⭐ EXPERT-REVIEWED  |  ✅ UPDATED 2026  |  🔒 NO SPONSORED BIAS  |  📚 EVIDENCE-BASED

Category: Business Insurance

  • Public Liability vs General Liability: Which One Do You Need?

    Public Liability vs General Liability: Which One Do You Need?

    Key Takeaways

    • General Liability primarily addresses third-party bodily injury and property damage arising from your operations, products, or completed work.
    • Public Liability is often synonymous with General Liability in the U.S. but represents a distinct, narrower coverage category in international markets like the UK or Australia.
    • Understanding the liability insurance differences is essential to prevent coverage gaps that could leave your business personally vulnerable to litigation.
    • Choosing business insurance requires a deep analysis of your physical footprint—whether you interact with the public on-site, off-site, or via digital products.
    • Many growing enterprises find that relying on a single policy is insufficient, necessitating a combined approach to manage varied risk exposures.

    Navigating the complex landscape of commercial risk management can feel like deciphering a foreign language, especially when the terminology seems to shift depending on who you ask. For many business owners, the debate between public liability vs general liability is a source of genuine confusion. While these terms are frequently used interchangeably in certain regions, they often denote specific risk protections that can significantly alter your financial safety net if a lawsuit occurs. As you work to choose business insurance that aligns with your operational reality, it is vital to peel back the layers of these policies to understand not just what they cost, but what they truly defend. This comprehensive commercial insurance guide serves to clarify your business liability coverage options and ensure you are protected against the unpredictable nature of third-party claims.

    Understanding the Core Purpose of General Liability Insurance

    General Liability (GL) insurance is widely considered the foundational pillar of any business risk management strategy. Often referred to as “slip-and-fall” insurance, its primary objective is to shield your company from financial ruin when a third party—someone not employed by your business—alleges that your actions, products, or services caused them physical harm or damaged their property. From a risk exposure standpoint, this is the first line of defense for almost every entity, from small local boutiques to massive manufacturing firms.

    The scope of General Liability is broad by design. It typically encompasses three main areas: bodily injury, property damage, and personal and advertising injury. Bodily injury coverage addresses medical expenses and potential legal fees if a customer trips over a stray cable in your office or slips on a wet floor in your retail space. Property damage coverage is equally critical; if one of your employees accidentally destroys a client’s high-end equipment while installing software, your GL policy is generally the mechanism that covers the replacement or repair costs.

    Furthermore, the “personal and advertising injury” component is a frequently overlooked but essential feature. This protects your business against claims involving libel, slander, or unintentional infringement of copyright during your marketing activities. In an age where digital presence is everything, a single aggressive social media post or an improperly cleared image used in a newsletter could trigger a lawsuit. General Liability provides the legal defense costs and settlement payouts necessary to navigate these high-stakes disputes without liquidating your business assets.

    It is important to note that General Liability is not a catch-all solution. It does not protect your own employees—that is the domain of workers’ compensation—nor does it cover professional errors or omissions, which require separate specialized policies. However, for the average business owner, the core purpose remains clear: it acts as a buffer against the everyday, physical, and communication-based risks that are inherent to being a public-facing entity. By integrating this into your broader insurance framework, you create a baseline level of stability that allows your operations to continue even when faced with unforeseen litigation threats.

    What Public Liability Insurance Actually Covers

    While the terms are often conflated in the United States, Public Liability insurance carries a specific, slightly more nuanced weight in global markets. In many jurisdictions outside of North America, Public Liability is explicitly designed to cover the legal liability a business incurs for injury or damage to members of the public. The fundamental difference between liability vs general liability in these contexts often boils down to how “operations” are defined. Public Liability is heavily focused on the physical interaction between your business activities and the public at large.

    Public Liability covers the costs of legal fees and compensation claims when a member of the public suffers a loss due to your business’s negligence. This might include an incident occurring at your business premises or at a location where you are performing work for a client. For instance, if you run a plumbing service and a pipe bursts due to a poorly soldered joint, damaging a client’s floorboards or furniture, a Public Liability policy is typically triggered. It is the insurance of “being out and about.”

    This coverage is particularly vital for contractors, tradespeople, and mobile service providers who move from site to site. Unlike a standard office-bound GL policy, Public Liability often requires careful scrutiny of where and how you conduct your work. If you are a consultant who visits clients’ homes, or a food truck operator serving crowds on the street, your risk exposure is dynamic. You are creating contact points with strangers in environments you do not control. Public Liability insurance is built to manage these “third-party interactions,” covering the medical costs or property repair bills that arise when your presence or work creates a hazard for an outsider.

    Moreover, Public Liability often extends to legal costs involved in defending yourself against claims, even if those claims prove to be frivolous or meritless. The cost of legal counsel alone can be enough to paralyze a small business, regardless of the ultimate verdict. Having a dedicated Public Liability policy provides the financial resources to hire experts, gather evidence, and sustain a vigorous defense. By focusing specifically on the relationship between your work and the public environment, this insurance ensures that your business can withstand the scrutiny of a claim and emerge on the other side without irreparable damage to your reputation or bottom line.

    Policy Type Primary Focus Best For
    General Liability Premises and operational hazards Retail stores, offices, and stationary businesses
    Public Liability Third-party contact at varying locations Contractors, tradespeople, and mobile service providers
    Combined Liability Comprehensive protection across all risks Growing enterprises with mixed-risk exposures

    Key Differences in Coverage Scope and Risk Exposure

    When analyzing the liability insurance differences between these two products, one must consider the geographical and environmental context of the risk. A General Liability policy is typically structured around the concept of “fixed premises.” If you operate a restaurant, your risk is centered on the dining room, the kitchen, and the walkway immediately adjacent to your storefront. The GL policy is mapped to these locations. In contrast, Public Liability often emphasizes the “activity” rather than the “address.” It follows the business entity, providing coverage wherever the work is performed, whether that is a residential kitchen, a busy event space, or a public thoroughfare.

    Another area where these policies diverge is in the handling of “Completed Operations.” General Liability specifically addresses risks that persist after a job is finished. For example, if you are an electrician who completes a wiring project in a home, and six months later that wiring causes a fire, General Liability provides coverage for those “completed operations.” While some Public Liability policies may offer similar protection, many are structured strictly for “active” incidents—meaning the accident must occur while you are physically present or performing the work. Misunderstanding this distinction can leave a business wide open to post-contract litigation, which can be devastating if you have moved on to new projects.

    Risk exposure analysis also requires looking at the nuance of “negligence.” Both policies operate on the principle that the business must be proven negligent, but the interpretation of negligence can differ based on policy wording. Public Liability policies are often highly responsive to specific event-based claims, such as someone slipping at an event you are sponsoring. General Liability, being more systemic, covers the broader umbrella of operations, including the potential for advertising injury—a risk factor that is often excluded entirely from standard Public Liability plans. If your business relies heavily on branding, marketing campaigns, and digital communication, a policy that ignores “personal and advertising injury” is inherently inferior, regardless of how well it covers your physical work sites.

    Finally, experts generally agree that the difference lies in the breadth of protection. A GL policy is a “macro” instrument, designed to cover the business as a holistic entity with multifaceted risks. Public Liability is a “micro” instrument, often favored for its precision in covering specific mobile or field-based operations. When evaluating which to choose, you aren’t just looking at the name on the policy—you are looking at the specific legal definitions within the fine print regarding “when” and “where” a covered occurrence must take place. Failure to align these definitions with your actual operational flow is one of the most common reasons businesses find themselves underinsured during a claim.

    Why Business Size and Industry Dictate Your Insurance Needs

    The size and industry of your company act as the primary filters through which you should view your liability insurance differences. A solopreneur who offers virtual coding services has a wildly different risk profile than a general contractor with thirty employees on a construction site. Consequently, the conversation regarding public liability vs general liability shifts based on the volume of foot traffic, the physical nature of the work, and the legal requirements imposed by local regulations or client contracts.

    For large companies with physical storefronts or high-traffic headquarters, General Liability is essentially non-negotiable. The sheer number of people passing through your doors on a daily basis creates a statistical certainty that, eventually, an injury or damage incident will occur. In these industries, the focus of the policy must be on broad-spectrum protection that covers premises liability, product liability, and the myriad of day-to-day accidents that happen in high-traffic settings. Larger businesses also face greater scrutiny from regulators, meaning that having a robust, standard GL policy is often a requirement for securing commercial leases or bank financing.

    Conversely, for the small business owner, such as a landscape architect or a mobile photographer, the risks are more episodic. These professionals operate in environments they don’t control. If you are doing work on a high-end estate, your risk of property damage is significantly higher than your risk of a slip-and-fall in your home office. Here, the industry dictates the need for specific liability coverage that follows you to the site. Many insurance providers offer “package” policies for these specific trades, which effectively combine the elements of Public Liability and General Liability into a single, manageable product. This simplification is a strategic advantage for smaller firms that may not have the capacity to manage multiple disparate insurance policies.

    Furthermore, industry-specific standards cannot be ignored. Some sectors, such as event management or hospitality, face strict “minimum liability coverage” requirements before they are even allowed to bid on contracts. In these cases, the choice between these policies is often made for you by external authorities. However, even when mandated, it is the responsibility of the business owner to ensure that the policy limit is sufficient to cover the worst-case scenario. A policy that meets the bare minimum for your industry may satisfy a contract, but it may fail to protect your personal assets in the event of a significant liability claim. Assessing the potential cost of a worst-case accident—such as a major fire or a debilitating injury—should always be the North Star of your insurance selection process, regardless of your company’s size.

    The Overlap: When Businesses Need Both Liability Policies

    In many complex operational environments, the lines between public liability vs general liability become blurred to the point that relying on one alone creates an unacceptable level of risk. This is the “overlap” zone, where the sophisticated business owner realizes that they require a layered defense. Most established firms, particularly those that maintain a permanent physical presence while also performing off-site project work, find that a dual-policy or an integrated commercial umbrella approach is the only way to ensure 360-degree coverage. Trying to stretch a single policy to cover both the risks of a fixed shop and the variable hazards of remote site work often results in “coverage thinning,” where the policy limits are exhausted far too quickly when multiple incidents occur.

    Consider a landscaping company that owns a nursery (fixed premises) but also handles large-scale commercial contracts at various office parks (mobile operations). If they rely solely on a basic Public Liability policy, they might find their coverage insufficient for the product liability risks associated with the fertilizers and materials they sell at their nursery. If they rely only on a standard General Liability policy, they might find that their insurer denies claims for work performed at specific high-risk commercial sites due to restrictive definitions of “premises.” In this scenario, the overlap is not a redundancy; it is a strategic necessity. By holding both, or by purchasing a comprehensive Business Owner’s Policy (BOP) that bridges these gaps, the business ensures that it is protected regardless of where the accident happens.

    The decision to hold both policies also serves as a powerful signal to potential clients and partners. In the world of B2B contracting, proof of comprehensive insurance is often a prerequisite for partnership. When you can present evidence of robust, multi-faceted liability coverage, you immediately signal that your business is well-managed and financially stable. It de-risks the relationship for your client, making them much more likely to choose you over a competitor who presents only a bare-minimum policy. This “insurance confidence” is a subtle but effective marketing tool in competitive bidding environments.

    Ultimately, the overlap period is where a business transitions from “just trying to get insured” to “actively managing enterprise risk.” It involves identifying the gaps where one policy ends and another begins. If you find yourself asking, “Is this covered?” and the answer is “maybe,” you are currently in an area of danger. Proactive business owners consult with their insurance agents to conduct a “gap analysis,” ensuring that there is no space between their General Liability and their other coverage forms where a lawsuit could fall through. Protecting your business is not about choosing the cheapest option; it is about building a cohesive structure that leaves no room for catastrophic financial loss.

    Geographical Variations: How Location Affects Policy Naming

    One of the most confusing aspects for business owners operating across state lines or international borders is the variation in terminology. When researching public liability vs general liability, you will quickly discover that insurance industry jargon is not universal. What a business owner in the United Kingdom or Australia calls “Public Liability Insurance” is often synonymous with what a business owner in the United States refers to as the “Premises Liability” portion of a Commercial General Liability (CGL) policy.

    In the United States, the term “General Liability” is the industry standard. It acts as an umbrella for a variety of risks, including bodily injury, property damage, and personal and advertising injury. However, if you move your operations to the UK, Canada, or Australia, you will find that “Public Liability” is the primary term used to describe coverage for third-party injuries or property damage. If you try to ask for “General Liability” in these regions, you may be met with confusion, as local brokers expect to hear “Public Liability” for standard third-party risk management.

    Furthermore, geographical location dictates the statutory requirements for these policies. In many jurisdictions, having public liability coverage is a de facto requirement for businesses that interact with the public, even if it is not explicitly written in the law as a “compulsory” insurance. For example, in many parts of Europe, hosting an event or opening a retail space requires proof of insurance before a local council will issue a business permit. Conversely, in certain U.S. states, general liability is not legally mandated for all businesses, though it is almost always required by commercial landlords and professional associations.

    Business owners must also be aware that the scope of coverage shifts based on geography. In some legal systems, public liability policies are strictly limited to accidents occurring on the business premises. In others, they may extend to cover activities conducted off-site, such as work performed at a client’s home or construction site. Understanding these regional nuances is critical when expanding your footprint, as your existing policy may not provide the territorial coverage you assume it does.

    Common Mistakes When Choosing Between Liability Policies

    The insurance marketplace is complex, and the pressure to save on premiums often leads business owners to make decisions based on incomplete information. When debating public liability vs general liability, the most common mistake is assuming that one policy is a direct, global substitute for the other. This misunderstanding can leave a business dangerously exposed.

    Another frequent error is “Under-insurance through categorization.” Many business owners categorize their risk based on their current revenue rather than their potential liability. For example, a consulting firm might assume they only need minimal coverage because they don’t have a high-traffic storefront. However, if that consultant visits a client’s site and accidentally causes significant property damage or triggers a lawsuit due to an unforeseen accident, the resulting legal costs could bankrupt the firm if their liability coverage was scaled only for “office-based” work.

    Relying solely on “bundled” policies without reading the fine print is a third major mistake. Many insurers offer a Business Owner’s Policy (BOP) that combines general liability with commercial property insurance. While these are cost-effective, they are often standardized. Business owners frequently fail to check if these policies include specific exclusions for their unique operations, such as cyber-related incidents, contractual liability, or specialized professional services. If the policy is too broad, it may not trigger in the specific scenario where your business is most vulnerable.

    Lastly, ignoring the “occurrence vs. claims-made” distinction is a trap many fall into. An “occurrence” policy covers incidents that happen during the policy period, regardless of when the claim is filed. A “claims-made” policy only covers claims filed while the policy is active. Choosing the wrong type—or failing to maintain “tail coverage” when switching providers—is a common oversight that results in businesses being left without a safety net when a past incident finally leads to a lawsuit.

    Policy Type Primary Focus Scope of Coverage Best For
    Commercial General Liability (CGL) Broad-spectrum business risk Bodily injury, property damage, advertising injury, and products-completed operations. Most standard businesses, retail shops, and companies with physical locations.
    Public Liability Third-party interactions Legal costs and compensation for injury or property damage to members of the public. Service providers, event organizers, and businesses with frequent public contact.
    Product Liability Post-sale risks Damages caused by defective products manufactured or sold by the business. Manufacturers, wholesalers, and e-commerce retailers.
    Professional Liability (E&O) Negligence in services Financial losses resulting from errors, omissions, or bad advice. Consultants, accountants, lawyers, and tech professionals.

    How to Assess Your Business Risk Profile for 2026

    As we head into 2026, the risk landscape for small and mid-sized businesses is evolving. Technology, remote work, and shifting consumer expectations mean that a static insurance strategy is no longer sufficient. To assess your risk profile accurately, start by performing a comprehensive audit of your operations.

    First, analyze your physical footprint. If you have moved from a traditional office to a hybrid or fully remote model, your liability needs have shifted. While you may have fewer visitors to an office, you may have increased reliance on contractors or third-party digital service providers. You must determine if your liability insurance covers damages caused by these external entities working on your behalf.

    Second, evaluate your contractual obligations. Take an inventory of every lease, vendor agreement, and client contract you hold. These documents often contain “indemnity clauses” that legally obligate your business to cover costs if something goes wrong. If your current policy does not provide enough coverage to satisfy these contractual requirements, you are in breach of contract and exposed to significant financial risk.

    Third, consider the nature of your growth. Are you expanding into new product lines or new markets? If your business model is shifting from selling goods to providing services, your risk profile is fundamentally changing. A policy that was designed to protect a retailer will not effectively cover a consultant. Use the transition period to consult with a risk advisor who can compare your historical claims data against your projected business activities for the coming year.

    Finally, factor in “reputational risk.” In the current social climate, public perception is a tangible asset. If a lawsuit or liability claim hits your business, the potential for brand damage is high. Ensure that your coverage limits are high enough to not only cover legal fees and settlements but to provide the financial cushion necessary to manage a potential crisis that could affect your long-term viability.

    Cost Comparison: Budgeting for Liability Protections

    Budgeting for insurance is rarely about choosing the cheapest option; it is about finding the optimal ratio between cost and protection. When comparing the costs of various liability policies, business owners should focus on the “total cost of risk,” which includes the premiums, deductibles, and the financial impact of potential coverage gaps.

    General Liability insurance costs are typically determined by three primary factors: the industry you operate in, your annual revenue, and your location. A restaurant, for instance, will pay higher premiums than a software developer because the physical risk of a slip-and-fall or foodborne illness is objectively higher. Public liability, when purchased as a standalone policy in regions where it is common, is often priced based on the volume of foot traffic or the nature of the events you host.

    To manage these costs effectively, consider the following strategies:

    • Raise your deductible: If your cash flow allows, taking on a higher deductible can significantly lower your annual premium. This is a common tactic for established businesses with healthy cash reserves.
    • Implement rigorous risk management: Insurance providers often offer discounts to businesses that demonstrate proactive safety measures, such as documented employee safety training, updated fire protection systems, or thorough site-access protocols.
    • Bundle when possible: Often, purchasing a Commercial General Liability policy alongside property and cyber insurance from a single carrier results in a “multi-line” discount.
    • Conduct annual reviews: Avoid the “auto-renew” trap. Business conditions change, and a policy that was appropriately priced last year may be over- or under-priced today.

    Always remember that the cheapest premium can be the most expensive mistake if a claim occurs and you find yourself under-insured. When budgeting, treat your insurance premium as a fixed operational cost that protects your primary revenue source, rather than an optional expense to be slashed when funds are tight.

    Evaluating Your Existing Coverage for Potential Gaps

    Your business insurance policy is a living document, yet many owners store it in a digital folder and forget about it until a crisis occurs. Periodically evaluating your coverage is essential to ensuring that your liability vs general liability choices still align with your business reality. The evaluation process should be systematic and rigorous.

    Begin by comparing your current “limits of liability” against the current industry standards for your specific niche. Limits that felt sufficient three years ago may now be below the market average. If a court awards damages that exceed your policy limit, your business assets—and potentially your personal assets—become vulnerable. Increasing your coverage limits is often much more affordable than you might expect, providing significant peace of mind for a marginal increase in premium.

    Look specifically for “endorsements” or “riders.” These are additions to your policy that cover specific, non-standard risks. For instance, if you have started offering delivery services, you may need an endorsement that specifically covers commercial auto liability, which is almost certainly excluded from a standard general liability policy. If you have begun hosting events, check for “liquor liability” exclusions. Many standard policies will deny a claim entirely if an incident involves alcohol, even if the policy itself is active.

    Check the definition of “insured” within your policy. Does it cover just you, the business entity, or does it extend to your employees, board members, and volunteers? If you have recently hired staff or entered a partnership, your existing policy might not automatically extend protection to these new stakeholders. Failing to update your policy to include all necessary parties can lead to a denial of coverage when it matters most.

    Finally, engage in a “what-if” scenario exercise. Take your policy document to your insurance agent and present them with three potential disaster scenarios—a major fire, a customer injury during a service delivery, and a data breach involving sensitive client information. Ask the agent directly: “Where would we be covered, and where would we have to pay out of pocket?” This exercise often reveals glaring gaps that aren’t apparent when simply reading the policy text.

    Frequently Asked Questions

    Is General Liability insurance mandatory for my business?

    In most jurisdictions, General Liability insurance is not strictly mandated by law for every type of business. However, it is effectively mandatory in practice because it is required by commercial landlords, major clients, and lenders. Operating without it often prevents you from signing leases or securing contracts with larger corporate entities.

    Can I get away with just having Public Liability insurance?

    If your business is very small and carries no inventory, has no physical office, and deals only with services provided off-site, you might feel that Public Liability is enough. However, this leaves you exposed to risks like advertising injury, damage to equipment while in your possession, and other liabilities covered by General Liability. It is usually more cost-effective to have a comprehensive CGL policy.

    How do I know if my business is under-insured?

    You are likely under-insured if your current liability limits are lower than the potential cost of a major lawsuit in your industry, or if you have recently added services, locations, or employees without updating your policy. If a claim would force you to dip into your personal savings or business operating capital, your coverage limits are likely too low.

    Does General Liability cover employee injuries?

    No, General Liability insurance does not cover employee injuries. Employee injuries are typically covered by Workers’ Compensation insurance, which is almost always a legal requirement for businesses with staff. Relying on General Liability for workplace injuries will result in a denied claim.

    What is the difference between “occurrence” and “claims-made” policies?

    An “occurrence” policy covers any incident that happens during the policy term, regardless of when the claim is filed, even if you cancel the policy later. A “claims-made” policy only covers you if the policy is active both when the incident occurs and when the claim is filed. Claims-made policies are often cheaper initially but carry more risk if not managed correctly.

    How often should I review my liability coverage?

    You should conduct a formal insurance review at least once per year. Additionally, you should review your coverage immediately whenever there is a significant change in your business, such as hiring new staff, moving to a new office, launching a new product line, or signing a major new contract with a high-value client.

    Conclusion

    Navigating the nuances of public liability vs general liability is more than a simple administrative task; it is a fundamental pillar of responsible business management. Whether you are a small startup or a scaling enterprise, the insurance choices you make today will define your ability to weather the storms of tomorrow. By understanding the geographical, operational, and financial dimensions of these policies, you move from a state of passive compliance to active risk stewardship.

    Do not wait for a legal challenge or an unexpected accident to discover the limitations of your current coverage. Take the time to audit your risk profile, consult with qualified professionals, and ensure that your liability protections are as robust as the business you have worked so hard to build. Protecting your assets, your reputation, and your employees starts with the right coverage. Review your policy today and secure your business’s future.

    By insureiqguru Editorial Team
  • Business Interruption Civil Authority: What You Need to Know

    Business Interruption Civil Authority: What You Need to Know

    Key Takeaways

    • Civil authority coverage provides financial protection when government mandates prevent access to your business property, even if your physical location remains undamaged.
    • This extension is typically found within commercial property insurance policies as a specialized supplement to standard business interruption insurance.
    • Most policies require proof that a covered peril—such as fire, wind, or civil unrest—occurred in the immediate vicinity to trigger the mandate.
    • Navigating commercial property insurance claims involving civil authority requires precise documentation of government-issued closure notices and financial loss timelines.
    • Understanding specific policy sub-limits, waiting periods, and geographic proximity requirements is essential to managing your expectations during a claim.

    When a natural disaster strikes, a fire destroys a neighboring building, or a sudden public safety threat forces authorities to cordon off a city block, your business may grind to a halt through no fault of your own. Even if your physical storefront or office remains completely unscathed, the inability to operate because you cannot reach your property can be financially devastating. This is where business interruption civil authority coverage becomes a vital component of your corporate risk management strategy. For many business owners, standard coverage feels like an invisible safety net until an unexpected government order forces the doors shut. By understanding the intricacies of civil authority coverage, business leaders can better prepare their organizations for the sudden, unpredictable interruptions that characterize the modern commercial landscape. This guide explores the essential components of these extensions, how they interact with broader policies, and what you need to track to ensure your recovery process remains efficient.

    What Is Civil Authority Coverage in Business Insurance?

    Civil authority coverage is an essential extension often found within the broader framework of business interruption insurance. At its core, this coverage is designed to provide financial relief when a government entity, such as a municipal government, state agency, or federal authority, prohibits access to your business premises due to an emergency event. Unlike standard business interruption policies, which typically require direct physical loss or damage to the insured property itself, civil authority coverage acts as a bridge for businesses that are “locked out” by official action.

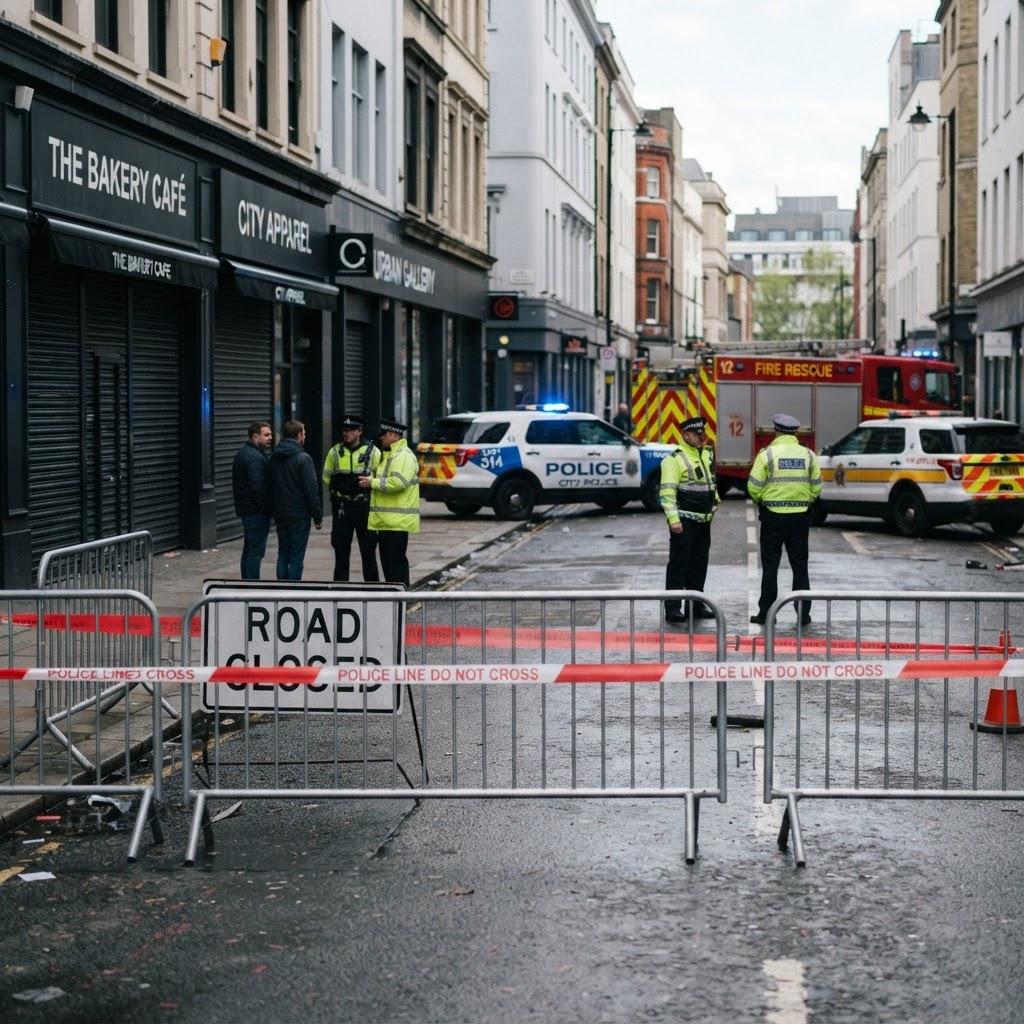
    Think of it as a form of protection against the ripple effects of a disaster. For example, if a major chemical leak occurs three buildings away, local emergency services may establish a security perimeter that effectively prevents customers, staff, and deliveries from reaching your business. Even though your building sustained no damage, you are essentially barred from conducting revenue-generating activities. Because there was no physical damage to your insured property, a standard business interruption claim might be denied. However, because a formal government order has restricted access, the civil authority clause serves as the policy trigger.

    It is important to recognize that this is not a standalone policy but rather an extension of your existing commercial property insurance. Most policies categorize this as an “Additional Coverage” or “Coverage Extension.” While the core purpose is to replace lost income and pay for continuing expenses during the period of restoration, the definition of what constitutes a “civil authority” can be quite specific. Typically, it refers to a police department, fire department, military branch, or civil defense agency authorized to enforce public safety.

    In practice, this coverage covers the income you would have reasonably expected to earn had the order not been in place. This includes net profit, ongoing fixed costs—such as rent, payroll, and insurance premiums—and sometimes even the costs associated with reopening. Because every insurance carrier drafts its own language, the specific geographic triggers and the duration of the coverage period can vary significantly. Some policies may require the order to be in place for a minimum number of hours before coverage begins, while others may apply immediately upon the issuance of the directive. Understanding these definitions is the first step in assessing whether your current policy is adequate for your specific location and industry risks.

    How Civil Authority Coverage Triggers Benefit Payments

    Triggering a claim for business interruption civil authority coverage is a structured process that relies heavily on the technical language of your policy. It is rarely as simple as merely closing your doors; you must satisfy specific conditions set by your insurer to demonstrate that the closure was a direct result of an qualifying event. Generally, the mechanism of triggering these benefits follows a logical sequence: the occurrence of a covered peril, the subsequent government action, and the physical restriction of your property.

    First, most policies require that the government order be issued in response to a “covered peril.” If your policy covers fire, windstorm, or explosion, the civil authority order must be linked to one of these events occurring in the immediate vicinity of your premises. If the government shuts down your street for a parade or a planned infrastructure upgrade, civil authority coverage does not apply. The trigger requires an emergency situation that poses a threat to public safety.

    Second, the issuance of a formal order is paramount. Insurance adjusters will look for documentation showing that a competent authority—such as a Mayor’s office, the Police Chief, or the Fire Marshall—has issued an official directive preventing access. This can sometimes be in the form of a written proclamation, a barricade announcement, or even an official public broadcast. If there is no clear evidence of an order, or if the closure is merely a voluntary decision by the business owner based on safety concerns, the insurer will typically deny the claim. You must be able to prove that you *wanted* to be open, but were legally prevented from doing so.

    Third, the geographic proximity requirement must be met. Policies define “vicinity” or “immediate area” with varying degrees of strictness. Some policies might limit the trigger to properties within a one-mile radius, while others may be more flexible. If the disaster occurs ten miles away, even if it leads to a road closure that affects your business, the insurer may argue that the event is too remote to trigger the coverage.

    Once these conditions are satisfied, the insurer begins calculating the period of restoration. This is the timeline during which your benefits are paid. It typically begins after a specific “waiting period” (which could be anywhere from 24 to 72 hours) and lasts until the order is rescinded or until a specific maximum duration (often two to four weeks) is reached. Because the waiting period is often significant, it is vital to maintain accurate records of exactly when the restriction began and ended. Maintaining a copy of the government order or a log of police activity in front of your location is a best practice for streamlining the claims process.

    Understanding the Difference Between Civil Authority and Business Interruption

    Distinguishing between standard business interruption insurance and civil authority coverage is vital for anyone managing commercial property insurance claims. While they are intrinsically linked, they address different causal factors for financial loss. Business interruption insurance is primarily concerned with *direct* consequences, while civil authority acts as a safety valve for *indirect* consequences that nonetheless halt your ability to earn revenue.

    Standard business interruption coverage serves to replace the income your business loses after a direct physical loss—such as a fire, storm, or burst pipe—occurs *at your specific premises*. It requires that your building or the equipment inside it be damaged to the point where you cannot operate. In these cases, the “trigger” is the physical damage itself. If a fire burns your warehouse, the loss of business income stems from your inability to fulfill orders or house your inventory due to that specific, localized damage.

    Conversely, civil authority coverage does not require any damage to your physical assets. It addresses scenarios where the “damage” is effectively to the accessibility of your location. Imagine a fire occurs at a neighboring gas station. Your own building is perfectly intact, the electricity is running, and your inventory is safe. However, the local fire department declares the entire block a hazardous zone and prohibits all traffic, including your customers and staff, from entering the area. In this instance, your standard business interruption insurance will not pay out because your property hasn’t been damaged. Civil authority coverage becomes the primary mechanism for recovery, as it acknowledges that the government’s intervention—caused by the fire next door—is the root cause of your lost income.

    The table below summarizes the core operational differences between these two coverages.

    Feature Standard Business Interruption Civil Authority Extension Best For
    Trigger Event Direct physical damage to your premises Government-mandated access restriction Comprehensive protection
    Proximity Requirement N/A (Damage must be on-site) Immediate vicinity of property Geographically vulnerable sites
    Dependency Primary Coverage Secondary/Extension Total risk mitigation

    It is critical to note that you cannot “double dip.” If an event occurs that both damages your property and prompts a government closure, the insurer will calculate the loss under the primary business interruption clause. Civil authority is intended to fill the gap where standard coverage falls short, ensuring that you are not left financially vulnerable simply because the damage happened “next door” rather than “in your office.” By understanding this distinction, you can better audit your current insurance policy limits to ensure that both areas of risk are sufficiently covered.

    Common Situations Where Civil Authority Coverage Applies

    Civil authority coverage is most frequently utilized in response to sudden, unpredictable events that necessitate a fast and protective reaction from local officials. While every event is unique, certain scenarios consistently trigger these types of claims. Being aware of these common occurrences can help business owners conduct a more accurate risk assessment of their operating environment.

    One of the most common applications involves severe weather events. If a major storm hits a coastal region, municipal authorities often issue mandatory evacuation orders. These orders are not requests; they are directives that force businesses to shutter their operations to protect human life. Even if the business remains standing once the storm clears, the period during which the evacuation order was in effect is covered under the civil authority provision, provided the order was issued due to the dangerous conditions of the storm.

    Another frequent scenario involves infrastructure failures or industrial accidents. A water main break that floods a downtown intersection, a gas line explosion in a nearby industrial park, or a chemical spill in a commercial district can all lead to an immediate and total lockdown of the area by the police or fire department. Because these events present a tangible risk of harm, the government is authorized to declare the area “off-limits.” Since your business occupies space within that restricted perimeter, the financial loss you suffer during the time the perimeter is guarded is eligible for recovery.

    Civil unrest also represents a recurring, if volatile, catalyst for civil authority claims. During periods of widespread public protest or social instability, local governments may implement curfews or cordon off specific blocks to maintain public order and prevent property damage. If your business is located within the zone where the government has prohibited movement, you may be able to claim lost income. However, it is essential to check your policy language here; some policies include specific “civil commotion” or “riot” exclusions that may apply depending on the nature of the events.

    Finally, unexpected public health directives have emerged as a significant, albeit complex, category. While historical policies were largely designed to address physical damage, some modern interpretations and endorsements have grappled with how government-mandated closures during public health emergencies are treated. Generally, unless the policy specifically covers “communicable disease” or “virus” triggers, many standard civil authority clauses will not provide coverage for lockdowns related solely to health. This highlights the importance of working closely with a broker to review the specific “peril” requirements in your policy. If your business is located in an area prone to specific environmental or security risks, discussing these potential scenarios with your insurance advisor before a loss occurs is the most effective way to ensure your policy isn’t just a document, but a functional tool for business continuity.

    Key Exclusions and Limitations to Watch For

    While civil authority coverage provides a critical layer of protection, it is rarely an unlimited safety net. Insurance carriers incorporate specific exclusions and limitations to define the boundaries of their risk. Failing to account for these nuances can lead to significant coverage gaps when you need them most. The most sophisticated business owners are those who audit their policies with a critical eye for what is *not* covered.

    First, the “waiting period” is a classic limitation. Many commercial property insurance claims involving civil authority are subject to a deductible in the form of a time-based wait. For example, a policy might state that coverage for civil authority does not kick in until 72 hours after the order is issued. If the government restricts access for only 48 hours, you would be responsible for the entire loss. For businesses operating on thin margins, a three-day, non-reimbursable shutdown can still represent a massive hit to cash flow. Always verify the waiting period duration in your specific policy declaration page.

    Second, the geographic limitation is a frequent source of contention. Many policies specify that the triggering event must occur within a certain distance—often 1 mile or 5 miles—from your premises. If an explosion occurs 10 miles away, forcing the closure of roads that your employees use to reach your office, the insurer might argue that the event is too geographically removed to satisfy the “immediate vicinity” requirement. Understanding the exact scope of this proximity requirement is vital, especially for businesses in urban environments where a blockade several blocks away could effectively cut off your entire customer base.

    Third, look for “peril” exclusions. Civil authority coverage is generally tied to the same perils covered by your property policy. If your policy covers fire and windstorm, but excludes flooding, and a government order is issued to close your area due to rising floodwaters, your claim will almost certainly be denied. Because civil authority is an extension, it inherits the limitations of the underlying coverage. If the primary cause of the government mandate is an excluded event, the extension will not override that exclusion.

    Fourth, keep a close watch on your “policy limits.” Civil authority is often subject to a sub-limit. Even if your overall business interruption limit is $1,000,000, your policy might cap the civil authority extension at a much smaller amount, such as $50,000 or $100,000. These sub-limits can be exhausted rapidly if the government order remains in effect for an extended period.

    Finally, be wary of the “causation” requirement. The order must be a *direct result* of the covered peril. If the police close your street for an unrelated reason—such as a film shoot or a street fair—there is no coverage. Adjusters will often request the specific official documentation or police reports that led to the restriction to verify the cause. If the stated reason for the closure is bureaucratic or discretionary rather than an emergency response to a covered peril, the financial loss will likely fall outside the scope of your policy protections. Thoroughly vetting these limitations during the policy renewal phase is essential to avoiding unpleasant surprises.

    How to Document a Claim for Restricted Business Access

    When a government entity restricts access to your place of business, the burden of proof rests heavily on the policyholder. Successfully navigating commercial property insurance claims involving civil authority coverage requires meticulous, contemporaneous documentation. You cannot rely on memory or generalized statements of financial loss; you must provide a clear, forensic trail that links the specific government order to the inability to conduct business operations.

    First and foremost, secure a digital and physical copy of the actual government mandate. Whether it is an executive order, a local police blockade, or a health department closure notice, the specific language contained within the document is critical. Insurance adjusters will examine whether the order was issued due to “direct physical loss or damage” to property in the immediate vicinity of your premises. Ensure you have the exact date, time, and geographic scope of the order.

    Next, maintain a detailed log of your business operations during the restriction. This log should categorize the specific ways in which the government order prohibited access. For instance, if a road closure prevented employees from reaching the office, document the specific shift times affected and the number of personnel unable to perform their duties. If the restriction prevented customers from entering your retail space, document the average foot traffic for similar time periods in previous years compared to the restricted period.

    Financial record-keeping must be granular. Do not simply submit a profit and loss statement for the month. Instead, isolate your daily revenue during the civil authority event. Use historical data to create a “but-for” projection—what your revenue would have been had the restriction not been in place. When seeking reimbursement under business interruption civil authority, you must also be prepared to disclose any expenses saved because of the closure, such as un-incurred utility costs or temporary staff reductions. Transparency in these calculations prevents the perception of padding your claim.

    Finally, utilize photographic and video evidence if possible. While you should never breach a legal blockade, document the perimeter of the restriction to show the physical limitations imposed on your business premises. If your facility remained open but empty because of the civil order, interior photos capturing an idle facility serve as powerful evidence of the business interruption.

    Determining the Right Coverage Limits for Your Operations

    Many business owners mistakenly assume their business interruption insurance is a catch-all safety net. In reality, sub-limits often apply specifically to civil authority coverage. These sub-limits are frequently much lower than the general business interruption limit, sometimes capped at a flat dollar amount or a limited period of time, such as 14 or 30 days. Understanding these constraints is vital during the policy renewal phase.

    To determine the appropriate coverage levels, you must perform a comprehensive business impact analysis. Start by calculating your “worst-case scenario” for a sustained government-mandated shutdown. How long could your business remain closed before cash flow becomes critical? Consider your fixed costs—rent, debt service, essential salaries, and insurance premiums—that persist even when revenue drops to zero.

    You should also factor in the “geographic risk profile” of your location. Businesses located in urban centers, near major transit hubs, or in areas prone to industrial accidents may face a higher frequency of civil authority events. If your business is located within one mile of a major chemical plant or a high-traffic highway, your exposure to an event that triggers a perimeter closure is statistically higher than a business in a low-density suburban office park.

    Coverage Type Typical Focus Best For
    Standard Business Interruption Losses from damage to your property Physical destruction of your assets
    Civil Authority Coverage Losses from restricted access (nearby) Businesses impacted by regional disasters
    Extra Expense Coverage Costs to relocate or expedite operations Businesses that must stay open at any cost

    When reviewing your policy with your broker, ask specifically about the “waiting period” or “deductible” associated with your civil authority provisions. Some policies require a 72-hour delay before the coverage kicks in. If your operations typically recover from minor disruptions within 48 hours, a 72-hour waiting period might effectively render your coverage useless. Adjusting these limits and waiting periods is a strategic decision that balances your premium costs against your actual risk exposure.

    The Role of Government Orders in Insurance Disputes

    The core of most insurance disputes regarding civil authority coverage hinges on the definition of “direct physical loss or damage.” Insurance carriers often argue that a government order is only enforceable if it was issued in response to actual property damage in the surrounding area. For example, if a fire destroys a building two blocks away, and the fire department shuts down the surrounding streets to fight the blaze, that is a classic trigger for civil authority coverage. The damage exists, and the authority has restricted access to protect the public.

    However, disputes frequently arise when the government order is issued as a precautionary measure rather than as a reaction to immediate physical destruction. During public health crises or civil unrest, government officials may issue broad proclamations that restrict movement across entire regions. Insurance companies may contest these claims by arguing that the civil authority order was not a direct result of damage to adjacent property, but rather an administrative decision based on generalized risk.

    This “proximate cause” issue is a frequent battleground. If you find yourself in a dispute, it is essential to review the specific language of your insurance contract. Does the policy require “physical loss to property” or simply “an act of civil authority”? Policies with broader language are generally more favorable to the policyholder. Furthermore, the distance from your premises to the site of the damage matters. Most policies stipulate a specific radius (e.g., one mile or five miles) for the damage to be considered “proximate” enough to warrant coverage.

    If a claim is denied based on the nature of the government order, you should involve legal counsel specializing in insurance coverage. They can help analyze whether the carrier’s interpretation of the policy is overly restrictive. Often, carriers rely on standard denial letters that may not adequately account for the nuances of your specific local mandates. Challenging an initial denial often requires showing that the government order was a direct, localized response to a physical hazard, effectively linking your business’s inability to operate to the protected property nearby.

    Proactive Steps to Take Before a Civil Authority Event Occurs

    The best time to prepare for a civil authority disruption is long before the police tape goes up. Business resilience planning should integrate insurance strategy as a core component of your risk management framework. First, review your existing policy to map out your specific coverage thresholds. Do not wait for an emergency to discover that your civil authority sub-limit is insufficient for your monthly overhead.

    Second, develop a “digital redundancy” plan. Many businesses are forced to close during civil authority events because their physical infrastructure is inaccessible. If your business can operate remotely, ensure that your data is backed up in the cloud and your employees have the remote access tools necessary to maintain operations. If your business can prove that it shifted to remote work immediately following a closure order, you can often mitigate the extent of your business interruption claim, which insurers generally view favorably.

    Third, establish a communication protocol with your local authorities. Knowing which department (police, fire, public health, or department of transportation) is likely to issue orders in your area helps you understand the nature of the risks you face. Should an event occur, having a designated point of contact within your business who is responsible for obtaining written documentation of closures is essential. They should be tasked with securing copies of press releases, official notices, and any subsequent updates that might change the scope or duration of the restriction.

    Finally, engage in periodic “tabletop exercises” with your management team. Simulate a scenario where a neighboring property is closed due to a major event and walk through the steps required to file a claim. By practicing the collection of financial and operational data, you eliminate the confusion and panic that typically accompany a crisis. A proactive approach not only streamlines the claims process but also demonstrates to your insurer that you are a well-managed entity, which can potentially lead to more favorable terms at renewal.

    Frequently Asked Questions

    Does civil authority coverage pay for all lost profits during a closure?

    Generally, civil authority coverage is intended to replace net income that would have been earned, along with continuing normal operating expenses. However, this is subject to your policy’s specific sub-limits, the duration of the order, and the “waiting period” stipulated in your contract. It rarely covers 100% of potential growth, but rather focuses on stabilizing the business based on historical performance.

    What if my business can still operate online while the physical location is closed?

    Insurers typically look at the “net” impact on your business. If your online sales successfully offset the losses from your physical storefront, you may find that you have a reduced claim or no claim at all. However, if your physical operation accounts for the vast majority of your revenue, you may still be entitled to a significant portion of your lost income, provided you can document the direct impact of the access restriction.

    How far away can the “physical damage” be for me to make a claim?

    Most commercial property insurance policies specify a geographic radius within which the “direct physical loss or damage” must occur for your civil authority coverage to trigger. This is commonly limited to one mile or five miles, but it varies significantly by policy. Always check the “Civil Authority” section of your declarations page for the exact language regarding distance.

    Do I need to prove my business was profitable before I can file a claim?

    While having a profitable business history makes the calculation of “lost income” straightforward, it is not always a strict requirement. If your business was in a startup phase or experiencing a temporary downturn, insurers will use alternative benchmarks, such as industry standards or projected budgets, to determine the “but-for” income. The documentation remains key, regardless of current profitability.

    What happens if the government order is extended?

    Most civil authority coverages have a maximum time limit, often stated as a consecutive number of days (e.g., 14, 30, or 60 days). If the government mandate exceeds this limit, your coverage will generally cease at the end of the policy’s specified term, even if the closure remains in effect. Review your policy’s “period of restoration” to understand how it applies to civil authority versus standard physical damage.

    Can I claim expenses for moving my operations to a temporary location?

    You may be able to claim these expenses under “Extra Expense” coverage, which is often bundled with or sits alongside civil authority coverage. If you must set up shop elsewhere to minimize the interruption caused by a government-mandated closure, check your policy to see if “reasonable and necessary” extra expenses are reimbursable. Keeping detailed receipts for all temporary relocation costs is mandatory for these claims.

    Conclusion

    Navigating the complexities of business interruption civil authority coverage requires more than just a standard insurance policy; it requires a proactive strategy rooted in documentation, risk awareness, and precise policy management. As we have explored, government-ordered access restrictions can threaten the financial viability of even the most resilient enterprises. By understanding the specific triggers of your policy—such as the requirement for physical damage in your vicinity and the constraints of your geographic sub-limits—you can move from a reactive posture to a position of control.

    Do not wait until a crisis occurs to review the fine print of your commercial property coverage. Assess your current risk profile, communicate with your insurance broker about potential coverage gaps, and ensure your operational records are robust enough to withstand the scrutiny of a claims adjuster. Being prepared is the most effective way to protect your business assets and ensure your doors can reopen, no matter what external challenges arise.

    If you are unsure whether your current business interruption policy provides sufficient protection against civil authority events, schedule a comprehensive audit with your broker today. Secure your operations, safeguard your revenue, and stay informed on the evolving landscape of commercial insurance.

    By insureiqguru Editorial Team
  • Business Interruption Waiting Period: How to Choose the Right One

    Business Interruption Waiting Period: How to Choose the Right One

    Key Takeaways

    • The business interruption insurance waiting period acts as a time-based trigger before your coverage begins, rather than a monetary cost.
    • Distinguishing between a time-based waiting period and a traditional dollar-based business insurance deductible is critical for accurate risk assessment.
    • Your choice of waiting period directly impacts the speed of your recovery; shorter periods provide faster cash flow but higher premiums.
    • Businesses with low operating margins should carefully weigh the potential for a “gap” in coverage against the cost of the policy.
    • Balancing your business income waiting period requires analyzing historical data on typical recovery timelines for common local perils.

    When disaster strikes your operations—whether through a fire, a burst pipe, or a natural catastrophe—the primary concern for most owners is immediate survival. While standard property insurance covers the physical repair of your building and equipment, it does not replace the revenue lost while your doors are closed. This is where business interruption insurance becomes a lifeline. However, understanding the policy nuances is just as important as having the coverage itself. One of the most critical, yet often misunderstood, components of these policies is the business interruption insurance waiting period. This specific provision dictates exactly when your coverage kicks in, serving as a time-based threshold that determines the scope of your financial protection. For business owners, choosing the right duration for this period is not merely a technical decision; it is a strategic financial move that shapes your organization’s resilience in the face of an unforeseen closure.

    What Is a Business Interruption Waiting Period?

    To understand the business interruption insurance waiting period, it is helpful to view it as a “time deductible.” Unlike standard insurance policies where you pay a specific dollar amount out of pocket before the insurer covers a loss, a business interruption waiting period is measured in hours or days. It represents the period during which your business must be unable to operate due to a covered peril before the insurance company begins paying for your lost income and ongoing fixed expenses. For instance, if your policy includes a 72-hour waiting period, your business must remain non-operational for three full days following the incident before you are eligible for any reimbursement of lost profits.

    This “time element,” as it is often referred to in the industry, exists to prevent insurers from having to process and pay out claims for minor, short-term inconveniences. Insurance companies design these policies to protect against significant, disruptive events that threaten the long-term viability of a business, rather than minor interruptions that last only a few hours. By implementing an insurance waiting period explained by the contract terms, carriers effectively reduce the administrative burden of handling hundreds of micro-claims, which in turn helps keep premium costs more manageable for policyholders across the board.

    The waiting period applies to the business interruption portion of your policy, which typically covers your “net income” (the profit you would have made had no loss occurred) plus your “continuing operating expenses” (such as rent, payroll, taxes, and debt interest). Even if your business suffers a direct physical loss on day one, the insurer will look at the clock. If the disruption resolves itself within the span of your designated waiting period, you will essentially bear the cost of that closure entirely on your own. If the closure extends beyond that timeframe, the policy coverage generally triggers retroactively to the start of the event, though this can vary depending on your specific policy language. This mechanism makes the business income waiting period a fundamental variable in your business continuity planning, as it defines your own “self-insured” window of time.

    For many small businesses, a 24-hour waiting period might seem attractive, but the practical implications depend on the nature of your operations. If you operate a high-volume retail storefront, a 48-hour disruption could result in significant lost sales that you can never recover. Conversely, a large manufacturing plant might have the inventory buffers or backup production lines to handle a two-day shutdown with minimal impact on their bottom line. Therefore, defining the waiting period requires a deep understanding of your business’s specific dependency on daily, uninterrupted operations. It is not a “one size fits all” choice, but a tactical selection based on your organization’s risk tolerance and financial stability.

    How the Waiting Period Differs from a Standard Deductible

    A frequent point of confusion for many business owners is the relationship between the business interruption insurance waiting period and the standard business insurance deductible. While both serve the purpose of shifting some risk back to the policyholder, they function through entirely different mechanisms. A standard deductible is a monetary threshold. If you have a $5,000 deductible on your property policy, and you incur $50,000 in damage, your insurance company will pay $45,000 after you pay the first $5,000 out of pocket. It is a straightforward reduction of the total claim payout.

    In contrast, the business income waiting period is a temporal threshold. It does not reduce the payout amount directly; rather, it dictates the eligibility of the claim based on the duration of the interruption. If you have a 48-hour waiting period and your business is closed for 72 hours, the insurer will compensate you for the loss of income generated during that total 72-hour period (depending on specific policy wording), but you are responsible for absorbing the revenue loss for the first 48 hours without any insurance assistance. This is why it is vital to contrast waiting period vs deductible when building your risk management profile. A deductible impacts your cash flow by requiring an immediate cash outlay at the time of repair or replacement, whereas a waiting period impacts your cash flow by leaving you without revenue for a specific duration of time.

    The distinction is also vital when considering the business interruption time element. Because the waiting period is time-based, it can be much more volatile than a fixed-dollar deductible. A dollar deductible is static; you know exactly how much you are on the hook for if a loss occurs. A time-based waiting period, however, is subject to the unpredictable nature of repairs and supply chain logistics. If you underestimate the time it takes to restore your operations, a short waiting period could quickly turn into a long, expensive period of downtime for which you are financially liable.

    The table below provides a quick comparison of these two core insurance concepts:

    Feature Standard Insurance Deductible Business Interruption Waiting Period
    Core Metric Monetary Value (e.g., $1,000) Time Value (e.g., 24 hours)
    Purpose Reduces claims frequency/cost Establishes eligibility for coverage
    Financial Impact Direct cash outflow for repairs Loss of revenue during downtime
    Best For Managing property repair costs Managing business continuity risk

    Understanding these differences allows you to structure your insurance portfolio more effectively. Some businesses may choose a higher dollar-value deductible in exchange for a shorter time-based waiting period, effectively buying peace of mind that they won’t be without income for long, even if they have to pay a bit more toward the physical repair costs. Others, confident in their ability to absorb short-term dips in revenue, might choose a longer waiting period to lower their overall insurance premiums. Balancing these two variables is a sophisticated approach to risk management that goes beyond merely shopping for the lowest policy rate.

    Why the Waiting Period Duration Matters for Cash Flow

    Cash flow is the lifeblood of any business, and the business interruption insurance waiting period is a direct variable in your cash flow model. Every day your business is not operating is a day where you are potentially hemorrhaging revenue while still being expected to cover fixed costs like payroll, rent, and utility commitments. When choosing a waiting period, you are essentially determining how much of a cash flow “buffer” you can afford to maintain in your operating accounts in the event of an emergency.

    If you choose a waiting period that is too long, you are placing a significant burden on your business’s emergency reserves. For example, if your business generates high daily revenue and you have a seven-day waiting period, you would need to be prepared to cover an entire week of lost income yourself. For a company with slim margins or high daily overhead, this could be the difference between a temporary setback and insolvency. The insurance waiting period explained in your policy is not just a line item; it is a potential liability that must be backed by liquid capital.

    Conversely, selecting a very short waiting period—such as 6 or 12 hours—can ensure that your income loss is covered almost immediately. However, this comes with the reality that you are paying for that protection through higher monthly premiums. If your business has a highly predictable cash flow or if you operate in a low-risk environment, paying for a 6-hour waiting period might be an inefficient use of capital. The key is to map your cash flow cycles against the potential length of a disruptive event. Ask yourself: how long can we survive without our primary revenue stream before we hit a liquidity crisis?

    Consider the cumulative impact of an interruption. Often, businesses focus only on the lost revenue during the period of restoration. However, the business interruption time element also includes the “period of indemnity,” which is the amount of time the policy covers for your business to return to its pre-loss level of operations. If your waiting period is long, you have a larger gap to fill. If you are forced to spend your cash reserves just to survive the waiting period, you may find that you lack the capital needed to jumpstart your operations once the property damage is fixed. This is why experts generally recommend that businesses with lower cash reserves opt for shorter waiting periods if possible, as it preserves their liquidity for the post-disaster recovery phase, where every dollar counts toward regaining market position.

    Furthermore, consider your accounts receivable cycles. If you operate on a “pay on delivery” basis, a waiting period hit is immediate and painful. If you operate on net-30 or net-60 day terms, the impact of a 48-hour disruption might not be felt until weeks later, when those specific invoices aren’t paid. A business owner must look at their cash conversion cycle when determining how long they can safely wait for an insurance payout. Your waiting period selection should align with the reality of your specific industry’s payment timing, ensuring that your insurance truly protects the flow of money into your business when it is needed most.

    Factors to Consider When Choosing Your Waiting Period

    Choosing the right waiting period for your business is a strategic decision that requires a multi-faceted analysis of your operations. There is no one-size-fits-all answer, but by evaluating your unique organizational characteristics, you can identify the “sweet spot” that provides adequate protection without unnecessary cost. Start by looking at your business’s physical vulnerability. If you operate in a region prone to natural disasters like floods, hurricanes, or wildfires, the likelihood of a long-term shutdown is statistically higher. In these scenarios, the difference between a 24-hour and a 72-hour waiting period might seem small in the moment, but it represents a significant portion of your financial risk profile.

    Another crucial factor is the nature of your supply chain. A business that relies on a “just-in-time” inventory model is highly sensitive to disruptions. If a fire at a distribution center prevents you from getting the parts you need to assemble your products, your business effectively stops, even if your physical storefront remains pristine. In this case, your choosing waiting period insurance strategy should prioritize a shorter interval. If you can’t source your inputs quickly, a 12-hour or 24-hour waiting period is often the safest bet to ensure that your business continuity isn’t compromised by someone else’s inability to deliver.

    Historical data also plays a major role. Many business owners have experienced minor power outages or small maintenance-related closures. Think about how long those past interruptions lasted. If your historical “worst-case scenario” for a closure was 36 hours, choosing a 24-hour waiting period makes sense, as it ensures you are covered for anything that exceeds your typical disruption. However, if your history shows that most disruptions are resolved in 4-6 hours, then a 24-hour waiting period is likely sufficient and saves you money. Being honest about the typical length of recovery for your specific industry is essential for data-driven decision-making.

    Next, evaluate your business’s elasticity and backup options. Do you have a secondary location? Can your team work remotely? If your operations are highly elastic, you might be able to shift production or service delivery to a different channel within a few hours. A company with high redundancy might be comfortable with a longer waiting period, knowing they can minimize the total impact of a localized event. In contrast, a business with a “single point of failure”—like a restaurant that cannot function without its commercial kitchen—should prioritize a shorter waiting period, as they have little room to pivot if the primary facility goes down.

    Finally, weigh the competitive landscape. If you are in a crowded, high-competition market, every hour you are closed allows your competitors to capture your customers. In these industries, the cost of a long waiting period isn’t just the lost revenue; it’s the potential loss of market share and customer loyalty. Choosing waiting period insurance that is as short as possible can be a defensive measure, allowing you to focus on marketing and customer retention immediately after a disaster rather than worrying about the immediate financial hole in your budget. By documenting these factors, you can approach your insurance broker with a clear rationale for the policy terms that best suit your specific business needs.

    How Waiting Periods Affect Your Insurance Premiums

    The relationship between your insurance waiting period and your premium is a classic example of the “risk-versus-reward” trade-off in the insurance marketplace. Generally speaking, the shorter the waiting period, the higher your annual premium will be. This is because the insurance company is taking on more liability. By agreeing to cover your income losses starting after only 12 or 24 hours, the insurer accepts the risk of paying out for a larger number of smaller events. From the underwriter’s perspective, this increased frequency of potential claims necessitates a higher premium to ensure the pool of funds remains solvent.

    Conversely, choosing a longer waiting period—such as 72 hours or even a full week—effectively signals to the insurer that you are willing to manage the minor, short-term interruptions yourself. By self-insuring the first few days of a potential outage, you are reducing the administrative and financial burden on the insurance carrier. In exchange for this risk-sharing, the insurer typically offers a discount on your premiums. For businesses that are financially stable and have cash reserves, this can be an effective way to lower overhead costs without sacrificing the protection needed for truly catastrophic, long-term events.

    However, it is important to avoid a common mistake: assuming that doubling your waiting period will cut your premium in half. Insurance pricing is rarely linear. While you will likely see a reduction in cost, it may be incremental rather than drastic. Furthermore, the savings gained from extending your waiting period might be overshadowed by the increased risk you are assuming. You must calculate the “crossover point”—the moment where the potential revenue lost during the additional time in your waiting period exceeds the money saved in reduced premiums over the course of a year. If you find that the cost of just one or two days of lost revenue is significantly higher than the annual premium savings, then a longer waiting period is mathematically unwise, regardless of the reduced insurance cost.

    When discussing these premiums with your agent, ask for a comparison of multiple waiting period options. Most insurance companies have the flexibility to adjust this parameter and provide you with a tiered list of pricing. By looking at the premiums for 24, 48, and 72-hour waiting periods side-by-side, you can better understand how much you are actually paying for the “speed” of your coverage. This transparency allows you to make an informed decision based on your specific business income waiting period tolerance. Many businesses find that there is a “sweet spot” at 48 hours, where the premiums become significantly more attractive compared to a 24-hour period, yet the duration is still short enough to prevent a liquidity crisis during a moderate disruption.

    Ultimately, the impact on your premium should be viewed as part of your overall risk management budget. Think of it as a tradeoff between fixed costs (your premiums) and potential variable costs (the risk of lost revenue during an outage). If your business is seasonal, or if you operate in a cyclical industry where cash flow is highly variable, you may find that you prefer to pay a slightly higher premium in exchange for the peace of mind that comes with a shorter waiting period. By understanding how the insurance waiting period explained here affects your bottom line, you can negotiate a policy that is both cost-effective and structurally sound for your specific risk profile.

    Common Waiting Period Lengths in Commercial Policies

    When reviewing commercial property and business interruption insurance policies, the waiting period—often referred to in industry parlance as an elimination period—is a critical time element. Unlike a traditional business insurance deductible, which is expressed as a flat dollar amount, the waiting period functions as a temporal deductible. It defines the specific duration that a business must remain non-operational or suffer revenue loss before the insurance coverage triggers its payout obligations.

    While policy language varies significantly between carriers, industry standards have gravitated toward specific time increments. Understanding these common durations is essential for business owners to align their coverage with their unique operational risk profile.

    • The 24-Hour Period: This is generally considered the most aggressive and comprehensive waiting period. It is often found in high-end, premium policies or specialized coverage forms. For businesses with razor-thin margins or those that rely on continuous, uninterrupted production (such as specialized manufacturing or data centers), a 24-hour window minimizes the gap in protection, ensuring that claims processing begins almost immediately after a covered loss occurs.
    • The 48-to-72-Hour Period: This is perhaps the most common standard for small-to-mid-sized commercial policies. It strikes a balance between keeping premiums affordable and providing meaningful relief. Most “off-the-shelf” business owner policies (BOPs) utilize a 72-hour threshold. This duration is designed to filter out minor, short-term interruptions—such as a brief power flicker or a minor pipe leak that is resolved over a weekend—that a business is expected to absorb as part of its normal operational risk.
    • The 7-Day to 14-Day Period: These longer waiting periods are often selected by large enterprises or organizations with robust cash reserves and significant self-insurance capabilities. By opting for a week or two of non-coverage, businesses can significantly reduce their annual premiums. This is often a strategic financial decision, as these firms may conclude that they can handle short-term recovery costs independently, reserving insurance coverage for catastrophic events that cause extended shutdowns.

    It is important to note that the business interruption time element does not always apply uniformly across all sub-coverages. For instance, a policy might feature a 72-hour waiting period for general business income, but might have a different or even zero-day waiting period for extra expense coverage—the costs incurred to mitigate the loss, such as renting temporary office space or expediting shipping. Distinguishing between these sub-limits is vital when analyzing your specific policy declarations.

    Waiting Period Length Primary Benefit Cost Implication Best For
    24 Hours Maximum protection Highest premiums High-tech, JIT manufacturing, high-revenue retailers
    72 Hours Balanced risk Moderate premiums Standard retail, professional services, restaurants
    7 to 14 Days Significant savings Lowest premiums Large corporations, businesses with strong cash reserves

    The Impact of Waiting Periods on Small Business Recovery

    The waiting period acts as a financial shock absorber, but for a small business, it can be the difference between a seamless recovery and an existential threat. Because small businesses typically operate with leaner cash buffers than their larger counterparts, the impact of the business income waiting period is magnified.

    Consider the “Day Zero” effect. When a covered peril—like a fire or windstorm—strikes, the initial 72 hours are often a period of high-intensity activity: assessing damage, communicating with vendors, notifying staff, and coordinating with insurance adjusters. If your policy has a 72-hour waiting period, you are essentially paying for those initial cleanup efforts out-of-pocket, without the benefit of insurance reimbursement. If the business lacks the liquid capital to survive those first three days of zero revenue while still paying for emergency repairs, the recovery effort may stall before it even begins.

    Furthermore, the waiting period can create a “hidden” cost structure. Many owners focus on the direct costs of repair but fail to account for the indirect costs that accrue during the elimination phase. During a three-day waiting period, payroll may still need to be satisfied, rent is still due, and debt service obligations remain unchanged. If the waiting period is set too long, the cumulative cost of these static expenses can erode a company’s working capital to the point of insolvency. Conversely, if a business owner chooses a very short waiting period without understanding the premium load, they may be overspending on insurance for risks they could have easily managed with a small emergency fund.

    The psychological impact also cannot be ignored. The certainty of having coverage kick in after a known period helps leadership teams make more confident decisions regarding post-disaster recovery strategies. Without clarity on the business interruption insurance waiting period, management might hesitate to authorize essential repair or mitigation work, fearful that those costs will fall entirely on the bottom line. Therefore, understanding this threshold is a core component of effective business continuity planning.

    Strategic Ways to Manage Waiting Period Financial Risks

    Managing the financial risk of a waiting period is an exercise in balancing self-insurance with risk transfer. There are several strategic maneuvers that savvy business owners utilize to mitigate the exposure created by the insurance waiting period.

    1. Maintain a Dedicated “Disaster Fund”: The most effective way to hedge against a waiting period is to hold sufficient cash reserves. Financial experts often suggest that businesses keep at least one month of fixed operating expenses in a liquid account. If your policy has a 72-hour waiting period, you should be able to cover that gap plus an additional buffer without jeopardizing your ability to pay your employees or service your core debts. This approach allows you to opt for a longer, cheaper waiting period on your insurance policy, effectively lowering your annual fixed costs while keeping yourself safe from the “middle-ground” of loss.

    2. Segment Your Risks: Not all parts of a business are equally affected by a waiting period. You might choose to self-insure the waiting period for one location while purchasing a low-waiting-period policy for a critical distribution center. By performing a rigorous business interruption time element analysis, you can determine where the financial impact of a 48 or 72-hour delay would be most catastrophic and prioritize insurance coverage for those specific nodes of your operation.

    3. Enhance Your Business Continuity Plan: If you know that your policy has a 72-hour wait, your recovery plan should be designed to get you back to at least partial operation within that window. For example, if you have a contingency contract with a third-party IT vendor or a secondary manufacturing site, you might be able to resume partial output even while your primary facility is undergoing repair. Even if you aren’t at full capacity, you may be able to generate enough revenue to offset the burden of the waiting period.

    4. Evaluate Umbrella or Contingency Coverages: In some cases, specialized riders or contingent business interruption policies can be structured to sit “on top” of your primary policy, providing coverage for costs incurred during the elimination period. While these are less common and may require more intensive underwriting, they are a powerful tool for businesses that simply cannot afford to have any revenue-free days.

    Negotiating Policy Terms with Your Insurance Broker

    Negotiating your business interruption insurance waiting period is not about finding the “cheapest” option, but rather the “best-fit” option. To conduct an effective negotiation, you must enter the conversation with a clear understanding of your business’s financial velocity.

    Start by asking your broker to provide a side-by-side premium comparison. Ask them to model the difference in cost between a 24-hour, 48-hour, and 72-hour waiting period. Often, the premium difference is smaller than business owners expect, and upgrading to a shorter waiting period can provide peace of mind that outweighs the cost. However, be wary of the business insurance deductible as well. Ensure your broker explains how the waiting period interacts with your standard property insurance deductible. Sometimes, a policy can be structured to have a lower waiting period but a higher deductible, or vice versa. Finding the right mix depends on whether your biggest concern is a short, sudden shock or a prolonged recovery.

    It is also crucial to discuss how the waiting period is measured. Does the time start the moment the damage occurs, or the moment the business is rendered unable to operate? Is there a specific protocol for how that time is verified by the carrier? A professional broker will be able to help you draft policy language that clarifies these ambiguities, ensuring that when a claim is filed, there is no dispute over whether the waiting period has been satisfied.

    Finally, review your current waiting period annually. As your business grows, your cash reserves and operational dependencies change. A 72-hour wait might have been safe for your startup, but as you scale, your risk profile likely demands a more nuanced approach. Challenge your broker to justify the existing terms based on your current financial statements and operational scale.

    Frequently Asked Questions

    What is the difference between a business interruption waiting period and a standard deductible?

    While both represent the portion of a loss you are responsible for, they function differently. A standard deductible is usually a fixed dollar amount deducted from the final claim payment. A waiting period is a time-based threshold; it is a duration (e.g., 72 hours) during which no business income coverage is triggered. Essentially, you are responsible for the lost income and extra expenses incurred during that specific window of time.

    Can I have a zero-day waiting period on my business interruption insurance?

    Yes, it is possible to negotiate a zero-day waiting period, though it is rare and usually significantly more expensive. Many carriers prefer to include at least a 12-to-24-hour buffer to eliminate the administrative cost of processing extremely small, inconsequential claims. Whether it is worth the cost depends on your cash flow sensitivity and the nature of your operations.

    How does the waiting period impact my extra expense coverage?

    In many policies, the waiting period applies specifically to the loss of net income. However, some insurance forms apply the same waiting period to “Extra Expense” coverage—the costs of temporary rent, equipment rental, or relocation. It is vital to check your policy declarations, as you might find that you are covered for emergency costs immediately, even if your coverage for lost income doesn’t trigger until 72 hours have passed.

    If I have multiple locations, does the waiting period apply to each one separately?

    Generally, the waiting period applies to each individual occurrence of loss per location. However, this depends entirely on the language of your policy. Some policies may have a blanket waiting period for the entire company, while others may trigger the waiting period for every single location affected by a single, multi-site event. Always consult with your broker to ensure the aggregation of losses is handled in a way that aligns with your business structure.

    Does the waiting period only count the hours the business is “open”?

    This is a common point of confusion. Most insurance policies define the waiting period in terms of consecutive hours from the time of the loss, regardless of your operating hours. If your business operates 9-to-5, a 72-hour waiting period doesn’t necessarily mean three “business days”—it means 72 consecutive hours. This is why it is essential to read the specific policy definitions regarding how time is measured.

    What documentation do I need to prove the waiting period has elapsed?

    You should maintain detailed logs documenting the exact time the physical damage occurred, the time your operations were officially halted, and the time you resumed operations (even if at a partial capacity). Photos, time-stamped security footage, emergency repair invoices, and internal communications regarding the closure are all invaluable during the claims process to establish the timeline against the policy’s waiting period requirement.

    Conclusion

    The business interruption waiting period is one of the most frequently overlooked components of a commercial insurance policy, yet it holds significant weight in the event of a disaster. By moving beyond the generic “standard” options and performing a deliberate analysis of your business’s financial resilience, you can customize a recovery strategy that protects your bottom line without overspending on premiums. Whether you choose a shorter period to protect thin margins or a longer period to keep costs down, the decision should be an informed one based on your specific operational data.

    Take the time to audit your policy, speak with your insurance broker, and ensure your disaster recovery plan is synchronized with your coverage. Your business’s survival depends on being prepared for the unforeseen; don’t let a misunderstood time element be the reason your recovery fails. Contact your broker today to review your business interruption coverage and confirm that your waiting period is optimized for your long-term success.

    By insureiqguru Editorial Team
  • Cyber Insurance Exclusions: 8 Mistakes to Avoid in 2026

    Cyber Insurance Exclusions: 8 Mistakes to Avoid in 2026

    Key Takeaways

    • Cyber insurance exclusions represent the most common reason for denied cyber insurance claims in the modern threat landscape.
    • Understanding policy fine print is essential for identifying cyber policy gaps before a breach occurs.
    • Many businesses mistakenly assume their general liability policy covers cyber-related bodily injury or property damage.
    • Security protocol requirements, such as multifactor authentication, are frequently cited as grounds for coverage denial if not strictly maintained.
    • Active business cyber risk management requires aligning your IT security maturity with the specific language of your insurance contract.

    In the digital age, a cyber insurance policy is often viewed as the ultimate safety net for a business facing a ransomware attack or a data breach. However, for many organizations, the promise of protection turns into a devastating realization during the claims process. As we approach 2026, the sophistication of threat actors continues to evolve, yet insurance providers are simultaneously tightening their underwriting standards. What was once considered comprehensive coverage may now be riddled with cyber insurance exclusions that leave your organization vulnerable. Navigating this complex landscape requires more than just purchasing a policy; it demands a proactive approach to auditing your cybersecurity insurance coverage limitations. The difference between a funded recovery and a catastrophic financial loss often lies in the nuanced wording hidden deep within the policy documentation. By avoiding these common mistakes, your business can bridge the gap between perceived security and actual contractual protection.

    Understanding How Cyber Insurance Exclusions Work

    To the uninitiated, a cyber insurance policy can look like a monolithic guarantee of coverage. In practice, however, these contracts are highly modular and restrictive. Cyber insurance exclusions are specific provisions within an insurance policy that explicitly state scenarios or types of losses that the insurer will not cover. These are not merely suggestions; they are legally binding boundaries that dictate the scope of your financial protection. When a claim is filed, the claims adjuster’s primary role is not necessarily to prove the attack occurred, but to determine whether the circumstances of the breach fall within an excluded category.

    Most cyber policy gaps emerge because policyholders fail to realize that cyber insurance is not a catch-all solution for IT-related losses. Exclusions are typically categorized into two types: absolute exclusions, which apply to entire classes of loss, and conditional exclusions, which trigger only if certain technical or behavioral requirements are not met. For example, an insurer might provide coverage for data recovery but exclude any losses resulting from a failure to update third-party software. This creates a significant blind spot for businesses that outsource their software management but fail to verify the security protocols of their vendors.

    The complexity of cyber policy fine print often stems from the fact that cyber risk is dynamic. As hackers develop new methods—such as deepfake-driven social engineering or AI-powered brute force attacks—insurers update their policy language to manage their own risk exposure. If your policy language hasn’t been reviewed in the last twelve months, it is likely outdated in the face of modern threats. Businesses must shift their mindset from “buying coverage” to “managing contract adherence.” This means understanding that the burden of proof often rests on the policyholder to demonstrate that they maintained the required “minimum security baseline.” When you sign a contract, you are effectively agreeing to a set of operational standards. If you fall below those standards, an exclusion clause may trigger, resulting in denied cyber insurance claims that could bankrupt an unprepared firm. Understanding these exclusions requires a collaborative effort between your IT department, your legal team, and your insurance broker. The goal is to identify these limitations before an incident occurs, ensuring that your insurance strategy matches your actual business cyber risk management posture.

    Policy Strategy Operational Focus Best For
    Standard Adherence Focuses on mandatory MFA and patch management. Small to mid-sized businesses with low-complexity IT.
    Vendor-Neutral Mapping Aligns security protocols with multiple insurance carriers. Organizations with multi-cloud or hybrid infrastructures.
    Aggressive Risk Transfer High coverage limits with rigorous security audit trails. Enterprises with significant regulatory and legal liability.

    The Danger of Improper Security Protocol Exclusions

    One of the most insidious types of cybersecurity insurance coverage limitations relates to the failure to implement mandatory security protocols. In recent years, insurers have begun baking specific, granular technical requirements directly into the policy language. These often appear as “conditions precedent” to coverage. If your business experiences a breach and the forensic investigation reveals that you were not using a required technology—such as multifactor authentication (MFA) or endpoint detection and response (EDR)—the insurer may cite these cyber insurance exclusions to deny the entire claim, regardless of whether that specific failure directly caused the breach.

    This is a critical area of business cyber risk management that many executives overlook. The assumption is often that insurance is there to cover “accidents” or “negligence.” While this is true in many contexts, cyber insurance is different. It is increasingly moving toward a “guaranteed security” model where the insurance company acts as a de facto audit authority. If you state on your application that you utilize air-gapped backups for your critical data, but your IT team decides to move that data to a cloud-based server without notifying the insurer, you have effectively voided a crucial component of your coverage. When the ransom demand arrives and you discover your backups are encrypted, your claim could be rejected because you failed to maintain the specific protocol agreed upon in the application.

    To avoid this, businesses must establish a continuous monitoring loop between their IT security roadmap and their insurance policy. It is insufficient to fill out the application once a year and file it away. Instead, organizations should treat their policy as a living document. Whenever a major change to the technical infrastructure occurs, the risk management team must ask: “Does this change impact our policy compliance?” For instance, shifting to a remote-first work policy significantly changes the risk profile and may render your existing firewall or VPN exclusions inadequate. Many denied cyber insurance claims originate from this simple disconnect between the IT department’s operational agility and the legal department’s rigid insurance constraints. Furthermore, avoid the trap of “soft” security implementations. If the policy requires “multifactor authentication on all remote access points,” ensure that this is verified across all departments—including high-level executives who may resist these measures. An exception made for convenience is an opening for an insurer to exclude coverage if a breach occurs through an un-protected account.

    How Intentional Acts and Employee Misconduct Trigger Denials

    The fine print regarding “intentional acts” and “employee misconduct” is frequently misunderstood by business owners. Most cyber policies are designed to cover accidental data losses, external hacks, or system failures. They are not designed to protect against internal sabotage, fraudulent wire transfers performed by internal staff, or intentional violations of company security policy. However, the definition of “intentional” can be surprisingly broad, creating significant cyber policy gaps for unsuspecting companies.

    For example, if a rogue employee decides to bypass a security protocol to facilitate their work, and that bypass leads to a breach, the insurer may classify this as an intentional act, thereby excluding the claim. Even more dangerous is the exclusion of “social engineering” or “fraudulent instructions.” If your finance department is tricked into wiring money to a fraudulent account, this is often treated differently than a traditional ransomware attack. Many standard policies contain strict cybersecurity insurance coverage limitations for social engineering, requiring that specific authentication procedures were followed before the money was moved. If an employee bypassed an internal protocol—like a phone verification process—to speed up a transaction, the insurance company may argue that the claim is excluded due to the failure to follow standard internal controls.

    This reality necessitates a shift in culture, not just a technical fix. Employee training and strict, enforced internal controls are your first line of defense, not just against hackers, but against insurance denials. You must document that you have provided adequate training and that your internal processes are designed to prevent the very actions that insurers exclude. When a breach happens, the forensic team will look for evidence of policy violations. If they find that an employee ignored a security training module or bypassed a multi-step verification process, you are at risk. Furthermore, be wary of the “deliberate act” exclusion. Some policies exclude coverage if any principal of the company “knew” of a vulnerability but failed to act. If your CISO identifies a known, unpatched vulnerability and the organization decides to delay the fix due to operational downtime, you may be creating an uninsurable risk. In the eyes of some insurers, this “willful failure” to patch could invalidate your protection entirely. Transparency with your broker is vital here; if you have a known security gap that you are actively working to remediate, ensure that this is documented in your policy as a scheduled improvement rather than a permanent vulnerability.

    Navigating Prior Acts and Known Vulnerability Clauses

    Perhaps the most complex aspect of modern cyber insurance is the concept of “prior acts.” When you switch insurance carriers or renew your policy, you must pay close attention to your “retroactive date.” This date marks the beginning of the time period for which your policy provides coverage. If a hacker infiltrated your system prior to this date, but the impact of that breach (such as a ransomware event) happens during your current policy term, your insurer may deny the claim by citing that the initial “act” occurred outside the coverage window. This is one of the most common causes of denied cyber insurance claims during mergers, acquisitions, or simply when switching providers for lower premiums.

    The “known vulnerability” clause is a similar trap. Insurers often expect policyholders to act with reasonable due diligence. If it becomes public knowledge that a specific software you use has a critical zero-day vulnerability, insurers may provide a “grace period” for you to patch it. If you fail to do so within that timeframe, any subsequent breach exploiting that vulnerability may be excluded from coverage. This puts the burden on your IT team to stay abreast of threat intelligence and proactively manage your risk. Cyber policy fine print often lists these timeframes in vague terms like “reasonable time,” which provides the insurer significant leverage to dispute claims.

    Managing these risks requires a sophisticated approach to asset management and vulnerability scanning. You cannot protect what you do not know you have. A comprehensive audit should include a full inventory of all software, hardware, and connected devices within your network. When negotiating your policy, you should aim for the broadest “prior acts” coverage possible, ideally negotiating for “full prior acts” coverage if you have a clean history. Be wary of “known circumstance” exclusions, which state that you are not covered for any incident that you were aware of—or reasonably should have been aware of—before the policy inception. If you have had previous minor breaches, document them thoroughly during the underwriting process. Hiding these occurrences to secure a lower rate is a recipe for a denied claim later. The goal of business cyber risk management should be to eliminate these “knowns” as quickly as possible. Every day that a known vulnerability persists, you are effectively self-insuring against a risk that you believed was covered. Proactive patching and a clear communication channel between your security operations team and your insurance advisor can help you close these gaps before they trigger a catastrophic exclusion clause.

    The Risk of Bodily Injury and Property Damage Exclusions

    As the Internet of Things (IoT) and Industrial Control Systems (ICS) integrate deeper into business operations, the line between cyber risk and physical risk is blurring. Many business owners operate under the dangerous assumption that their standard cybersecurity insurance coverage limitations will protect them in the event that a cyberattack causes physical harm or damage to property. In reality, most cyber policies contain specific exclusions for “bodily injury” and “property damage.” This is a significant point of contention in cyber policy gaps for manufacturing, healthcare, and infrastructure-reliant businesses.

    Consider a scenario where a malicious actor hacks a factory’s temperature control system, causing an overheating event that ruins expensive machinery and causes a fire that results in an employee injury. A standard cyber policy will likely cover the cost of the data breach and the notification of affected customers, but it will almost certainly exclude the damage to the machinery and the liability arising from the bodily injury. In this situation, the business is left to rely on its general liability or property insurance. However, many general liability policies also contain “cyber exclusions,” which specifically state that they do not cover losses “arising out of, or resulting from, the access to, or use of, any computer system.” This creates a “coverage donut hole” where neither policy provides indemnity.

    To address this, organizations must seek “silent cyber” coverage or explicitly negotiated endorsements that bridge these two domains. Do not assume your existing policies cover this gap. Instead, perform a cross-policy analysis. Compare your property and casualty insurance with your cyber policy and look for these exclusion triggers. If you operate physical infrastructure that is network-connected, you need to ensure that your insurance portfolio includes “Cyber-Physical” coverage. This is a specialized area of underwriting, and simply opting for a standard policy is insufficient. Furthermore, check the wording on “contingent business interruption.” If a vendor’s cyberattack shuts down your physical manufacturing line, the resulting lost income might be covered, but the damage to your own hardware may not be. Experts generally agree that the best strategy is to have a single, unified risk management approach that explicitly acknowledges the potential for cyber events to cause real-world, physical damages. By explicitly requesting coverage for “physical loss resulting from cyber-peril,” you force your insurer to address these gaps during the underwriting process. Failing to do so leaves your business exposed to events that could exceed your financial reserves, as physical damages are often significantly more expensive to remediate than digital data breaches.

    Why Infrastructure Failures Often Go Uncovered

    One of the most persistent misconceptions among business owners is the belief that cyber insurance acts as a catch-all safety net for any digital disruption. In reality, a significant portion of downtime is triggered by infrastructure failures that fall squarely outside the scope of traditional cyber policies. When a server crashes or a data center goes offline, many policyholders are shocked to find their claims denied because the cause was categorized as a mechanical or electrical failure rather than a malicious cyberattack.

    Cyber insurance is designed to respond to “cyber perils”—incidents involving unauthorized access, data breaches, or intentional malicious acts. Infrastructure failures caused by hardware aging, software bugs, or general power outages are typically governed by commercial property or business interruption policies, not cyber coverage. This creates a critical “no-man’s-land” where businesses suffer massive financial losses, yet have no insurance vehicle to recoup those costs because they failed to map the specific cause of the outage to the right policy language.

    Furthermore, many policies include exclusions for “acts of God” or systemic failures that affect broad swathes of the internet. If your cloud provider experiences a widespread outage due to a faulty software update—a phenomenon known as a cascading failure—insurers often argue that this does not constitute a “cyber event” under the definitions stipulated in your contract. Without explicit “contingent business interruption” coverage that specifically accounts for third-party infrastructure instability, your business remains highly vulnerable to these common, non-malicious operational risks.

    Intellectual Property and Patent Infringement Gaps

    The intersection of technology and liability is fraught with legal complexity, particularly regarding Intellectual Property (IP). A common pitfall in cyber policy management is the assumption that a cyber policy covers the legal costs or damages resulting from claims that your software, algorithms, or digital content infringed on another company’s patents or trademarks. In the vast majority of cases, cyber policies expressly exclude intellectual property disputes.

    Cyber insurance is primarily focused on the privacy and security of data. When an insurer writes a policy, they are underwriting the risk of a breach, not the risk of bad-faith business practices or design infringement. If your firm is sued for allegedly stealing source code, violating a copyright in your digital marketing, or infringing on a patented cybersecurity protocol, your cyber insurance carrier will likely issue a letter of denial citing an IP exclusion clause. These exclusions are often buried in the fine print under “Exclusions and Limitations of Liability.”

    Businesses that fail to bridge this gap often end up paying exorbitant legal fees out-of-pocket. To protect against this, companies must look toward “Media Liability” endorsements or specialized Tech Errors & Omissions (E&O) policies. These separate, yet complementary, insurance products are designed to handle the fallout of creative and proprietary disputes. Relying solely on a standard cyber policy for such risks is a fundamental error in business cyber risk management that can lead to catastrophic fiscal exposure.

    The Reality of Regulatory Fine and Penalty Limitations

    While many businesses purchase cyber insurance specifically to cover the costs of a GDPR, CCPA, or HIPAA violation, the fine print often reveals a much more restrictive reality. Many jurisdictions and insurance contracts prohibit the coverage of “punitive” fines and penalties. While an insurer may cover the costs of a forensic investigation, notification, or legal defense, the actual regulatory fines—which are often the most damaging part of a data breach—may be uninsurable depending on the specific language of the policy and the laws of the jurisdiction.

    Insurers often include “insurability of fines” clauses, which state that if the law of the governing jurisdiction does not permit the insuring of civil or criminal penalties, the carrier will not pay those amounts. This effectively renders your coverage useless if you are targeted by regulators who levy heavy penalties. Furthermore, if a breach is deemed to have occurred due to “gross negligence” or “willful non-compliance” with security standards, the insurance company has a strong baseline to deny the claim entirely, arguing that the business effectively invited the risk through reckless operational habits.

    To navigate this, businesses must be hyper-aware of the distinction between “insurable” and “uninsurable” costs. Companies should prioritize compliance frameworks that satisfy the policy’s minimum security requirements. Many policies stipulate that if you fail to maintain “reasonable security measures,” the coverage for regulatory defense may be reduced or voided. This makes the documentation of security controls not just a technical necessity, but a vital component of your insurance eligibility.

    Policy Type Primary Focus Best For
    Standard Cyber Liability First-party breach costs and third-party liability General business protection against hackers.
    Tech E&O Insurance Performance failure and professional negligence Software developers and managed service providers.
    Media Liability IP infringement, libel, and copyright issues Digital agencies and content creators.
    Directors & Officers (D&O) Fiduciary failure in oversight of security Protecting executives from shareholder lawsuits.

    How to Negotiate Better Cyber Insurance Terms

    Negotiating cyber insurance is not a standard transactional purchase; it is a tactical exercise in risk transfer. The most successful businesses approach the negotiation process by treating their security posture as a competitive advantage that can lower premiums and improve coverage terms. Instead of simply accepting the standard policy offer, savvy business leaders work with brokers to strike specific exclusions from the contract.

    The first step in negotiation is “Endorsement Management.” Many of the most dangerous exclusions—such as those related to social engineering, wire transfer fraud, or cloud provider downtime—can be bought back into the policy through endorsements. By explicitly requesting these, you ensure that the gaps are closed before a claim ever happens. You should also press for “Duty to Defend” language, which forces the insurer to take the lead in legal proceedings, rather than leaving your team to navigate the complexities of data breach litigation alone.

    Additionally, pay close attention to the “Consent to Settle” clause. Without a favorable clause here, an insurer might force a settlement that is damaging to your business reputation, or conversely, refuse to settle when you believe it is the most prudent path forward. By negotiating for more influence over the settlement process, you ensure that the insurer’s response aligns with your long-term business goals and public relations strategy. Always remember that insurance contracts are written in favor of the carrier; your job is to negotiate for the “clarity of intent” that protects your specific business model.

    Conducting a Regular Policy Gap Analysis

    A policy purchased in 2026 may be entirely inadequate by the time renewal rolls around. Cyber risk management is not a “set it and forget it” task. As your business grows, adopts new technologies, and shifts its storage to different cloud environments, your insurance coverage must evolve in lockstep. A regular policy gap analysis is the only way to ensure that your coverage doesn’t drift away from your actual operational risk profile.

    To conduct an effective gap analysis, start by gathering your current security stack documentation and comparing it against your policy’s “security requirements” section. If you have adopted new AI tools, moved to a remote-first work environment, or started collecting a new type of sensitive consumer data, you must determine if your existing policy definitions of “network” or “data” still cover these new vectors. If the policy definition is too narrow, you have a gap.

    Furthermore, involve your IT and legal departments in the annual review. They see the threats in the trenches; their input is invaluable for identifying where the insurance coverage ends and reality begins. Document every discussion with your broker or carrier regarding these gaps. If a claim is denied in the future, having a record of your proactive efforts to identify and address potential holes in your coverage can demonstrate a “good faith” effort that may influence dispute resolution outcomes.

    Frequently Asked Questions

    Why is my cyber insurance policy denying my claim for a phishing attack?

    Many policies treat social engineering—like phishing—differently than a technical system hack. If your policy does not have a specific “Social Engineering” or “Funds Transfer Fraud” endorsement, the insurer may argue that the loss resulted from a voluntary action by an employee rather than a unauthorized breach of the network.

    Does cyber insurance cover the cost of a ransom payment?

    Some policies provide coverage for ransomware payments, while others explicitly exclude them or require pre-approval from the carrier before any funds are released. Additionally, you must be aware of local laws, as some jurisdictions have introduced strict regulations that complicate or prohibit paying ransoms to sanctioned entities.

    What is the difference between first-party and third-party coverage in cyber insurance?

    First-party coverage pays for your own expenses, such as the costs to recover data, investigate the breach, and notify customers. Third-party coverage is designed to pay for legal defense and settlements if a customer or partner sues your business due to the damage caused by the breach of their data.

    Can I be denied coverage if I don’t use Multi-Factor Authentication (MFA)?

    Yes. Many modern cyber insurance carriers now make MFA a mandatory condition for coverage. If your policy stipulates that MFA must be enabled on all remote access points and you fail to comply, an insurer may deny a claim or cancel the policy entirely for misrepresentation of your security posture.

    Will my cyber policy cover physical damage to hardware?

    Generally, no. Cyber insurance is focused on digital assets and electronic data. If a cyberattack causes a fire or physical hardware destruction, you would typically look to your commercial property policy to cover the physical damage, while the cyber policy covers the data restoration and business interruption components.

    How often should I review my cybersecurity insurance policy?

    You should review your policy at least annually or whenever there is a major change in your business operations, such as a merger, acquisition, migration to a new cloud provider, or a significant expansion of your data collection practices. This ensures the fine print of the policy still matches your current risk profile.

    Conclusion

    Cybersecurity insurance is a cornerstone of modern business continuity, yet it is far from a simple safeguard. As we move further into 2026, the complexity of digital threats—and the corresponding complexity of insurance contracts—demands a sophisticated, proactive approach to risk management. The most successful businesses do not treat their insurance as a background utility; they treat it as a strategic asset that must be rigorously maintained, negotiated, and audited.

    By understanding the nuances of policy gaps, scrutinizing the fine print for exclusions, and aligning your security controls with your coverage obligations, you can build a resilient infrastructure that survives even the most sophisticated digital assaults. Do not leave your business’s future to chance by assuming you are protected where you are not. Take the time today to perform a gap analysis and reach out to your broker to tighten your coverage terms. If you haven’t reviewed your policy in the last six months, your coverage is already aging. Contact your advisor today to ensure your protection is as dynamic as the risks you face.

    By insureiqguru Editorial Team
  • Professional Indemnity Insurance: Is It Worth It for Consultants?

    Professional Indemnity Insurance: Is It Worth It for Consultants?

    Key Takeaways

    • Professional indemnity insurance is designed to cover legal defense costs and damages resulting from claims of professional negligence or failure to provide services as promised.
    • Consultants face unique risks because their work is often intangible, making it difficult to define “success” and leaving them vulnerable to dissatisfaction-based lawsuits.
    • Professional indemnity is distinct from general liability; while the latter covers physical accidents, the former focuses strictly on professional output and advice.
    • Real-world claims often stem from project delays, mismanaged expectations, or data security breaches, even when the consultant has performed their work in good faith.
    • Consultant risk management strategies should always include a combination of clear contractual language and adequate professional liability protection.

    In the modern gig economy, where expertise is the primary commodity, your reputation is your most valuable asset. Whether you are an independent IT advisor, a management strategist, or a niche marketing consultant, your professional worth is defined by the quality and accuracy of the advice you provide. However, even the most meticulous experts can find themselves facing a catastrophic legal challenge if a client perceives that a project has failed or that the advice provided resulted in financial loss. This is where professional indemnity insurance serves as a critical safety net, shifting the burden of legal defense and potential settlements away from your personal and business assets. Understanding the nuance of this coverage is not merely a box to check during business setup; it is a fundamental pillar of modern consultant risk management.

    What Is Professional Indemnity Insurance and How Does It Work?

    Professional indemnity insurance, frequently referred to as errors and omissions insurance for consultants, is a specialized form of business insurance for consultants designed to protect against claims of professional negligence. Unlike general business policies that cover physical injuries or property damage, this insurance addresses the financial consequences of mistakes in professional services. When a client alleges that you provided inadequate advice, failed to deliver a project on time, or committed an oversight that resulted in a financial loss for their business, your professional indemnity policy acts as the primary mechanism for financial recovery.

    The mechanics of how this insurance operates are essential for any business owner to understand. Typically, these policies operate on a “claims-made” basis. This means that the policy must be active both when the alleged incident occurred and when the claim is officially filed against you. Because of this, it is crucial for consultants to maintain continuous coverage even if they pivot to new projects or take a hiatus. If a claim arises from work performed three years ago, a current active policy with the appropriate retroactive date will trigger coverage to handle the defense.

    When a lawsuit or formal demand is received, the insurer typically appoints legal counsel to represent you. This is one of the most vital components of the policy; legal defense costs can accrue rapidly—often reaching tens of thousands of dollars—long before a judge or jury ever considers the merits of the case. By carrying professional liability protection, you shift these immense legal fees onto the insurance carrier. This ensures that you can mount a vigorous defense without the threat of bankruptcy looming over your business operations.

    Furthermore, professional indemnity insurance is not solely for when you have made a verifiable mistake. In many cases, it provides a defense against meritless or frivolous claims. Even if the court eventually finds in your favor, the process of proving your innocence is incredibly costly and time-consuming. An insurance policy protects your cash flow during these periods, allowing you to focus on your clients rather than navigating the complexities of litigation alone. In essence, it functions as both a shield against legitimate professional oversights and a fortress against the unpredictable nature of the litigious business environment.

    Why Consultants Are at Higher Risk for Professional Liability Claims

    Consultants operate in a unique professional sphere where the end product is often intellectual capital rather than a physical good. This creates a challenging environment for risk management. Because the results of a consultant’s work—be it a strategic plan, a software implementation, or a marketing audit—are often intangible, they are inherently subjective. What a consultant considers a successful strategic pivot, a client might view as a failed campaign if the expected revenue growth does not manifest immediately. This disconnect between expectation and reality is the breeding ground for consultant liability insurance claims.

    One of the primary drivers of this elevated risk is the nature of the consultant-client relationship. Consultants are hired precisely because they possess specialized knowledge that the client lacks. Consequently, clients often place a high degree of trust in the consultant’s recommendations. When things go wrong, the client is naturally inclined to hold the expert accountable. If a software consultant suggests a specific database architecture that eventually proves insecure, or if a management consultant advises a supply chain strategy that gets derailed by global logistics shifts, the client may claim that the expert should have foreseen these complications.

    Moreover, the modern regulatory landscape has made clients more sensitive to losses. As businesses face tighter margins and increased competition, they are more likely to look for someone to blame when their objectives are not met. If a consultant’s work is remotely connected to a financial dip in the client’s company, that consultant becomes an easy target for litigation. The lack of a tangible “warranty” on intellectual work means that the burden of proof often lands on the consultant to demonstrate that they adhered to the standard of care expected within their industry.

    Consultant risk management is further complicated by “scope creep.” It is common for projects to evolve as client needs change, often without updated contracts or written acknowledgments. When a project goes off the rails, a client may retrospectively claim that the consultant was responsible for tasks that were never formally agreed upon. Without clear documentation, it is the consultant’s word against the client’s, creating a scenario where errors and omissions insurance for consultants becomes the only thing keeping the business from collapsing under the weight of a legal battle. Because consultants often work with diverse clients across multiple industries, they are exposed to a broader array of legal standards, making professional liability protection indispensable.

    Insurance Type Primary Focus Best For
    Professional Indemnity Negligence, errors in advice, failure to deliver services Advisors, architects, IT consultants
    General Liability Bodily injury, property damage, advertising injury All consultants with physical workspaces
    Cyber Liability Data breaches, network security failures IT and data-heavy consultants
    Errors & Omissions Service-based mistakes and financial losses Service providers handling client funds

    Key Coverage Areas: What Does Your Policy Actually Protect?

    When you invest in professional indemnity insurance, it is critical to look beyond the generic marketing language and understand the granular components of your coverage. A robust policy is not a blanket guarantee for every possible misfortune, but it is a targeted instrument designed to address the specific financial risks inherent in your professional practice. Experts generally agree that a well-structured policy should cover several fundamental areas, starting with legal defense costs, which include attorney fees, court costs, and the expenses associated with expert witnesses or investigators. In complex litigation involving technical errors, these costs alone can be staggering.

    Beyond legal defense, your policy should cover settlements and judgments. If a court determines that you are liable for a financial loss suffered by a client due to a professional error, your insurance carrier will pay the damages up to your policy’s limit. This covers the actual monetary losses the client claims to have incurred because of your service. This is particularly relevant for IT consultants, where a bug in code can lead to significant downtime or data loss for a major corporation. The financial impact of such an event can easily reach into the six-figure range, making the existence of a high-limit policy a matter of corporate survival.

    Another important, yet often overlooked, coverage area is the cost of investigations. In some cases, a potential claim might arise that can be resolved before it ever goes to court. Many insurance policies include provisions that cover the costs of hiring forensic experts or mediators to settle disputes early. By resolving these issues through professional mediation, you not only save on legal fees but also protect your reputation by keeping the matter out of the public record. This proactive approach is a hallmark of good consultant risk management.

    It is also essential to ensure your policy covers “good faith” errors. Mistakes happen—an email sent to the wrong person, a calculation error in a financial model, or an accidental violation of a deadline. Even if you have acted with the best intentions and professional due diligence, you can still be found liable. A comprehensive policy provides professional liability protection for these human errors, ensuring that an honest mistake does not result in the permanent dissolution of your business. Finally, ensure that your policy includes “retroactive coverage.” This is critical because it extends your protection to work you completed in the past, provided the claim is filed after the policy is purchased. This is the difference between a policy that merely covers current projects and one that covers your entire career history as a professional consultant.

    Professional Indemnity vs General Liability: Understanding the Differences

    A common mistake among new consultants is assuming that their general liability insurance covers all business-related risks. While both general liability and professional indemnity insurance are cornerstones of business insurance for consultants, they serve fundamentally different purposes. To put it simply, general liability is about “accidents,” while professional indemnity is about “expertise.” If you confuse the two, you may find yourself with a significant coverage gap at the worst possible moment. Understanding this distinction is the first step toward effective risk management.

    General liability insurance is designed to protect your business against third-party claims of physical injury or property damage. Imagine you are meeting a client at their office, and you accidentally trip over a server cable, causing a piece of their expensive hardware to fall and shatter. This is a classic general liability claim. Similarly, if you invite a client to your studio and they slip on a wet floor, the resulting medical bills would typically be covered under your general liability policy. These claims are straightforward because they relate to physical events that occur within the course of doing business.

    Professional indemnity insurance, by contrast, is entirely removed from physical interaction. It is concerned with the financial consequences of your professional output. If you provide a strategic roadmap for a client’s business growth, and that roadmap is based on flawed assumptions that ultimately cause the client to lose money, this is not a general liability issue. It is a professional liability issue. The damage here is purely financial—the client did not get physically hurt, and no property was broken, but their balance sheet was negatively impacted by your advice. Because general liability policies explicitly exclude coverage for professional services, you would be entirely on your own without professional indemnity protection.

    Some consultants think that if they work remotely, they don’t need general liability insurance. While that may be true in some jurisdictions, most experts advise keeping both. You may hold a physical event, meet at a client’s office, or interact with third parties in person at some point. However, the most important takeaway is that professional indemnity fills the massive hole left by general liability. The claims brought against consultants for “professional negligence” are significantly more expensive than the average physical injury claim, as they often involve lost revenue, breach of contract allegations, and complex financial damages. For any consultant whose work has the potential to impact a client’s bottom line, relying solely on general liability is a dangerous oversight.

    Real-World Scenarios: When Do Consultants Face Lawsuits?

    The triggers for lawsuits in the consulting world are rarely as dramatic as the legal dramas on television. More often, they are rooted in mundane project management failures or communication breakdowns that escalate over time. Take, for example, the IT consultant who is hired to manage a cloud migration for a mid-sized company. Midway through the project, the consultant discovers that the client’s existing architecture is more outdated than initially communicated. The consultant proceeds with a workaround, but a year later, a security breach occurs. The client blames the consultant, arguing that the workaround was technically deficient and that the consultant had a professional duty to mandate a full infrastructure upgrade before proceeding. In this case, errors and omissions insurance for consultants would cover the legal battle to defend the consultant’s decision-making process at the time the work was performed.

    Another frequent scenario involves management consultants hired to optimize operational workflows. A consultant might recommend a specific inventory management software. The client implements it, but due to a lack of staff training—which the consultant argues was the client’s responsibility—the system fails, leading to lost sales during the peak holiday season. The client sues the consultant, claiming that the consultant’s implementation plan was incomplete and that they failed to provide adequate training. Even if the consultant’s contract clearly stated that staff training was the client’s duty, the consultant must still pay for a defense to prove that they honored their side of the agreement.

    Communication-based claims are perhaps the most common. A marketing consultant might be tasked with a brand pivot. The consultant provides a range of options, and the client chooses one. When the campaign launches, it fails to connect with the target audience, and the client loses significant revenue. The client then claims that the consultant promised a specific return on investment (ROI) that never materialized. This is why risk management experts emphasize the importance of avoiding guarantees in contracts. Even if you never verbally promised a specific ROI, the client’s perception of that promise is often enough to trigger a lawsuit. Your professional indemnity policy provides the resources to handle these “he-said-she-said” conflicts, ensuring that your defense is as strong as your initial strategic proposal.

    Finally, there is the issue of project delay. A strategic consultant might be hired to help a company prepare for a merger. The consultant is responsible for creating the due diligence reports. If these reports are delayed by even a few weeks, the entire merger might be jeopardized, costing the client millions. The client may argue that the consultant’s failure to deliver on time was a breach of contract that led directly to the collapse of the deal. In scenarios like this, professional liability protection is the only thing standing between the consultant’s business and a massive financial judgment. These scenarios illustrate why professional indemnity is not just an optional business expense; it is a vital component of the consultant’s operational architecture.

    Factors That Influence Your Insurance Premiums in 2026

    As we navigate the professional landscape of 2026, the cost of securing professional indemnity insurance is no longer determined by simple boilerplate calculations. Underwriters have become increasingly sophisticated, utilizing data-driven models that assess risk on a granular level. Understanding these variables allows consultants to be proactive in managing their risk profile, which can lead to more favorable premium negotiations.

    The primary factor remains the nature of the services rendered. A management consultant advising on organizational culture generally faces a different risk profile than an IT consultant providing architectural oversight for high-stakes cybersecurity infrastructure. Insurers categorize these risks based on the potential for catastrophic financial loss should a project fail. If your consultancy operates in sectors like legal advisory, financial planning, or critical infrastructure engineering, premiums are often elevated due to the high-dollar nature of potential negligence claims.

    Your firm’s historical claims experience—often referred to as your “loss run”—is perhaps the most significant individual factor. Insurance carriers look for a clean history. If you have faced repeated claims, regardless of whether you were ultimately found liable, your premium is likely to increase as you are perceived to be a higher-risk client. Conversely, maintaining a robust, documented track record of successful project delivery and proactive dispute resolution can help keep premiums stable.

    Revenue size and client profile also play a major role. Generally, the higher your annual billings, the higher your premium, as this correlates with a larger volume of work and a statistically higher probability of a dispute arising. Furthermore, the size of your clients matters. Working with multinational corporations or government agencies often triggers higher coverage requirements via contract mandates, and insurers account for the increased complexity of defending against claims brought by large, well-resourced entities.

    Geographic footprint is another vital consideration. In 2026, the legal environment in your specific jurisdiction is a major variable. Regions with high litigation rates or expansive interpretations of “professional duty” will naturally command higher premiums. Additionally, if your consultancy provides services internationally, you are exposing your policy to multiple regulatory regimes, which increases the complexity of legal defense and, consequently, the insurance cost.

    Finally, the sophistication of your own internal risk management protocols is increasingly being used as a pricing lever. Consultants who employ rigorous quality assurance procedures, maintain impeccable documentation, and use standardized, legally vetted engagement letters are often viewed as “preferred risks.” Some carriers in the 2026 market may even offer premium discounts to firms that demonstrate a commitment to ongoing professional development and specialized liability training for their team members.

    How to Determine the Right Level of Coverage for Your Consultancy

    Determining your “limit of liability”—the maximum amount an insurer will pay in the event of a covered claim—is a balancing act. Choosing a limit that is too low leaves your personal or corporate assets exposed, while choosing one that is unnecessarily high results in “wasted” capital spent on redundant premiums. Finding the “goldilocks” zone requires a strategic assessment of your business operations.

    Start by evaluating the worst-case scenario. If a mistake in your advice were to cause a client to lose their entire investment or face a massive regulatory fine, what is the maximum potential damage? While you cannot account for every outcome, you should aim to cover the likely financial consequences of a professional error. For many consultants, this involves reviewing the contracts you sign with your largest clients. Often, these contracts include an “indemnity clause” that dictates the minimum insurance coverage you must carry to be eligible for the contract. Meeting these contractual obligations is usually the baseline for your policy limit.

    Next, consider your client concentration. If you derive eighty percent of your revenue from a single client, you are disproportionately exposed to their financial health and their tendency to litigate. In such cases, your coverage level should be higher to mitigate that specific concentration risk. If your client base is diverse, the probability of a “contagion effect”—where one bad project brings down your entire firm—is naturally lower, potentially allowing for a more conservative coverage limit.

    Consultants should also factor in defense costs. In many policies, the limit of liability is “inclusive” of defense costs, meaning that the money spent on lawyers, expert witnesses, and court fees is subtracted from your total coverage limit. If you have a limit of $1 million and a defense costs $300,000, you only have $700,000 left for the actual settlement or judgment. Ensure your policy language clarifies whether defense costs are *inside* or *outside* the limit; having costs paid “outside” the limit (often called “defense in addition to limits”) is a significantly safer position for the policyholder.

    Policy Type Best For Key Advantage
    Claims-Made Policy Consultants in high-risk, long-cycle projects Usually more affordable, allows for retroactive coverage.
    Occurrence-Based Policy Consultants with stable, predictable risk profiles Coverage stays in place even if the policy expires.
    “Defense in Addition” Policy Firms entering high-stakes litigation areas Protects your total limit from being eroded by legal fees.

    Common Misconceptions About Professional Indemnity Insurance

    Despite the prevalence of professional liability protection in the modern marketplace, several myths persist that can leave consultants dangerously underinsured. Clearing these up is essential for accurate business risk management.

    The most dangerous misconception is that “a standard business insurance package covers everything.” Many consultants assume their General Liability (GL) policy will protect them if a client sues for bad advice. This is false. General Liability covers physical injury or property damage (e.g., someone tripping in your office). It does not cover economic loss resulting from a failure to perform professional services. If your client claims your consulting work led to their bankruptcy, your GL policy will offer zero protection. You must have a dedicated policy for consultant liability insurance to cover purely financial claims.

    Another common myth is that you only need professional indemnity insurance if you are a “big” company. In reality, independent contractors and solopreneurs are often more vulnerable. A single multi-thousand-dollar claim, if not covered by insurance, could lead to personal bankruptcy or the total dissolution of a small business. Smaller firms are often targeted precisely because they may lack the extensive internal legal counsel that larger firms use to deter litigation.

    There is also a prevalent belief that if you have “done nothing wrong,” you don’t need insurance. This ignores the reality of the legal system. In the world of commercial litigation, the cost of *proving* you did nothing wrong can be astronomical. A frivolous lawsuit can drain your resources through legal fees and lost productivity, even if you eventually win the case. Professional indemnity insurance is as much about defense as it is about paying settlements.

    Finally, many consultants believe that once they complete a project, they can cancel their insurance. Because most professional liability insurance is written on a “claims-made” basis, you are only covered for claims filed *while* the policy is active. If a client discovers an error you made two years ago and sues you tomorrow, you will not be covered unless you maintain “tail coverage” or an active policy that includes prior acts coverage. Understanding these nuances prevents the catastrophic mistake of assuming past work remains protected after a policy is terminated.

    Steps to Take When Selecting the Best Policy for Your Business

    Choosing the right coverage is a procedural task that should be approached with the same rigor as your client project planning. Follow these steps to ensure you select a robust policy that truly protects your interests.

    Step 1: Conduct a thorough risk audit. Identify the specific hazards inherent in your service delivery. Do you handle sensitive data? Are your recommendations based on predictive financial models? Do you sign contracts that include strict indemnity obligations? Document these risks so you can articulate your specific needs to a broker or insurer.

    Step 2: Engage a specialist broker. Do not settle for a generic agent. Find a broker who specifically deals with professional indemnity insurance for consultants. They will have a deep understanding of the market, the reputation of different carriers, and the ability to negotiate nuances in the policy wording, such as the definition of “professional services” or the inclusion of “wrongful acts.”

    Step 3: Analyze the “Prior Acts” date. When switching carriers, ensure your new policy covers you for work performed in the past. This is known as your “retroactive date.” If your new policy does not honor your previous start date, you essentially create a coverage gap for your previous work.

    Step 4: Scrutinize the exclusions. Every policy has exclusions—situations where the insurer will not pay. Common exclusions include fraudulent activities, criminal acts, or contractual liability that goes beyond what the law would normally require. Read these carefully. If a common exclusion for your industry is included in the policy, negotiate its removal or find a carrier that provides more tailored coverage.

    Step 5: Review the financial strength of the insurer. Insurance is a promise to pay. You want to ensure the entity making that promise is financially stable. Use independent rating agencies to check the financial health of the carrier. You are looking for a carrier with a long-standing reputation for fairness in claim settlements, not just the one offering the lowest price.

    Frequently Asked Questions

    Is professional indemnity insurance legally mandatory for consultants?

    While laws vary by region and industry, it is rarely mandatory by government law for general consulting firms. However, it is frequently mandated by client contracts, professional licensing bodies, or industry-specific regulations to protect stakeholders. Even when not legally required, it is considered a standard best practice for risk management.

    What is the difference between errors and omissions insurance and professional indemnity?

    In most professional contexts, they are the same thing. “Professional Indemnity” is the term commonly used in the UK, Europe, and Australia, whereas “Errors and Omissions” (E&O) is the standard terminology used in the United States and Canada. Both refer to the same type of coverage designed to protect against claims of professional negligence or failure to provide services as promised.

    How does “prior acts” coverage work?

    Prior acts coverage protects you against claims arising from services you provided before your current policy start date. When purchasing a new policy, the retroactive date determines how far back in time your coverage extends. It is crucial to maintain a consistent retroactive date when switching insurance providers to ensure there are no gaps in your protection for past projects.

    Can I cancel my insurance if I have no active clients?

    It is generally not advisable to cancel your policy completely. Professional liability claims can be filed years after a project is completed. If you plan to shutter your business, you should consider purchasing “tail coverage” (or an Extended Reporting Period), which allows you to continue reporting claims related to your past work for a specific period after you have stopped actively trading.

    What happens if a client sues for an amount higher than my policy limit?

    If a settlement or court judgment exceeds your policy limit, you are personally responsible for the difference (the “excess”). This is why it is vital to regularly evaluate your coverage limits to ensure they align with your firm’s current client size and the potential financial impact of a failed project, rather than just picking a minimum limit to save on premiums.

    Do I need this insurance if I have an LLC or Corporation?

    Yes. While an LLC or corporate structure provides a layer of legal separation between you and your business assets, it does not provide immunity against professional negligence claims. A client can still sue the business entity, which could result in the total depletion of the company’s assets. Professional indemnity insurance is the only way to shift the financial burden of these legal challenges to an insurer.

    Conclusion

    The journey of a consultant is defined by the value they provide to clients, but this value is inextricably linked to the risks inherent in providing professional advice. As we have explored, professional indemnity insurance is not merely a bureaucratic checkbox or an optional expense; it is a fundamental pillar of professional maturity. By proactively managing your risk, understanding the nuances of your coverage, and selecting the right protection for your specific niche, you transform your insurance from a defensive necessity into a strategic advantage.

    In an increasingly litigious global environment, demonstrating that you are properly insured also serves as a hallmark of credibility. Clients trust consultants who take responsibility for their work, and holding comprehensive liability coverage is a clear sign that you are a serious, established professional. Don’t leave your career and your reputation to chance. Take the time to audit your risk profile today and secure a policy that gives you the peace of mind to focus on what you do best: driving results for your clients.

    Are you ready to secure your consultancy? Contact a licensed insurance advisor specializing in professional liability to conduct a gap analysis of your current operations and receive a tailored quote today.

    By insureiqguru Editorial Team

  • Social Engineering Fraud Insurance: Is It Worth It in 2026?

    Social Engineering Fraud Insurance: Is It Worth It in 2026?

    Key Takeaways

    • Social engineering fraud insurance protects against losses caused by human error, such as manipulated wire transfers, rather than just technical system breaches.
    • Standard cyber policies often exclude social engineering, making standalone cyber insurance add-ons essential for modern risk management.
    • Business email compromise (BEC) remains a leading threat, frequently targeting accounts payable departments with urgent, fraudulent requests.
    • Effective phishing protection for business requires a combination of robust insurance coverage, employee training, and multi-factor authentication.
    • When selecting a policy, businesses must scrutinize definitions of “social engineering” and “computer fraud” to ensure their coverage aligns with specific operational risks.

    As we navigate the mid-decade business landscape of 2026, the perimeter of the corporate network has effectively dissolved. With decentralized workforces and an increasing reliance on digital communication, the most vulnerable component of any organization is no longer a server or a software vulnerability—it is the human employee. Social engineering has emerged as the weapon of choice for sophisticated criminal syndicates, targeting the psychological tendencies of workers to bypass even the most expensive digital defenses. For many organizations, the question is no longer whether they will be targeted by a fraudulent scheme, but whether their existing insurance portfolio is sophisticated enough to recover the losses when a trusted employee inadvertently authorizes a multi-million-dollar wire transfer to a threat actor. This guide, brought to you by the insureiqguru Editorial Team, explores the necessity of social engineering fraud insurance in an era where trust is often a liability.

    What Is Social Engineering Fraud?

    At its core, social engineering fraud is the art of psychological manipulation. Unlike a technical cyberattack that seeks to exploit a weakness in hardware or software, social engineering targets the inherent human willingness to be helpful, to follow authority, or to resolve a perceived crisis. In a business context, this manifests as a deceptive communication designed to trick an employee into performing an act—such as wiring money, changing banking details for a known vendor, or disclosing sensitive credentials—that results in a significant financial loss.

    The complexity of these attacks has escalated significantly by 2026. While the “classic” phishing email—riddled with grammatical errors and promising unrealistic rewards—still exists, modern social engineering is far more surgical. Attackers often spend weeks or even months conducting reconnaissance on their target organizations. They monitor executive travel schedules via social media, scrape public business filings, and analyze tone and linguistic patterns from legitimate company communications. By the time a fraudster sends that initial email, they possess enough internal context to bypass initial skepticism.

    Social engineering fraud is distinct from standard “hacking” because it relies on the voluntary action of the victim. If an employee is coerced or tricked into initiating a wire transfer, that is a social engineering event. If a hacker breaks into a server to steal data without an employee’s participation, that is typically categorized as a standard cyber intrusion. Understanding this distinction is the cornerstone of risk management. Because the employee effectively “authorized” the transaction, many traditional banks and insurance policies initially viewed these losses as outside the scope of coverage. This is precisely why specialized social engineering fraud insurance has moved from being a niche luxury to a business-critical requirement.

    These schemes are rarely one-off events. They often follow a trajectory of “Business Email Compromise” (BEC), where the attacker gains unauthorized access to an email account and monitors ongoing conversations. They wait for the perfect moment—a large pending invoice or a high-stakes merger—to interject. By sending an email from a legitimate account, or a domain that is nearly indistinguishable from the real one, the attacker creates a sense of extreme urgency. Because the request originates from a “known” source, the employee feels pressured to bypass standard verification protocols. This creates a psychological trap that is remarkably effective regardless of how much technical training the employee may have received.

    Why Traditional Cyber Policies Often Fall Short

    Many business owners labor under the misconception that their general liability or standard cyber insurance policy provides an all-encompassing safety net. Unfortunately, this is a dangerous assumption. Traditional cyber policies were designed primarily to cover the aftermath of a “data breach”—the expenses associated with forensic investigations, legal fees for privacy violations, customer notification requirements, and potential regulatory fines. In these scenarios, the threat actor enters the system to steal data; they are a trespasser.

    However, social engineering is fundamentally different. In a social engineering scenario, the business is not necessarily “breached” in the traditional sense. The employee was not hacked; they were fooled. Because the employee took the action to move funds or release information, insurance carriers often categorize this as a “voluntary parting” of assets. Standard policy language often contains restrictive “social engineering fraud” exclusions. If a policy is not specifically drafted to provide coverage for this, the insurance company may argue that the loss was not a “computer-based” loss, but rather a simple case of corporate mismanagement or employee error.

    Furthermore, standard cyber policies frequently lack the specific sub-limits required to cover the high-value losses associated with wire fraud. A policy might provide two million dollars in coverage for a data breach but only five thousand dollars for social engineering events, or none at all. Without explicit wire fraud insurance add-ons, the business is left to absorb the loss, which can be catastrophic for small to mid-sized enterprises (SMEs). The insurance market has seen a surge in claims involving spoofed emails from CEOs requesting urgent, confidential wire transfers. If the policy definition of a “claimable loss” requires a physical breach of a server, the claim will likely be denied.

    Another area where traditional policies fall short is in the definition of “computer fraud.” Some older policies might only cover losses if there was “unauthorized access” to the internal system. Since social engineering often involves using compromised credentials (which technically act as “authorized” access), the policyholder may find themselves in a coverage gap. This is why it is essential to review the “insuring agreements” of any policy. Modern policies should explicitly include coverage for “Social Engineering Fraud” or “Funds Transfer Fraud” as a standalone component. Relying on an outdated policy is not merely a risk; it is a point of significant financial exposure that can threaten the continuity of business operations in the current threat environment.

    Coverage Option Primary Focus Best For
    Standard Cyber Policy Data breach response, legal/regulatory costs. Companies focused on liability for leaked customer data.
    Standalone Social Engineering Insurance Reimbursement for funds stolen via deception. Businesses that regularly conduct high-value wire transfers.
    Integrated Cyber & Crime Package Both technical breach coverage and human-factor fraud. Enterprises seeking a holistic, consolidated insurance strategy.

    How Social Engineering Attacks Target Businesses

    To understand the necessity of specialized insurance, one must look closely at the tactical execution of these attacks. The landscape in 2026 is defined by the automation of human-centered deception. Threat actors no longer rely on spray-and-pray tactics; they employ sophisticated, AI-driven scripts that adapt to the target’s specific operational environment. By observing email traffic patterns, these groups identify who holds the authority to initiate payments, who is most likely to be stressed during month-end closing, and who might be distracted by seasonal hiring surges.

    One of the most persistent attack vectors remains the “Invoice Hijack.” In this scenario, an attacker gains access to a vendor’s email system. They monitor the communication flow between the vendor and the victim’s accounts payable department. Once an invoice is due, the attacker sends an email from the vendor’s real account—or a deceptively similar one—stating that their banking information has changed. They provide new routing and account numbers, often including an attachment that looks identical to a standard invoice, down to the company logo and font. The victim’s employee, seeing no reason to doubt the request, updates the system. The next payment is effectively sent to the criminal’s account, often untraceable by the time it is discovered.

    Another dangerous iteration is “Executive Impersonation” or “CEO Fraud.” The attacker targets mid-level employees with access to financial accounts. The communication usually begins as a low-stakes email—a quick “Are you at your desk?” to gauge availability. Once the employee responds, the “CEO” explains that they are in a confidential acquisition meeting and need an urgent, discrete transfer of funds to finalize the deal. By creating a culture of secrecy, the attacker discourages the employee from following standard verification protocols, such as calling the CEO directly to confirm the request. The speed at which these transfers occur is the primary goal; once the money hits the first intermediary bank, it is often moved into a series of shell accounts globally within minutes.

    The rise of deepfake technology has further complicated this. By 2026, many organizations have reported incidents where video or audio calls were manipulated to mimic the appearance or voice of an executive. An employee may participate in a brief video call that appears legitimate, only to find later that the video was a synthetic reconstruction designed to build false trust. Traditional phishing protection for business often focuses on email filtering, but these new, high-tech methods of engagement represent a physical and psychological shift in the battlefield. Because these attacks target the subjective experience of the employee—their trust in their leader or their professional sense of duty—they are exceptionally difficult to flag using standard spam-filtering software. This confirms the reality that human vulnerability is the most difficult variable to secure, and financial protection via insurance is the final, essential layer of defense.

    What Social Engineering Fraud Insurance Typically Covers

    When an organization invests in social engineering fraud insurance, it is purchasing more than just a reimbursement mechanism; it is securing a safety net for the inevitable “human factor” in digital business. While policy language varies significantly by carrier, comprehensive coverage typically focuses on the financial loss directly resulting from the intentional misleading of an employee. This coverage is often distinct from traditional cyber insurance, which emphasizes the aftermath of a server breach.

    Most policies will cover “Direct Financial Loss.” This refers to the actual funds stolen from the company’s bank accounts as a result of fraudulent instructions. If an employee is tricked into initiating a wire transfer to a threat actor, the insurance is intended to replace those funds. However, it is vital to note that this is usually subject to a specific sub-limit within the broader cyber policy. Unlike standard cyber insurance, which may have very high limits for things like PR firms and legal counsel, social engineering sub-limits are often lower, reflecting the increased frequency of these events.

    Additionally, modern policies often provide coverage for the “Extra Expenses” incurred during the investigation of the event. This might include hiring specialized digital forensic experts to determine whether the event was confined to a social engineering attack or if it involved a wider compromise of the internal network. Identifying the scope of the threat is a critical step that many businesses fail to account for until they are in the middle of a crisis. Having an insurance policy that explicitly funds this level of investigation ensures that the business can get back to operations quickly rather than being paralyzed by uncertainty.

    Furthermore, many policies offer “Crisis Management” and “Public Relations” support. If a business loses a significant amount of money through fraud, the reputational impact can be just as damaging as the financial loss. This is particularly true for firms that handle sensitive client funds or operate in the financial services sector. Insurance providers may cover the costs of reputation management services, which help the business navigate the communication strategy with stakeholders, investors, or clients to maintain confidence after an incident. This holistic approach ensures that the impact of the fraud is contained not just at the balance sheet level, but at the organizational level as well.

    Finally, some advanced policies now include coverage for the cost of re-training and re-securing the environment post-incident. This includes funds for implementing better phishing protection for business, conducting company-wide security audits, or paying for updated employee training programs to prevent a recurrence. By covering both the immediate financial loss and the long-term remediation, social engineering fraud insurance acts as a partner in risk management. It encourages the business to adopt a more resilient posture, acknowledging that while security can never be perfect, the ability to recover from a sophisticated deception is a hallmark of a mature, well-defended enterprise.

    Common Red Flags of Phishing and Business Email Compromise

    In the evolving threat landscape of 2026, the ability for employees to recognize the warning signs of a social engineering attack is the most significant tactical defense a company can deploy. While insurance is the financial backstop, employee vigilance is the frontline barrier. Organizations should treat these red flags not just as guidelines for an occasional seminar, but as a living part of the corporate culture. The most effective security training teaches staff to pause and verify when something feels even slightly “off.”

    The most common red flag in business email compromise is the “Sense of Unnatural Urgency.” Attackers rely on the fact that humans make mistakes when they are pressured. Whether it is an email demanding a wire transfer by the end of the day or a claim that a vendor’s invoice is overdue and will result in a service disruption, the primary goal is to bypass the employee’s critical thinking skills. Any communication that insists on immediate action while simultaneously requesting confidentiality—”do not tell anyone about this request”—should be treated as an immediate high-risk event.

    Another classic warning sign is the “Discrepancy in Communication Channels.” If a senior executive suddenly reaches out via a personal email address or an encrypted messaging app that is not typically used for company business, this is a major indicator of a potential compromise. Furthermore, if a vendor suddenly changes their bank account details, it is a non-negotiable rule that the employee must verify this through a known, trusted contact at the vendor—using a telephone number obtained from a known contract, not the number provided in the suspicious email. This simple, two-step verification process prevents the vast majority of BEC losses.

    Pay close attention to “Subtle Domain Variations.” Attackers frequently register domains that are one character off from the legitimate company domain, such as using an ‘rn’ instead of an ‘m’ or swapping a zero for an ‘o’. Most employees will glance at the sender’s display name and assume it is legitimate, never looking at the actual email header. Additionally, an unexpected change in tone or linguistic style is a critical indicator. If an executive who is usually concise and formal suddenly writes a rambling or grammatically informal email, that is an alarm bell. These small nuances, when identified by a vigilant employee, can stop a devastating wire fraud attempt in its tracks.

    Finally, encourage a culture of “Healthy Skepticism.” If an employee feels uncomfortable reporting a potential mistake because they fear repercussions, they are more likely to hide it, allowing the attacker more time to move the funds. A company that effectively integrates phishing protection for business understands that mistakes will happen. By creating a “no-blame” environment where employees are encouraged to report any suspicious communication—no matter how small—the company can trigger incident response protocols in minutes rather than hours. This proactive culture is the ultimate partner to your cyber insurance policy, ensuring that the business is protected by both sound strategy and human intuition.

    Real-World Costs of Social Engineering Incidents

    When businesses evaluate the impact of a social engineering attack, it is tempting to only count the immediate financial loss—the wire transfer that landed in a criminal’s account. However, experienced risk managers and forensic accountants understand that the true cost of a breach is a multi-layered financial burden that often threatens a company’s long-term solvency. In the landscape of 2026, where sophisticated deepfake audio and AI-driven phishing have become commonplace, the total cost of ownership for a breach includes far more than just the stolen funds.

    The primary cost is, of course, the direct loss of capital. Business email compromise (BEC) remains one of the most effective tools for threat actors, who meticulously mimic the communication styles of executives to trick employees into diverting payroll or vendor payments. Once the money is gone, recovery is statistically rare. While law enforcement agencies work to track these assets, international jurisdictional hurdles often make the retrieval of funds nearly impossible.

    Beyond the primary loss, businesses face significant forensic investigation costs. Before a claim can be filed under cyber insurance or social engineering fraud insurance, you must determine how the breach occurred. This requires hiring third-party cybersecurity firms to conduct a digital forensic audit. These experts must examine email server logs, cross-reference IP addresses, and identify the point of entry to ensure the vulnerability is closed. These services are billed at premium rates and, in many cases, can run into tens of thousands of dollars regardless of whether the lost funds are recovered.

    Legal and regulatory costs also accumulate rapidly. If the social engineering attack involved the theft of Personally Identifiable Information (PII) or protected customer data, the company may be legally required to provide identity theft monitoring services to affected parties. Additionally, privacy regulators may launch investigations, necessitating specialized legal counsel. For businesses operating in regulated sectors—such as finance, healthcare, or legal services—the potential for fines and non-compliance penalties often outweighs the initial wire fraud loss itself.

    Finally, there is the intangible but devastating cost of reputational damage. When stakeholders, clients, or partners learn that a company was easily duped by a phishing campaign, trust is compromised. This can lead to contract terminations, difficulty renewing professional liability insurance at favorable rates, and a decline in future revenue. In 2026, transparency is expected; however, the public relations strategy required to manage the narrative following a breach is yet another expense that businesses must factor into their risk assessment models.

    Who Needs This Coverage the Most in 2026?

    While every business with a digital footprint faces some level of risk, certain operational profiles make social engineering fraud insurance an essential component of their defensive strategy. As threat actors continue to evolve, they are no longer just targeting multinational corporations; they are actively scanning for mid-market firms that have significant cash flow but perhaps lack the enterprise-level security architecture of a Fortune 500 entity.

    Organizations with high-volume accounts payable (AP) departments are at the highest risk. If your business regularly processes wire transfers for international vendors, inventory, or construction milestones, you are a primary target. In these settings, the “human factor”—the reliance on individual employee judgment—is the weakest link. Even with robust software, a single tired or distracted employee can be manipulated into changing a vendor’s payment routing information.

    Professional services firms, such as law firms, accounting practices, and real estate brokerages, also occupy a high-risk category. These entities handle large sums of money on behalf of clients, often through escrow or trust accounts. A breach of these accounts is not only a financial nightmare but a professional liability catastrophe that could result in the loss of licensing or malpractice litigation. For these firms, wire fraud insurance is not just an elective expense; it is a fiduciary responsibility to their clients.

    Startups and technology companies in the growth phase also require specialized coverage. These businesses are often in a state of rapid flux, with new employees joining frequently and processes being updated constantly. This lack of institutional stability creates “process gaps” that attackers love to exploit. A large, unexpected loss from a social engineering incident can completely derail a funding round or lead to the closure of a business that hasn’t yet reached a state of consistent profitability.

    Business Type Primary Exposure Best For
    Accounting/Law Firms Trust account/Escrow fraud Comprehensive Professional Liability & Fraud
    E-commerce Retailers Vendor impersonation/Phishing Business Email Compromise Protection
    Manufacturing/Supply Chain Invoice manipulation Wire Fraud Insurance
    Tech Startups CEO Fraud/Social Engineering Standalone Cyber Crime Coverage

    How to Assess Your Exposure to Fraud Risks

    Assessing your risk is an exercise in honesty. Many business owners approach this task by looking at their antivirus software and declaring themselves “safe.” However, social engineering does not typically target the software; it targets the human. To assess your risk, you must conduct a thorough audit of your internal workflows and power structures.

    Start by mapping your financial approval chains. Who has the authority to initiate a wire transfer? Is there a mandatory “two-person rule” that requires a secondary check by a different individual before funds are moved? If your internal protocol allows a single employee to move significant capital based on an email request, your exposure is extreme. Experts often suggest that companies without a strict multi-stage verification process for financial transactions are effectively uninsurable or, at best, ineligible for favorable premium rates.

    Next, evaluate the “culture of accessibility.” Are your executives’ names, roles, and email structures easily found on your website? In 2026, attackers use AI tools to scrape LinkedIn and corporate websites to build highly realistic profiles of your team. If an attacker can easily identify your CFO and your Controller, they can map the relationship between them, making their phishing attempts far more convincing. Determine what information you are broadcasting and whether it provides a roadmap for an attacker.

    Perform a “mock phishing” test. There are many affordable security services that will send controlled, simulated phishing emails to your staff. Monitor the results closely: how many people clicked the link? How many replied with sensitive information? This data provides a clear metric of your company’s resilience to social engineering. If your click-through rate is high, your exposure is high, and your need for insurance—coupled with training—is urgent.

    Finally, review your existing insurance policies. Many general liability policies explicitly exclude losses caused by voluntary transfers of funds, even if that transfer was induced by fraud. Read the definitions in your current policy documents carefully. If you see exclusions for “voluntary parting of property” or “authorized wire transfers,” you are not covered for modern social engineering tactics. Understanding these gaps is the most critical step in identifying your true financial risk.

    Best Practices for Preventing Social Engineering Attacks

    Preventing social engineering requires a blend of technological safeguards and, more importantly, a cultural shift within the workplace. While phishing protection for business software, such as advanced email filtering and DMARC protocols, is essential, these tools only filter the incoming noise. They cannot stop a sophisticated, “human-first” attack that bypasses the inbox entirely.

    Implement a “Verified Outside of Email” policy. This is the single most effective defense against business email compromise. Any request to change a payment destination, update bank account details for a vendor, or move money into an account must be verified through a secondary, trusted channel. This could be a pre-established phone number that is kept on file and never included in the email request itself. If the request comes via email, the verification must happen via phone or in-person conversation.

    Continuous, mandatory training is the next pillar of defense. In the past, annual “security awareness” videos were the norm. Today, that is insufficient. Modern training should include interactive modules that show employees what a deepfake voice or a spoofed domain actually looks like. It is important to foster a culture where employees feel empowered to ask questions or delay a payment without fear of retribution from management. Often, the victim of a social engineering attack is an employee who was trying to be “helpful” or “efficient” to satisfy a boss’s urgent demand.

    Technical controls should be hardened as well. Use hardware-based multi-factor authentication (MFA) rather than SMS-based codes where possible. While SMS codes are better than nothing, they can be intercepted via SIM-swapping attacks. Hardware keys provide a much higher level of assurance. Additionally, ensure that your email gateway is configured to label external emails clearly. This helps employees immediately identify that an email, even if it looks like it came from the CEO, originated from outside the organization’s walls.

    Finally, limit the data you publish publicly. If you do not need to list the names and email addresses of your entire AP team on your website, remove them. Use a generic, monitored “billing@” or “accounts@” alias that is heavily guarded by security protocols. By reducing your digital footprint, you make it harder for attackers to conduct the reconnaissance required to craft a convincing, personalized fraud attempt.

    Integrating Fraud Coverage Into Your Insurance Portfolio

    Social engineering fraud insurance should never be viewed as a standalone safety net, but rather as one layer in a robust risk-transfer strategy. To properly integrate this coverage, you must look at your insurance portfolio as a holistic defense mechanism. Start by checking for overlap. If you already carry a standard cyber insurance policy, determine if it includes “social engineering fraud” as an add-on or a sub-limit. Many policies offer a small, “token” amount of coverage for fraud—sometimes as little as $25,000 or $50,000. If your typical wire transfers are in the six-figure range, this sub-limit is woefully inadequate.

    When you sit down with your insurance broker, ask specifically for “social engineering endorsement” or “voluntary parting coverage.” These terms are critical because they override the standard exclusions found in older commercial crime policies. Ensure that the policy language covers not just the theft of funds, but also the costs associated with the response, such as forensic IT services, legal fees, and notification costs if data is compromised.

    Coordinate this coverage with your directors and officers (D&O) insurance. If a massive social engineering attack leads to a catastrophic financial loss, shareholders or investors may sue the board of directors for failing to implement proper controls. A well-integrated insurance portfolio ensures that you are covered both for the immediate loss (via your fraud/cyber policy) and for the derivative litigation that often follows (via your D&O policy).

    Finally, make the policy a “living document.” Your risk profile changes every time you add a new vendor, expand to a new country, or update your payment software. Revisit your policy limits annually. If your revenue has grown or your transaction volume has increased, ensure your coverage limits keep pace. By treating your insurance coverage as an evolving strategic asset rather than a “set it and forget it” expense, you ensure your business remains resilient even when the unexpected occurs.

    Frequently Asked Questions

    Is social engineering fraud covered by standard general liability insurance?

    In almost all cases, the answer is no. Standard general liability policies are designed to cover bodily injury and property damage. They typically contain specific exclusions for “voluntary parting of property,” which means if an employee is tricked into sending funds, the insurance company will argue the transfer was voluntary, even if it was based on a fraudulent request. You need a dedicated cyber crime or social engineering policy to bridge this gap.

    What is the difference between cyber insurance and social engineering coverage?

    Cyber insurance is a broad category that typically covers first-party and third-party losses resulting from data breaches, ransomware, and system failures. Social engineering coverage is often an add-on to these policies that specifically addresses the human-deception aspect of fraud. While cyber insurance covers the “technological” theft of data, social engineering insurance covers the “psychological” theft of assets.

    Can an AI-generated voice really trick an insurance carrier into paying a claim?

    Insurance carriers have become increasingly sophisticated in their forensic analysis of claims. If a company suffers a loss due to a deepfake, the burden of proof rests on the insured to demonstrate that the loss resulted from the deception. Providing logs, forensic reports, and security audit data is essential. If you can prove that you had reasonable protocols in place and were still deceived by an advanced AI attack, coverage is generally applicable under a well-drafted policy.

    How much does social engineering fraud insurance typically cost?

    The cost varies significantly based on the size of your business, the industry you operate in, your total revenue, and the strength of your existing security controls. Insurers look at your “security posture”—how often you train staff, whether you have MFA, and your history of claims—to set premiums. A small business might pay a few hundred dollars a year for a sub-limit, whereas large enterprises pay significantly higher premiums for tailored, high-limit policies.

    Should small businesses prioritize this over traditional property insurance?

    They should not be viewed as competitors, but rather as distinct necessities. Property insurance covers your physical office and equipment; social engineering insurance covers your liquid assets. For a small business, a successful wire fraud attack can be more immediately fatal than a fire in the office. If you are operating in a digital-first environment, you should prioritize ensuring both areas are adequately protected, as the loss of cash flow is often more difficult to recover from than the loss of equipment.

    What happens if I don’t have this coverage and get hit by a BEC attack?

    If you lack this coverage, the financial loss is usually absorbed entirely by the business. You will be responsible for the full amount of the stolen funds, as well as all associated forensic, legal, and operational recovery costs. Without insurance, many small to mid-sized businesses find themselves unable to recover, as the depletion of working capital can lead to an inability to pay vendors, employees, or taxes, creating a cascade of financial failure.

    Conclusion

    As we navigate 2026, the threats facing businesses have shifted from simple technical exploits to highly sophisticated campaigns of psychological manipulation. Social engineering fraud has become a dominant challenge, targeting the human element of your organization in ways that firewalls and antivirus software simply cannot stop. While the best defense is always a combination of rigorous process controls and constant employee education, no organization is truly immune to the ingenuity of modern cybercriminals.

    Social engineering fraud insurance provides a vital safety net, transforming a potentially ruinous event into a manageable financial incident. It is an essential component of a modern business strategy, ensuring that when technology, policy, and human judgment fail, your organization has the financial resilience to survive and continue its mission. Do not wait until an incident occurs to evaluate the strength of your coverage. Take the time to assess your exposures, harden your internal protocols, and speak with your insurance advisor today to ensure your business is protected against the evolving landscape of digital crime.

    By insureiqguru Editorial Team

  • Event Cancellation Insurance: Is It Worth It for Your Business?

    Event Cancellation Insurance: Is It Worth It for Your Business?

    Key Takeaways

    • Event cancellation insurance serves as a critical financial safety net against non-refundable costs and lost revenue when events are forced to change or postpone.
    • Coverage is highly customizable, often spanning natural disasters, venue damage, and key speaker absences, but it is not a catch-all for poor planning.
    • Understanding the distinction between cancellation policies and event liability coverage is essential for comprehensive business risk management.
    • Exclusions, such as communicable diseases or lack of ticket sales, are common traps; reading the policy fine print is mandatory for any business stakeholder.
    • The decision to invest in a policy depends on the ratio of sunk costs to your organization’s tolerance for financial loss.

    Planning a corporate event is an exercise in meticulous orchestration, involving months of vendor negotiations, venue bookings, and marketing spend. Yet, despite the most detailed logistical plans, the uncontrollable nature of the world means that disruptions are an inherent reality of the business landscape. From extreme weather events that render a venue inaccessible to unexpected crises that force a mandatory cancellation, the financial fallout can be catastrophic for an organization’s bottom line. This is where event cancellation insurance becomes a vital instrument in a company’s risk mitigation strategy. By transferring the financial risk of non-refundable expenses and loss of profit to an insurer, businesses can safeguard their capital and ensure their long-term stability regardless of the unexpected hurdles that may arise during the event lifecycle.

    What Is Event Cancellation Insurance and How Does It Work?

    At its core, event cancellation insurance is a specialized financial product designed to protect a business from the unforeseen loss of revenue and non-recoverable expenses associated with a planned event. When an organization commits to hosting a conference, trade show, or product launch, it inevitably faces significant upfront expenditures—deposits for venues, travel arrangements, speaker fees, catering contracts, and technology rentals. If the event is forced to cancel, postpone, or relocate due to a cause beyond the organizer’s control, these funds are often locked into contracts, leading to direct financial depletion.

    The mechanism behind event cancellation insurance functions as a contract of indemnity. The insurer agrees to compensate the policyholder for specifically defined financial losses sustained due to covered perils. These policies are generally written on a bespoke basis, meaning that a policy for a high-profile technology summit will look drastically different from a policy for a regional networking seminar. The process typically begins with an assessment of the “exposure,” which is the total amount of money the business stands to lose if the event were to fail. The business provides a detailed budget, and the underwriter analyzes the probability of various risks—ranging from severe weather to regional civil unrest—to determine the premium.

    Once the policy is in effect, the insurance remains active through the planning and execution stages. If a covered peril occurs, the business initiates a claim by providing proof of the financial commitments made. It is critical to understand that this insurance is not a substitute for standard business insurance; rather, it is a narrow-focused product aimed at event-specific risks. Unlike standard corporate event insurance that might focus on property damage, cancellation coverage specifically addresses the inability to hold the event as scheduled. This ensures that when the “unthinkable” happens, the balance sheet remains intact, allowing the business to pivot or reschedule without the weight of wasted capital hanging over its head.

    Why Businesses Face Financial Risk From Event Disruptions

    For many modern enterprises, events are no longer just supplementary marketing tactics; they are core revenue drivers and brand-building milestones. When a company invests heavily in a corporate function, it creates a “sunk cost” profile that is often highly vulnerable to external pressures. Financial risk in this context is twofold: there is the literal loss of the cash spent on non-refundable vendors, and there is the opportunity cost—the potential revenue or lead generation that evaporates when the event disappears from the calendar.

    Market analysts often observe that small to mid-sized businesses are particularly sensitive to these risks. A large conglomerate might absorb the loss of a five-figure deposit with minimal operational impact, but for a startup or a mid-sized firm, such a loss could jeopardize a quarter’s profitability. Furthermore, the modern event environment is increasingly global. Corporate event insurance must now account for international travel disruptions, political volatility in host regions, and the fragility of digital infrastructure that supports hybrid events. A single logistical breakdown, such as a labor strike at a transport hub or a sudden power failure at a primary venue, can trigger a domino effect of cancellations.

    Beyond the direct financial hit, there is the issue of contractual obligations. Most venue and vendor agreements contain “force majeure” clauses, yet these clauses are often narrowly defined and frequently contested. Relying solely on the legal wording of a vendor contract is risky; if a court determines that the disruption did not technically meet the criteria of “act of God,” the business remains on the hook for the full contract value. Event cancellation insurance bridges this legal gap. It does not rely on the cooperation of the venue or the interpretation of a lawyer; it provides a direct, contractually guaranteed path to recouping costs. By securing this financial stability, companies protect their ability to reinvest in future projects, thereby maintaining their competitive edge in a fast-paced market. Ignoring this risk, or assuming that “everything will go to plan,” is essentially a gamble that many CFOs are no longer willing to take given the current volatility of global logistics and climate patterns.

    What Does Typical Event Cancellation Coverage Include?

    When businesses investigate the scope of an event cancellation policy, they often find that the coverage is more modular than they initially anticipated. The primary objective of any robust policy is to replace the “out-of-pocket” losses that occur when an event is curtailed or moved. Standard inclusions generally start with the reimbursement of non-refundable deposits for venue hire, audio-visual equipment, and event production services. If a policyholder has paid a talent fee to a keynote speaker or a performer, and the event is forced to cancel for a covered reason, the policy will generally reimburse the portion of the fee that the organizer cannot recover from the talent.

    Many policies also extend to cover the costs of “abandonment.” This refers to situations where the event begins but cannot continue to its natural conclusion. For example, if a severe storm forces an outdoor event to shut down halfway through the day, the insurance may cover the wasted costs associated with the remaining portion of the event, such as catering for a dinner that was never served or staffing for a session that never occurred. Another key component is the protection of marketing and promotional spend. Companies often spend significant sums on digital advertising, printing, and branding leading up to an event. If the event is canceled, these costs are essentially lost, and comprehensive policies usually include provisions for these expenditures.

    Some premium policies go a step further, covering the loss of profit. This is essential for trade shows or ticketed conferences where the business relies on entry fees or booth rentals to turn a profit. In the event of a cancellation, the insurer pays the expected net income that the company would have generated had the event proceeded as planned. When evaluating which type of policy is best, companies should consider the following comparison of typical approaches:

    Approach Key Focus Best For
    Standard Cancellation Policy Recouping sunk costs, deposits, and vendor fees. Smaller workshops, team-building retreats, or small-scale internal meetings.
    Comprehensive Revenue Protection Sunk costs plus projected profit and lost ticket revenue. High-stakes trade shows, ticketed conferences, and events with significant revenue goals.
    Special Peril Endorsement Coverage for specific risks like civil unrest or adverse weather. Events held in locations with known instability or volatile weather patterns.

    It is important to note that these coverages are not automatic. They are usually selected as “riders” or endorsements on the master policy. For example, a business might opt for basic cancellation coverage but add a specific rider for “key speaker non-appearance” if the success of the event hinges on a single, high-profile individual whose absence would necessitate canceling the entire program.

    Common Exclusions in Event Insurance Policies

    The beauty of event cancellation insurance lies in its ability to offer peace of mind, but the “fine print” is where many businesses find themselves at odds with their insurers. Understanding what is *not* covered is just as critical as understanding what is. Perhaps the most significant exclusion in modern policies involves communicable diseases and pandemics. Since the global disruptions of the early 2020s, many insurers have tightened their language significantly. Unless specifically negotiated and paid for as a separate high-cost add-on, most general policies will not cover cancellations driven by public health orders or viral outbreaks.

    Another common exclusion pertains to “lack of attendance” or “lack of sales.” An insurance policy is designed to cover fortuitous, external events—not the commercial failure of a concept. If a business decides to cancel an event because they only sold 20% of the tickets, they cannot file an insurance claim for the lost revenue. The event must be canceled due to an external force (such as a fire, flood, or government intervention), not due to a strategic business decision or a lack of interest from the target audience. This is a vital distinction for event planners who are concerned about the financial viability of a launch; insurance covers the disaster, not the poor performance.

    Furthermore, policies usually exclude instances where the business was aware of a potential risk before purchasing the policy. For instance, if an event is planned for an area currently experiencing active civil unrest and the policy is purchased after that unrest has become widely publicized, the insurer will likely deny a claim if that unrest eventually disrupts the event. Insurance is intended for unpredictable future events; it cannot be used to mitigate a risk that is already unfolding. Additionally, most policies have specific requirements for “due diligence.” If an event is canceled because a venue failed to meet basic safety codes that the organizer should have inspected beforehand, the insurer may argue that the organizer was negligent, leading to a claim denial. Maintaining thorough records of venue vetting and vendor contracts is essential to ensuring that exclusions are not triggered by a perceived lack of professional oversight on the part of the organizing team.

    When Is It Worth Purchasing Special Event Insurance?

    Deciding whether to allocate budget toward special event insurance requires a pragmatic cost-benefit analysis. The cost, often referred to as the event insurance cost, is a variable premium determined by the total budget of the event, the location, the duration, and the risk profile of the activities involved. If you are hosting a small internal team-building day with a budget of a few thousand dollars at a local office space, the premium may outweigh the potential loss, and the risk might be considered “self-insurable.” In such cases, the business can simply absorb the loss if the event is canceled.

    However, when the financial stakes reach a point where a total loss would disrupt the company’s annual budget or lead to cash flow problems, insurance becomes a logical expense. A general rule of thumb used by risk managers is to look at the “recoverability ratio.” If more than 50% of your event budget is tied up in non-refundable contracts (such as non-cancelable venue deposits or international flights), the argument for insurance becomes compelling. Furthermore, if your company’s brand reputation is highly sensitive to cancellations—for instance, if you are hosting a major press launch for a new product where a cancellation would signal instability to the market—the indirect cost of a cancellation far exceeds the premium.

    Consider the nature of the event as well. Events occurring in “high-risk” locations or during seasons prone to extreme weather (such as hurricane season in coastal areas or winter in regions with heavy snowfall) automatically carry a higher risk profile. In these cases, the insurance premium acts as a stabilizing force, allowing the business to proceed with confidence. Additionally, if you have specific event insurance requirements imposed by a venue contract—which is common for large convention centers or luxury hotels—the decision is often made for you. These venues often mandate a minimum level of liability coverage, and it is frequently efficient to bundle your cancellation coverage with your required liability policy. Ultimately, the question is not “What is the cost of the insurance?” but rather “What is the cost of a total loss?” If the latter figure is large enough to impact your organization’s mission, the insurance is not merely an optional add-on; it is a fundamental pillar of sound corporate governance.

    How to Calculate the Potential Cost of an Event Cancellation

    Calculating the potential financial impact of a cancelled event requires a comprehensive audit of your event budget. To determine if event cancellation insurance is a sound investment, you must move beyond the basic venue rental fee. Start by aggregating every sunk cost that would be impossible to recover if the event were terminated suddenly.

    Begin with non-refundable deposits. Many vendors—including high-end catering firms, keynote speakers, and audiovisual production companies—require substantial non-refundable retainers. In a cancellation scenario, these funds are typically lost immediately. List each vendor, the deposit amount paid, and the timeline for when the remaining balance becomes due. If you cancel after a specific date, you may be liable for the entire contract value, not just the deposit.

    Next, account for internal labor costs. While you might not pay your staff an “hourly rate” for planning, the opportunity cost is significant. Calculate the man-hours invested by your marketing, operations, and logistics teams. If the event is cancelled, those hundreds of hours of internal labor become a sunk expense that generates zero return on investment.

    Factor in marketing and promotional collateral. Any physical print materials, branded merchandise (swag), or targeted digital advertising campaigns created specifically for this event are essentially wasted if the doors never open. If you have already paid for satellite broadcasting, specialized fiber-optic lines for livestreaming, or international travel bookings for staff, these must be added to your risk assessment.

    Finally, consider the revenue side of the equation. If your event relies on ticket sales, registrations, or sponsorship tiers, calculate the total potential gross revenue. If the cancellation clause in your sponsorship contracts requires you to refund sponsors, that revenue gap becomes an immediate liability. By summing your total non-recoverable expenses and your potential lost revenue, you arrive at your “Total Financial Exposure.” This number serves as the baseline for the amount of coverage you should seek when purchasing corporate event insurance.

    Factors That Influence Your Event Insurance Premiums

    The cost of securing an event cancellation policy is not a flat rate; it is a calculation based on your specific risk profile. Insurers evaluate several key metrics before providing a quote. Understanding these variables allows you to adjust your planning to potentially lower your premiums.

    Geographic Location and Venue Selection: An event held in a region prone to severe weather, such as coastal areas during hurricane season, will naturally command higher premiums than an event held in a climate-controlled, stable environment. Furthermore, the type of venue matters; an outdoor festival in a remote location carries higher risks than a professional conference held in a modern, well-equipped convention center.

    Duration and Scale: The length of the event and the expected number of attendees correlate directly to your risk profile. A three-day international conference involves more moving parts, more vendors, and a higher probability of disruption than a one-day networking cocktail hour. Simply put, the more logistical points of failure, the higher the insurance company’s exposure.

    Event Type and Content: High-risk activities, such as demonstrations involving heavy machinery, pyrotechnics, or athletic competitions, significantly influence your special event insurance cost. Events that feature high-profile keynote speakers also increase financial risk; if that speaker cancels, your entire event may lose its value, triggering a claim.

    Experience and History: If your organization has a documented history of successfully managing events, underwriters may view you as a lower risk. Providing a detailed risk management plan—demonstrating that you have considered fire safety, security, and contingency planning—can often help in negotiations regarding premium rates.

    The Level of Coverage: Finally, the scope of your policy is the most direct driver of cost. A basic policy covering only “force majeure” events will be cheaper than a comprehensive policy that covers “non-appearance” of essential talent or pandemic-related disruptions. Choosing a higher deductible can reduce your premium, but you must ensure your business can absorb that cost if a claim arises.

    Event Cancellation vs Event Liability: Understanding the Difference

    A common mistake among business planners is assuming that event cancellation insurance and event liability coverage are the same thing. In reality, they protect against entirely different categories of financial loss.

    Coverage Type Primary Purpose Best For
    Event Cancellation Protects your organization from financial loss due to events you cannot control. Large-scale conferences, trade shows, and events with high non-refundable costs.
    Event Liability Protects you if a third party is injured or property is damaged during your event. Any event where attendees, staff, or public property are present.
    Non-Appearance Insurance Specific protection if a keynote speaker or star performer fails to show up. Events reliant on a single high-profile individual to drive attendance.

    Event cancellation insurance is effectively an “income protection” or “expense reimbursement” policy. It is designed to save your business from bankruptcy if the event you invested in must be abandoned. If a flood prevents your venue from opening, or a power grid failure makes the event impossible to host, this insurance helps you recover the deposits and expenses you paid in advance.

    Conversely, event liability coverage is a “defensive” policy. If a guest trips over a loose cable and sues your company, or if your stage setup accidentally damages the host hotel’s flooring, liability insurance covers the legal costs, medical bills, and settlement amounts. You should view these as complementary components of a robust business event protection strategy rather than alternatives.

    Steps to Filing a Successful Event Cancellation Claim

    Filing a claim can be a high-stress endeavor. To ensure the process is as smooth as possible, your administrative preparation must begin the moment the policy is bound. If a disaster forces you to cancel, follow these professional steps:

    1. Notify Your Insurer Immediately: Do not wait. Most policies have strict notification requirements. Contact your broker or the insurance carrier as soon as the decision to cancel is finalized.
    2. Mitigate Further Losses: Your policy likely requires you to take reasonable steps to reduce the financial loss. If you cancel early, you may be able to negotiate partial refunds from vendors. Keep records of these attempts, as showing you tried to save costs can support your claim.
    3. Compile Exhaustive Documentation: Create a digital folder containing your original contract, your proof of payment for every vendor, the formal cancellation notice from the venue or government entity, and all internal planning documentation.
    4. Maintain a Clear Narrative: Write a concise report detailing the exact cause of the cancellation. If it was due to weather, include meteorology reports. If it was due to a vendor failure, include the communication records leading to the breakdown.
    5. Monitor Communication: Stay in constant contact with your claims adjuster. Provide requested information promptly and keep a log of all phone calls and emails.

    Best Practices for Risk Management When Planning Corporate Events

    Insurance should be your safety net, not your first line of defense. A superior risk management strategy involves identifying hazards before they manifest into a claim. Begin by conducting a “Pre-Mortem” analysis: ask your team, “If this event were to be a total disaster, what would have been the cause?” This exercise often reveals overlooked risks, such as reliance on a single transit route or a fragile supply chain.

    Diversify your vendor contracts. When possible, avoid paying 100% of the cost upfront. Negotiate payment milestones that align with deliverables. Ensure your contracts include “force majeure” clauses that clearly define what constitutes an unavoidable occurrence, which may allow you to terminate agreements without full penalty.

    Establish a physical and digital security protocol. For in-person events, coordinate with the venue regarding emergency exits, medical stations, and crowd control. For virtual or hybrid components, ensure your cybersecurity measures are robust. A data breach during a virtual event can be just as damaging as a physical cancellation.

    Finally, keep a “Go/No-Go” decision matrix. Define the threshold for cancellation ahead of time. For example, if a storm is forecasted for 48 hours before the event, decide at what point you will trigger the cancellation to minimize unnecessary vendor fees. By having a pre-approved plan, you remove the emotion from the decision and protect the company’s bottom line.

    Frequently Asked Questions

    Is event cancellation insurance required by law?

    No, there is no federal or state law that mandates businesses to purchase event cancellation insurance. However, many private venues and convention centers require proof of general liability insurance as part of their rental agreement to protect their property from damage.

    Can I purchase insurance after I have already started planning my event?

    Yes, you can purchase coverage after planning has begun, but you may face significant limitations. Many insurers require policies to be purchased a specific number of days before the event. If a threat, such as an approaching storm, is already known, the insurance company will likely issue a “known peril” exclusion, meaning they will not cover that specific risk.

    Does a standard business owner’s policy (BOP) cover my event?

    Typically, no. A standard business owner’s policy is designed for daily operations, such as property damage to your office or general liability for your business premises. It rarely extends to the complex, specific risks associated with hosting external, one-off events.

    What is a deductible in event insurance?

    A deductible is the portion of a financial loss that you agree to pay out of pocket before the insurance company begins to reimburse your expenses. Choosing a higher deductible often lowers your monthly or upfront premium, while a lower deductible provides more comprehensive protection at a higher cost.

    What does “non-appearance” mean in a policy?

    Non-appearance coverage is a specific endorsement that protects you if a key individual—such as a celebrity guest, keynote speaker, or performer—fails to show up at your event due to illness, travel issues, or other covered circumstances, and their absence results in a significant loss of value for your event.

    Does event cancellation insurance cover pandemic-related closures?

    Following recent global events, many standard policies now exclude communicable diseases or pandemics unless a specific, additional rider is purchased. You should always read the “Exclusions” section of your contract carefully to see how the policy treats viral outbreaks or government-mandated health lockdowns.

    Conclusion

    Corporate events represent significant investments of time, capital, and reputation. While the excitement of planning can often overshadow the potential for disruption, a professional approach to risk management dictates that you prepare for the unexpected. Event cancellation insurance acts as a vital safeguard, ensuring that a single unforeseen disaster does not compromise your company’s financial stability or future growth.

    By accurately calculating your total financial exposure, distinguishing between liability and cancellation coverage, and implementing rigorous internal risk management practices, you can host your next event with confidence. Whether you are planning a local seminar or an international conference, the peace of mind provided by comprehensive insurance is an invaluable asset. Take the time to audit your upcoming event schedule today, review your vendor contracts, and speak with a qualified professional to build a safety net that aligns with your business goals.

    By insureiqguru Editorial Team

  • Employee Dishonesty Insurance: Is It Worth It for Your Business?

    Employee Dishonesty Insurance: Is It Worth It for Your Business?

    Key Takeaways

    • Employee dishonesty insurance acts as a vital financial safety net against losses caused by theft, fraud, and embezzlement committed by staff.
    • Internal fraud is a persistent risk that impacts businesses of all sizes, often remaining undetected for months or even years.
    • Fidelity bond insurance typically covers a broader range of illicit acts than standard property or general liability policies.
    • Many business owners incorrectly assume that their existing business owner’s policy (BOP) provides sufficient coverage for internal criminal acts.
    • Determining the necessity of coverage depends on your company’s risk profile, internal controls, and the level of exposure to liquid assets.

    The nightmare scenario for any business owner isn’t necessarily a fire, a flood, or a lawsuit from a disgruntled customer—it is the slow, methodical erosion of capital from within. When a trusted employee decides to exploit their position for personal gain, the damage inflicted is often far more than just financial; it creates a profound sense of betrayal that can dismantle company culture and threaten long-term viability. Protecting business assets against internal threats requires a proactive approach, and for many organizations, that strategy begins and ends with employee dishonesty insurance. As modern business operations become increasingly digitized and decentralized, the avenues for internal fraud have expanded, making it more critical than ever to understand the tools available to mitigate these risks. In this guide, the InsureIQGuru Editorial Team explores the nuances of fidelity coverage, why standard policies fall short, and how you can safeguard your firm against the silent threat of embezzlement.

    What Is Employee Dishonesty Insurance and How Does It Work?

    Employee dishonesty insurance, frequently referred to as commercial crime coverage, is a specialized financial product designed to indemnify an organization against the loss of money, securities, or property resulting from the illicit actions of its employees. While it is often conflated with other forms of commercial coverage, it functions quite differently from a standard general liability policy. Instead of protecting the business from third-party claims, this insurance serves as a specialized shield against internal actors.

    The mechanism behind this coverage is relatively straightforward but requires careful attention to detail during the underwriting phase. When a business purchases a policy, it defines the limit of insurance, the deductible, and the scope of covered positions or individuals. Unlike general insurance, which might be triggered by an accidental event like a slip-and-fall, employee dishonesty insurance is triggered by a criminal act. This act must be performed by a person—or a group—directly employed by the organization. The core intent of this insurance is to restore the balance sheet after a dishonest employee has funneled funds into private accounts, stolen physical inventory, or manipulated payroll data for their own benefit.

    To function effectively, these policies typically require the business to maintain rigorous internal controls. Insurance providers are not looking to subsidize poor management; they are looking to protect well-run companies from the “bad actor” who manages to bypass even the best oversight mechanisms. For instance, if an employee is consistently forging checks or siphoning funds through a ghost-employee payroll scheme, the insurance provider will conduct an audit once a claim is filed. The claimant must demonstrate that a loss occurred, quantify that loss, and provide evidence that it was the direct result of employee dishonesty.

    Moreover, the scope of “employee” is broadly defined in modern policies. It usually includes full-time, part-time, temporary, and even leased employees. Some policies can be extended to cover volunteers or independent contractors, depending on how the contract is structured. A critical aspect of how this insurance works is the concept of “discovery.” Most policies are written on a “discovery basis,” meaning the coverage applies to losses that are discovered during the policy period, even if the actual theft occurred in a prior year. This is vital because embezzlement often takes years to uncover. By maintaining consistent coverage, a business ensures that even if a crime started long ago, it remains protected once the discrepancy is finally brought to light. This long-term perspective is what makes internal fraud insurance a fundamental component of a comprehensive risk management strategy, distinguishing it from products that only cover immediate, visible damages.

    The Growing Threat of Internal Fraud and Embezzlement

    The landscape of internal fraud has changed dramatically over the last decade, evolving from simple cash skimming from a register into highly sophisticated digital embezzlement. As businesses shift toward cloud-based accounting and remote workforces, the physical barriers that once prevented easy access to capital have largely evaporated. This digital shift has unfortunately lowered the barrier to entry for potential fraudsters. Experts generally agree that internal fraud is one of the most common and damaging risks that businesses face today, precisely because it is committed by the people who know your systems, your weaknesses, and your security blind spots better than anyone else.

    Embezzlement does not look like a movie heist. It is typically a slow, quiet bleed. An employee might begin by altering small expense reports, escalating to larger unauthorized transfers once they realize the business owner is not closely monitoring bank reconciliations. In smaller enterprises, the problem is often exacerbated by a lack of “separation of duties.” When a single individual is responsible for receiving payments, recording them in the ledger, and reconciling the bank statements, they have the perfect opportunity to conceal their tracks. In this environment, the business owner relies entirely on the integrity of that individual. When that trust is abused, the result is internal fraud that can last for years before it is noticed.

    The economic impact of these crimes can be devastating, often reaching into the tens or hundreds of thousands of dollars. For a small business, a loss of this magnitude can lead to immediate insolvency, the loss of staff jobs, and the destruction of the owner’s personal credit. Beyond the financial drain, there is the hidden cost of investigation and prosecution. Businesses frequently find themselves in a position where they must hire forensic accountants to quantify the extent of the damage, legal counsel to handle the fallout, and potentially public relations professionals to manage the reputational damage if the fraud becomes public knowledge. All of these activities incur additional expenses that are not covered by standard insurance products.

    Internal fraud also feeds on complacency. Many business owners operate under the assumption that they have “good people” and therefore don’t need to worry about theft. However, history shows that fraud is often a crime of opportunity combined with personal desperation—whether it is gambling debts, medical bills, or general dissatisfaction. Even a loyal employee of twenty years can turn to embezzlement when their personal financial circumstances change drastically. By acknowledging that internal fraud is an ever-present risk rather than a rare anomaly, business owners can move toward a more objective posture. Implementing employee dishonesty insurance acts as a final fail-safe for when the internal controls fail to stop a determined perpetrator. In this context, protecting business assets is not just about keeping the doors locked; it is about having a financial recovery plan for the moments when the locked doors are bypassed by someone with a key.

    Coverage Type Primary Function Best For
    Employee Dishonesty Insurance Covers theft/fraud committed by direct staff members. Businesses with high-volume cash or asset handling.
    Fidelity Bond Insurance Guarantees against dishonest acts; often client-focused. Service providers visiting client premises.
    Cyber Crime Insurance Covers digital theft, social engineering, and hacking. Companies with heavy reliance on e-commerce.

    Types of Losses Covered by Fidelity Bonds

    To fully grasp the protection offered by fidelity bonds and crime coverage, it is essential to distinguish between the various forms of theft an employee might commit. Fidelity bond insurance is designed to cover specific categories of loss, and the breadth of these categories will vary significantly depending on the policy wording and the insurance carrier. In a standard commercial crime policy, the focus is usually on the loss of “money,” “securities,” and “other property.”

    Money and securities represent the most common target for embezzlers. This includes physical cash, checks, promissory notes, and electronic funds. Embezzlement often occurs via the manipulation of payroll, the creation of ghost employees, or the simple redirection of customer payments into personal accounts. Because these assets are liquid, the loss is immediate and often difficult to recover through legal action, as the funds are frequently spent long before the discovery of the crime. The fidelity bond acts to indemnify the firm for these direct financial losses.

    Beyond liquid assets, these policies also cover the theft of “other property.” This can include inventory, office equipment, or raw materials. For a retail business or a manufacturing firm, the theft of physical goods is a substantial risk. Employees who have access to the warehouse or the retail floor might gradually siphon off inventory to sell on third-party marketplaces. Because this type of theft is incremental—a few boxes of product here, a laptop there—it can avoid triggering inventory alarms for an extended period. When the annual physical audit reveals a massive discrepancy, the insurance can help recover the value of that stolen property, provided there is sufficient evidence of employee involvement.

    Another crucial area often covered by these policies is forgery and alteration. If an employee uses the business’s signature to create unauthorized checks or alters existing documents to authorize fraudulent transfers, the resulting loss is typically covered under the forgery clause of a fidelity policy. This is a critical distinction, as basic general liability policies almost never cover losses arising from documents that have been intentionally forged or manipulated by internal personnel.

    Furthermore, many comprehensive policies include coverage for computer fraud and wire transfer fraud committed by employees. As more companies move toward automated banking and electronic payments, the ability for an employee to bypass administrative controls and initiate a fraudulent wire transfer has increased. While specialized cyber insurance is often required for outside hacking incidents, the internal aspect—where a trusted employee uses their legitimate access rights to commit fraud—is the domain of employee dishonesty insurance. By understanding the specific types of losses covered, business owners can tailor their policies to match their specific risks. For instance, a construction company might prioritize coverage for physical equipment theft, whereas an accounting firm might place more weight on the coverage for financial document forgery and electronic funds transfer fraud. In every instance, the common denominator remains the same: the policy is there to replace value that was systematically taken from the company by its own staff.

    Common Myths About Commercial Crime Coverage

    Misunderstandings surrounding commercial crime insurance can leave a business dangerously exposed. Perhaps the most pervasive myth is that a standard Business Owner’s Policy (BOP) or commercial property policy covers employee theft. Many business owners feel a sense of security, believing that because they have “full” coverage, they are protected against all potential losses. However, standard property policies are typically designed to cover “perils of nature”—fire, wind, theft by outsiders, and vandalism. They specifically exclude the criminal acts of employees, agents, or business partners. If you file a claim for inventory lost to employee theft under a standard property policy, the denial is almost guaranteed, as the definition of covered perils rarely extends to internal dishonesty.

    Another common myth is the belief that internal controls are a substitute for insurance. While it is true that robust internal controls—such as dual-signature requirements, third-party audits, and background checks—are essential, they are not infallible. Even the most carefully constructed system of checks and balances can be undermined by two employees colluding to commit fraud. When two people in different departments agree to override the system, the controls are effectively neutralized. Believing that your processes are “too good” to allow for theft is a psychological bias that creates a blind spot. Insurance is not a replacement for good management; it is a safety net for when that management is inevitably tested by human error or malice.

    Some business owners also believe that employee dishonesty insurance is prohibitively expensive or only for large corporations. In reality, the cost of this coverage is often surprisingly manageable, especially when weighed against the potential loss from a single embezzlement event. Crime coverage is generally priced based on the size of the company, the number of employees, and the nature of the assets handled. For a small business, a low-limit policy can be obtained at a relatively modest premium, providing a significant return on investment should an incident occur. The cost of not having the coverage, by contrast, is a total loss of the stolen assets.

    Finally, there is the myth that internal fraud is easy to detect through regular oversight. Many believe that “if someone was stealing, I would notice.” This confidence is frequently shaken by the reality that sophisticated fraud often involves the manipulation of the very records that the owner uses for oversight. An employee who is familiar with your reporting style can craft reports that look perfect on the surface while masking systemic theft. By clearing up these myths, business owners can approach the decision to purchase internal fraud insurance with clarity and urgency. It is not about distrusting your staff; it is about recognizing that your business is an asset that deserves protection against all threats, both internal and external, regardless of how unlikely you feel the risk might be on any given day.

    Do Small Businesses Really Need Dishonesty Insurance?

    Small businesses often operate on tight margins where every dollar counts. This reality leads many owners to ask whether they can afford the luxury of employee dishonesty insurance. However, the more pressing question should be whether a small business can afford the catastrophic consequence of embezzlement. When a large corporation suffers an internal fraud event, it may be a line item in their annual report, an unpleasant surprise that they absorb without disrupting operations. When a small business suffers that same loss, it can represent years of profit, the inability to meet payroll, or the necessity to shutter the business entirely.

    Small businesses are particularly vulnerable because they lack the complex layers of oversight present in massive organizations. In a small shop or boutique firm, the person who manages the bank account is often the same person who processes orders and manages payroll. This centralization of power, while efficient, creates a massive “single point of failure.” If that person turns out to be dishonest, the business has no redundancy to prevent the theft. Therefore, small businesses actually have a higher proportional need for this coverage than large corporations. Their exposure is not mitigated by institutional checks, making insurance the primary mechanism for financial stability.

    Furthermore, small business owners often have a closer, more personal relationship with their employees. This can lead to a sense of comfort that prevents the implementation of necessary security measures. You might not want to perform a thorough audit of your bookkeeper’s work because you feel it signals distrust. Unfortunately, this emotional aspect of business ownership is exactly what fraudsters rely upon to commit their crimes. Having an insurance policy in place changes the culture from one based on blind faith to one based on professional accountability. It allows the owner to conduct audits and reviews as a matter of policy, rather than as a reaction to suspicion.

    Consider also the cost of recovery. If you do discover that an employee has stolen from you, recovering those assets is rarely as simple as asking for them back. Even if you pursue legal action, the perpetrator has often spent the money, and winning a judgment does not mean you will collect the funds. Insurance coverage provides a streamlined path to financial recovery, allowing you to focus on the future of your business rather than being mired in a years-long legal battle over stolen funds. Ultimately, the necessity of this coverage comes down to risk tolerance. If your business holds liquid cash, handles valuable inventory, or relies on digitized payments, you are inherently exposed to the threat of internal fraud. The question for the small business owner is not whether theft is happening right now, but whether they have the financial resilience to survive if and when it occurs. Investing in coverage is an investment in the longevity and survivability of the firm, providing peace of mind that allows the owner to focus on growth rather than constant suspicion.

    Employee Dishonesty Insurance vs Commercial Crime Insurance

    When shopping for protection against internal threats, business owners often encounter the terms “employee dishonesty insurance” and “commercial crime insurance.” While these terms are sometimes used interchangeably in casual conversation, they carry distinct meanings within the insurance industry. Understanding the difference is vital for ensuring your business is not left with unexpected coverage gaps.

    At its core, employee dishonesty insurance—often categorized under fidelity bond insurance—is a specialized subset of coverage. Its primary focus is narrow: indemnifying an employer for the direct financial loss caused by a fraudulent or dishonest act committed by an employee. This typically includes theft of money, securities, or property, whether the employee acts alone or in collusion with others.

    Commercial crime insurance, by contrast, is an umbrella policy. It is designed to cover a broader range of illicit activities that can cripple a business’s financial health. While it includes coverage for employee theft, it also typically covers external threats, such as forgery, robbery, burglary, computer fraud, and funds transfer fraud. By choosing a comprehensive crime policy, you essentially wrap your employee dishonesty coverage within a wider net that addresses both insider and outsider threats.

    Table 1: Employee Dishonesty Insurance vs. Commercial Crime Insurance

    Feature Employee Dishonesty (Fidelity Bond) Commercial Crime Insurance Best For
    Scope Internal threats (employees only) Internal and external threats Comprehensive protection
    Coverage Focus Direct loss from theft/embezzlement Theft, forgery, cyber fraud, robbery Businesses facing multifaceted risks
    Complexity Specialized and targeted Broad and modular Customizable risk management
    Cost Generally lower due to narrow scope Higher due to expanded coverage Budget-conscious small entities

    In practice, many mid-sized and large enterprises opt for a commercial crime policy because the modern threat landscape rarely limits itself to just one entry point. For example, a business that stores sensitive data may find that an employee is not just embezzling funds, but also facilitating an external cyberattack. In this scenario, a standard fidelity bond might not cover the damages resulting from the computer fraud component, whereas a crime policy would be structured to respond to both.

    How to Assess Your Business Risk for Internal Theft

    Assessing risk is the precursor to effective risk management. Before purchasing business embezzlement protection, you must perform a “vulnerability audit” of your financial and operational workflows. Many business owners make the mistake of assuming that “it won’t happen to me” because they trust their staff implicitly. However, the most effective internal fraud often occurs in environments where trust is absolute and oversight is nonexistent.

    Begin by mapping out your financial touchpoints. Identify exactly who has access to the business bank accounts, corporate credit cards, petty cash, and inventory management systems. Any position that combines the ability to record financial transactions with the ability to authorize those transactions is a high-risk role. This is known as a failure in “segregation of duties.” If a single employee can approve a vendor invoice, issue the payment, and reconcile the bank statement, your risk of internal fraud is significantly elevated.

    Consider the “Fraud Triangle,” a concept often cited by forensic accountants. Fraud typically occurs when three conditions intersect: pressure, opportunity, and rationalization. Assess your business for these elements:

    • Pressure: Are your employees facing significant financial strain, personal life crises, or excessive work pressure?
    • Opportunity: Is your internal accounting software accessible to too many people without audit logs? Do you perform surprise audits?
    • Rationalization: Does your workplace culture encourage the view that the business “owes” the employee, or that the company has “plenty of money” to spare?

    Furthermore, analyze your digital footprint. In the modern era, internal fraud insurance is increasingly tied to digital hygiene. How easy is it for an employee to bypass dual-authorization for wire transfers? Are passwords shared among team members? By documenting these gaps, you can better determine the level of coverage your business requires.

    Factors That Influence the Cost of Your Premiums

    Insurance carriers do not assign premiums based on guesswork. When underwriting employee dishonesty coverage, they utilize actuarial data to determine the likelihood of a loss. Several key factors can either inflate or reduce your annual premium.

    The primary driver is the size of your business as measured by gross revenue and employee headcount. A business with hundreds of employees and millions in monthly transactions is naturally exposed to higher potential loss events than a small boutique operation. Consequently, higher limits of insurance—the maximum amount the insurer will pay for a claim—will increase the premium cost.

    Your internal controls are arguably the most significant variable that you, as the business owner, can influence. Insurers often provide discounts to businesses that implement robust preventative measures. For example, if you can demonstrate that you utilize a dual-signatory requirement for all outgoing payments over a certain threshold, or that you use a third-party accounting firm to perform monthly reconciliations, the insurer perceives a lower risk. This decrease in perceived risk directly correlates to lower premiums.

    The nature of your industry also plays a critical role. Businesses dealing with high-value physical inventory (such as jewelry, electronics, or pharmaceuticals) or businesses with constant access to liquid cash (like retail or service sectors) will typically face higher premiums than professional services firms with lower tangible assets on-site. Past claims history is another factor; businesses that have filed previous claims for internal theft may be classified as “high risk,” potentially leading to higher premiums or more stringent coverage requirements.

    Best Practices to Prevent Employee Theft in the Workplace

    Relying solely on internal fraud insurance is a reactive strategy; proactive prevention should always be your first line of defense. A strong internal control environment not only discourages bad actors but also protects honest employees from being wrongly accused.

    1. Implement Segregation of Duties: Ensure that no single person is responsible for the entire lifecycle of a transaction. The person who authorizes an invoice should not be the one who signs the check, and the person who reconciles the bank statement should not be the person who makes the deposits.
    2. Mandatory Vacation Policies: Many embezzlers are caught because they are unable to keep their fraudulent schemes going while they are away from the office. Forcing employees in sensitive financial roles to take consecutive vacation time allows other team members to step in and potentially uncover inconsistencies.
    3. Background Checks: A thorough pre-employment screening process remains one of the most effective tools for risk mitigation. While it does not guarantee honesty, it signals to prospective hires that the organization takes security seriously.
    4. Audit Trails and Technology: Use modern accounting software that provides immutable audit trails. Every change made to an account should be logged with a timestamp and user ID. Periodically review these logs to check for unusual activity or unauthorized edits.
    5. Whistleblower Procedures: Create an anonymous reporting mechanism where employees can voice concerns about suspicious financial activities without fear of retaliation. Many instances of fraud are first identified by observant coworkers.

    Steps to Filing a Claim for Employee Dishonesty

    If the unthinkable happens and you suspect internal theft, the process of filing a claim must be handled with precision. A mishandled internal investigation can jeopardize your insurance payout. Follow these steps to maximize your chances of a successful recovery.

    Step 1: Secure the Environment. Once fraud is suspected, immediately restrict the employee’s access to company systems, physical cash, and sensitive documents. Do not alert the suspect until you have preserved the evidence. If the evidence is digital, contact an IT professional to create forensic images of the systems involved.

    Step 2: Document Everything. Assemble a detailed file of the suspicious activity. Include canceled checks, bank statements, invoices, and a narrative explaining how the fraud was committed. The more thorough your documentation, the faster the claims adjuster can verify the loss.

    Step 3: Consult Legal Counsel and Law Enforcement. Before making accusations, consult with an employment attorney to understand your rights and the potential for wrongful termination lawsuits. Furthermore, most insurance policies require you to file a police report for criminal activity. This serves as formal evidence that a crime has occurred.

    Step 4: Notify Your Insurer Promptly. Every policy has a “notice of loss” provision. Failure to report a potential claim within the specified timeframe can lead to a denial of coverage. Call your broker or insurance carrier as soon as you have confirmed that a loss has occurred.

    Step 5: Cooperate with the Adjuster. The insurer will conduct their own investigation to verify the amount of the loss. Be prepared to provide access to your financial records and answer questions transparently. Maintain professional communication throughout the process and keep a record of all correspondence.

    Frequently Asked Questions

    Is employee dishonesty insurance mandatory for all businesses?

    In most jurisdictions, there is no government-mandated requirement to carry specific employee dishonesty insurance. However, some industry regulators, commercial lenders, or clients may require you to maintain a fidelity bond or specific crime coverage as a condition of your contracts or lending agreements.

    What exactly does “loss of money” mean in an insurance policy?

    In the context of internal fraud insurance, “money” typically refers to currency, coins, and bank notes. Coverage often extends to “securities” as well, which includes stocks, bonds, and other financial instruments. It is essential to review your specific policy definition, as some policies may exclude certain types of virtual currencies or digital assets unless explicitly added via endorsement.

    Can I get coverage for theft committed by an independent contractor?

    Standard employee dishonesty policies are generally restricted to direct employees. If your business relies heavily on independent contractors or temp agency staff, you may need to request a policy extension or a specific rider that includes these individuals under the definition of “employee” for insurance purposes.

    What if I am not sure if a loss was caused by theft or a mistake?

    Insurance claims require proof that the loss was the result of a dishonest act. If the loss was caused by simple negligence or clerical error, your policy may not respond. However, it is still advisable to report the incident to your insurance provider so they can assist in determining whether a formal claim is appropriate.

    How does “discovery period” affect my insurance claim?

    The discovery period refers to the time frame after a policy expires during which you can still report a loss that occurred while the policy was active. Understanding your policy’s discovery period is vital, as internal embezzlement is often hidden for years before it is eventually discovered.

    Do I need an audit before I can get an insurance policy?

    While many insurers do not strictly require a formal, expensive audit by an outside CPA to bind a standard policy, they may request your most recent financial statements. For larger businesses seeking high limits of coverage, an insurer might mandate an annual audit as a condition of the policy’s renewal.

    Conclusion

    Protecting your business from the internal threat of embezzlement is not just a financial decision; it is an act of stewardship for your organization, your stakeholders, and your employees. While you hope to never need it, employee dishonesty insurance provides a critical safety net when the people you trust cross the line. By assessing your risks, hardening your internal controls, and selecting a comprehensive policy that fits your operational reality, you build a foundation of resilience that keeps your business moving forward.

    Don’t wait for a financial crisis to realize your coverage gaps. Take the time today to review your current policy, perform a mock audit of your internal procedures, and consult with a qualified insurance broker to ensure your business assets are fully protected. Your peace of mind is worth the investment.

    By insureiqguru Editorial Team

  • Cybersecurity Insurance Extensions: What Extras Should You Add?

    Cybersecurity Insurance Extensions: What Extras Should You Add?

    Key Takeaways

    • Standard cyber insurance often carries significant exclusions that may leave your business vulnerable to modern threats.
    • Social engineering and wire transfer fraud frequently require specific policy endorsements to trigger meaningful coverage.
    • Distinguishing between extortion coverage and business interruption is vital for financial recovery during a ransomware event.
    • Regulatory fines and penalties are often capped or excluded; proactive policy mapping is essential for compliance protection.
    • Customizing your cyber insurance extensions is a core component of a modern, comprehensive cyber risk management strategy.

    In the rapidly shifting landscape of global digital threats, businesses are increasingly realizing that a one-size-fits-all approach to risk management is a recipe for catastrophe. While many organizations invest in foundational protection, they often discover too late that their baseline coverage contains critical blind spots. Relying on a standard policy without considering cyber insurance extensions is akin to purchasing a high-end vehicle but leaving the windows open in a thunderstorm; the core protection exists, but it fails to account for the most common ways water actually gets inside. As threat actors evolve from simple malware deployment to sophisticated multi-vector attacks, securing your organization requires a nuanced understanding of cyber liability endorsements and strategic policy add-ons. In this guide, the InsureIQGuru Editorial Team explores how to bridge these common cyber insurance coverage gaps to ensure your business remains resilient in the face of ever-present digital volatility.

    Understanding the Limits of Standard Cyber Insurance Policies

    The misconception that a “comprehensive” cyber insurance policy covers every conceivable digital loss is one of the most dangerous myths in modern risk management. Standard policies, often labeled as “Cyber Liability” or “Network Security Insurance,” are designed to provide a baseline of protection, typically focusing on third-party liability—such as the legal costs associated with a data breach—and some first-party response costs like forensic investigation and notification services. However, these baseline policies often operate under rigid definitions and narrow scopes that fail to reflect the complexity of modern business operations.

    One of the most frequent areas where standard policies fall short is in the realm of operational nuances. For example, many base policies contain “silent cyber” exclusions or limitations that only trigger when a specific, narrowly defined “security failure” occurs. If a breach is caused by a human error that technically falls outside the narrow definition of a “network security incident,” an insurer might deny the claim. This creates a significant gap between the business’s expectation of protection and the actual legal reality of the policy language.

    Furthermore, standard network security insurance policies often place strict sub-limits on key services. While they may pay for the immediate legal fees following a breach, the sub-limit for forensic accounting, public relations management, or the physical replacement of corrupted hardware might be insufficient to cover the actual costs of a major incident. In a mid-market organization, a $50,000 sub-limit for public relations might seem adequate during the underwriting process, but when a high-profile breach requires a weeks-long national media campaign to protect brand equity, that limit vanishes in days.

    Another area of limitation involves the definition of “protected systems.” Standard policies are often written to protect the internal server architecture owned and operated by the business. However, as organizations migrate to cloud-native infrastructures and software-as-a-service (SaaS) environments, the line between what the business controls and what the service provider manages becomes blurred. If a service provider experiences an outage or a breach, the standard policy may offer little to no coverage for the resulting business interruption unless a specific extension for “contingent business interruption” is explicitly added to the policy.

    Effective cyber risk management requires a granular audit of your policy’s “Exclusions” section. Every standard policy includes boilerplate exclusions for things like “prior acts,” “intentional damage,” or “infrastructure failure” (such as a widespread power grid outage). While these are industry standards, the lack of affirmative extensions to cover these events can leave a business essentially uninsured during a large-scale event. To mitigate these risks, businesses must shift from a passive “buy-and-forget” approach to an active, iterative strategy of evaluating cyber policy add-ons that align with the specific digital infrastructure and threat profile of their industry.

    Policy Option Primary Function Best For
    Standard Cyber Liability Covers third-party legal costs and basic forensics. Small firms with minimal data exposure.
    Social Engineering Endorsement Covers financial loss from deceptive emails/phishing. Companies with high-volume accounts payable.
    Business Interruption Extension Replaces lost revenue during system downtime. E-commerce and cloud-dependent businesses.
    Extortion/Ransomware Rider Covers ransom payments and negotiation costs. Organizations with sensitive, high-value data.

    Social Engineering Fraud: Why It Needs a Separate Endorsement

    One of the most persistent threats facing modern enterprises is social engineering—the psychological manipulation of employees to divulge confidential information or authorize fraudulent financial transactions. Unlike a traditional “hack,” where a perpetrator bypasses a firewall or exploits a software vulnerability, social engineering exploits the most unpredictable variable in the security equation: human psychology. Because these attacks often involve authorized employees inadvertently “opening the door” for criminals, they frequently fall outside the coverage scope of standard cyber policies.

    In many standard policies, a claim is only triggered if there is an “unauthorized access” or a “security failure” resulting from an outside infiltration. However, in a classic Business Email Compromise (BEC) scenario, an attacker might pose as a legitimate vendor or CEO and request an urgent wire transfer. The employee, believing the request is genuine, authorizes the payment voluntarily. Because the employee technically had the authorization to move those funds, and the system did not suffer a “technical breach” in the traditional sense, many insurers classify this as a voluntary transfer of funds rather than a cyber-theft. Without a specific social engineering fraud endorsement, the resulting financial loss is often unrecoverable under the core policy.

    The prevalence of this threat has made the social engineering endorsement a non-negotiable component of modern business data breach protection. When evaluating this extension, business leaders must look for key language regarding the scope of coverage. Does the endorsement cover only wire transfers, or does it include other forms of payment fraud, such as ACH transactions or even the release of sensitive data? The most comprehensive endorsements cover the loss of funds even when the fraud is sophisticated enough to mimic legitimate internal protocols perfectly.

    Furthermore, businesses should be aware of the “pre-loss” requirement found in many of these add-ons. Insurers may require the organization to have specific internal controls in place, such as a “two-person rule” for financial transactions or verified callback procedures, before they will pay out on a claim. If an organization suffers a social engineering loss but lacks these mandated internal controls, the insurer may decline the claim despite the existence of the endorsement. Therefore, the endorsement acts not only as financial protection but also as a catalyst for tighter internal governance and cyber risk management.

    Implementing a social engineering extension also requires an assessment of the “Social Engineering Limit.” Because these attacks are frequent and often result in significant cash outflows, insurers may be more conservative with these limits than with other coverages. It is not uncommon to see a lower sub-limit for social engineering compared to the overall policy aggregate. Organizations should determine their maximum possible loss from a single, high-level fraudulent instruction and ensure their endorsement limit is calibrated to cover that worst-case scenario, rather than relying on the insurer’s default, lower-tier offering.

    Finally, consider the human element of your security training. A robust social engineering endorsement should be viewed as a safety net that complements, rather than replaces, ongoing security awareness training. While the insurance provides the financial backstop, the ultimate goal of any organization should be the prevention of the fraud before the transfer is initiated. A healthy policy is one that you hope never to trigger, providing the peace of mind to innovate while knowing the organization is protected against the most deceptive of digital threats.

    Understanding Ransomware Deception and Extortion Coverage

    Ransomware has matured into a sophisticated industry, with threat actors utilizing “double extortion” tactics where data is not only encrypted—effectively paralyzing business operations—but also exfiltrated and threatened with public release. Standard insurance policies created five or ten years ago are often woefully inadequate for this reality. In the context of modern ransomware, simply restoring data from a backup is rarely enough to resolve the incident, as the threat of leaking proprietary client information creates a separate, ongoing liability. This is why ransomware deception and extortion coverage has become a cornerstone of contemporary cyber insurance.

    The primary function of this coverage is to address the costs associated with the extortion process itself. This includes the potential ransom payment, which is a highly complex and controversial topic in the insurance industry. Professional cyber insurers typically partner with specialized crisis management firms that conduct negotiations with threat actors. These firms attempt to verify the attackers’ intent, validate the decryption tool, and ensure the stolen data is truly deleted if a payment is made. An extortion endorsement provides the financial resources to engage these specialists and, depending on the policy language and local law, helps cover the cost of the ransom demand itself.

    However, the value of extortion coverage extends far beyond the raw payment of a ransom. It covers the costs of “forensic investigation into extortion,” which is a critical process for determining exactly what data was accessed. Often, an organization may believe they have been hit by a simple encryption attack, only for forensic experts to discover that sensitive customer data has been exfiltrated weeks prior. The extortion endorsement supports this investigative work, which is essential for meeting legal notification obligations in the event of a data breach. Without this specific coverage, the forensic costs associated with assessing the “extortion potential” of an incident can quickly spiral, potentially exhausting the base policy limits.

    Another often overlooked aspect of this coverage is the “reputation damage” protection that many extortion riders include. When a breach results in a public extortion attempt, the media fallout can be just as damaging as the operational downtime. Some high-end extortion extensions provide coverage for crisis communications experts and public relations campaigns designed to mitigate reputational damage, help retain client trust, and manage the narrative with stakeholders. For businesses that rely heavily on their reputation for data security, this facet of the coverage is often more valuable than the financial loss mitigation itself.

    It is also essential to scrutinize the definition of “extortion” within your cyber insurance extensions. Some policies strictly define extortion as a threat to encrypt or delete data. If your policy is this narrow, it might not trigger in cases where an attacker threatens to damage your reputation or sabotage your search engine rankings or partner relationships. Ensure that your endorsement definition is broad enough to cover “threats of harm to computer systems or proprietary information.” By taking a proactive, broad-stroke approach to your ransomware coverage, you ensure that your organization has the flexibility to handle the modern extortion playbook, which is rarely limited to simple data locking.

    Coverage for Regulatory Fines and Data Privacy Penalties

    As governments worldwide tighten data protection regulations, the cost of a data breach is no longer limited to technical remediation and PR management. It now includes the significant legal peril of regulatory investigations and potential fines. From the GDPR in Europe to various state-level privacy acts in the United States, the regulatory landscape is characterized by high, often mandatory, penalties for the mishandling of sensitive information. Consequently, a dedicated extension for regulatory fines and penalties has become a standard requirement for any organization holding customer data.

    Standard cyber policies often explicitly exclude “government fines and penalties” on the basis that these are considered “uninsurable” in some jurisdictions due to public policy concerns. However, many insurers now offer cyber liability endorsements that carve back coverage for these costs, provided they are legally insurable. It is critical to work with a broker who understands the interplay between your specific jurisdiction’s legal framework and the policy language. You need to know if your policy covers “civil penalties” specifically, and whether it includes the costs of defending against a government investigation before a fine is even assessed.

    The “defense costs” aspect of this coverage is arguably more important than the fine itself. Regulatory investigations are notoriously lengthy, document-intensive, and expensive. An investigation into a breach can involve high-priced cybersecurity legal counsel, data privacy experts, and forensic examiners working for months to document compliance efforts. Without a specific regulatory extension, these costs may be categorized as “general legal expenses,” which could be subject to lower sub-limits or not covered at all. A robust regulatory endorsement typically provides a separate limit for these legal expenses, ensuring that the investigative process does not drain the funds needed for business continuity.

    One common area of confusion is whether the policy covers “fines and penalties” that result from a failure to comply with established security standards, such as PCI-DSS (Payment Card Industry Data Security Standard). In the event of a breach involving credit card data, the merchant may be liable for heavy non-compliance fines imposed by payment brands or acquiring banks. These are not always considered “government fines,” but rather “contractual penalties.” A truly comprehensive cyber policy will include specific language to handle these contractual data privacy penalties, or it will clarify that such costs fall under the definition of “insured damages.” Failing to align these definitions can lead to a rude awakening when a payment processor presents a six-figure fine following a breach.

    Lastly, organizations should pay close attention to the “insurability” clause. In some regions, certain types of punitive damages are considered uninsurable by law, meaning even if your insurance policy says it covers them, the court may prevent the insurer from paying. While you cannot override the law with an insurance contract, you can ensure your policy includes “most favorable interpretation” or “choice of law” clauses that provide the best possible chance of coverage. By proactively addressing these regulatory exposure points, you demonstrate to both regulators and stakeholders that your organization takes data stewardship seriously, which can occasionally act as a mitigating factor during the investigation itself.

    Business Interruption vs Digital Asset Restoration Extensions

    In the aftermath of a major cyber event, two distinct types of financial loss emerge: the physical cost of fixing the mess, and the massive revenue loss from being unable to operate. A common error among businesses is treating “Business Interruption” and “Digital Asset Restoration” as one and the same. While they are both critical components of network security insurance, they serve very different purposes and require careful calibration through specific cyber insurance extensions.

    Digital Asset Restoration is the process of getting the “lights back on.” It covers the technical costs of restoring your systems to their pre-incident state. This includes hiring external IT professionals to scrub infected servers, reinstalling software, and potentially paying for data recovery services to reconstruct corrupted databases. Essentially, this is the cost to repair the hardware and software. It is a one-time expense designed to return the organization to a functional state. In modern cyber policies, this coverage is relatively straightforward, though it is vital to ensure that your limit accounts for the current complexity of your cloud and on-premise hybrid environment.

    Business Interruption, however, is far more complex. This coverage is designed to compensate for the “lost net profit” and “continuing operating expenses” that the business incurs while its systems are down. If your e-commerce platform is offline for three days, you are losing sales every hour. If your logistics software is compromised, you may be missing shipping deadlines, leading to contractual penalties. Business Interruption coverage is intended to fill this financial gap, keeping the business afloat while the IT team is busy with the “Digital Asset Restoration.”

    The distinction becomes critical when you consider the “Waiting Period” or “Deductible” applied to Business Interruption. Most policies include a waiting period, typically ranging from 8 to 24 hours, during which no coverage is triggered. If your business can lose a significant amount of revenue in less than 24 hours, a long waiting period is a massive, unaddressed financial risk. You should negotiate this window down to the absolute minimum required to stay solvent during a disruption.

    Furthermore, many businesses fail to account for “dependent business interruption.” This is the coverage that applies when a *third-party* service provider—like your cloud hosting provider or a crucial SaaS vendor—goes offline due to a cyber event, preventing your business from operating. Because you were not “hacked” yourself, a standard policy might not cover your revenue loss. An extension for dependent business interruption is essential for any modern company that relies on external digital ecosystems. It ensures that your income protection follows the data, regardless of where that data is physically stored or processed.

    When selecting these extensions, consider the “Indemnity Period.” This is the length of time for which the insurer will provide compensation for lost profits. While some policies offer a short 30-day window, a complex recovery process can take months, especially if data integrity issues persist. Businesses that require significant time to re-verify systems and recover customer trust should look for extensions that offer longer indemnity periods. Balancing these two extensions—restoration for the technical fix and interruption for the financial recovery—is the key to ensuring that a single incident does not lead to total business insolvency.

    The Importance of Media Liability Coverage for Online Content

    In the digital age, your business is a publisher. Whether you operate a blog, maintain active social media channels, or produce high-traffic e-commerce websites, you are constantly disseminating content. While many business owners assume that their general liability policy covers defamation or copyright infringement, the reality is that traditional policies often exclude digital media activities. This is where media liability coverage, often included as a cyber insurance extension, becomes essential.

    Media liability endorsements are designed to protect your organization against lawsuits arising from the content you publish online. This includes claims related to libel, slander, trade libel, and the unauthorized use of names or photographs. More importantly for digital-first businesses, this extension covers intellectual property infringement, specifically regarding the unauthorized use of titles, slogans, or trademarks in your digital marketing campaigns.

    Consider the risk of a “wrongful act” in electronic media. If your marketing team accidentally uses a licensed image without the proper permissions, or if an article published on your corporate site inadvertently defames a competitor, you could face significant litigation costs. Without this specific cyber policy add-on, your business might be forced to defend these claims out-of-pocket. The coverage gap is particularly wide for companies that rely on influencer marketing, user-generated content, or automated news feeds, where the potential for copyright errors scales rapidly.

    Furthermore, media liability coverage often extends to cover the costs of legal defense, settlement payments, and court-awarded damages. It acts as a safety net for the modern enterprise that engages in content-heavy marketing, ensuring that a single misstep in a blog post or social media update does not jeopardize the company’s financial stability. By integrating this into your cyber risk management strategy, you are effectively acknowledging that content creation is now a core business function that carries its own unique set of liability risks.

    Cloud Computing Downtime and Third-Party Provider Risks

    Modern business operations are rarely contained within a single server closet. They are dispersed across a complex ecosystem of Software-as-a-Service (SaaS) providers, cloud storage solutions, and infrastructure-as-a-service (IaaS) platforms. While outsourcing IT infrastructure to experts can improve your internal efficiency, it simultaneously introduces a critical dependency: third-party provider risk.

    If your primary cloud provider experiences a massive outage, your business continuity plan might be flawless, but your operations will still come to a screeching halt. Many standard cyber policies offer limited protection for “business interruption,” but they often strictly define this as interruption caused by a cyberattack on your network. If the outage occurs at your provider’s data center due to a glitch, a cyberattack on their system, or a physical fire, standard policies may not provide the necessary coverage.

    To bridge this gap, you should consider a “Dependent Business Interruption” extension. This specific cyber liability endorsement provides coverage for lost income and increased expenses if a critical third-party service provider suffers a network outage that prevents you from conducting business. This is crucial for businesses that utilize CRM systems, payment gateways, or supply chain management platforms that are hosted externally.

    When evaluating these extensions, it is important to pay close attention to the definition of a “service provider” within the policy document. Does it include your web host? Your cloud-based accounting software? Your payroll processor? A comprehensive extension will cast a wide net, ensuring that when your digital backbone is compromised by a third party, your business retains the financial support required to survive the downtime.

    Extension Type Primary Coverage Focus Best For
    Dependent Business Interruption Lost income due to third-party cloud outages E-commerce and SaaS-reliant firms
    Media Liability Endorsement Copyright infringement and defamation claims Content creators and social media teams
    Hardware Failure Extension Software-induced physical server damage Manufacturing and IoT-heavy industries

    Physical Damage Extension: When Your Software Causes Hardware Failure

    The boundary between the virtual and the physical is dissolving. As businesses adopt the Internet of Things (IoT), automated manufacturing systems, and smart building management, the risk of a “cyber-physical” event increases. Traditionally, cybersecurity insurance has been limited to intangible data and information assets. However, what happens if a malicious code or a faulty software update causes a physical piece of machinery to overheat, catch fire, or suffer a catastrophic internal failure?

    Most commercial property insurance policies contain “cyber exclusions,” which specifically state that they will not cover damage if it is “caused by” or “arises from” a cyber incident. This creates a dangerous “coverage vacuum.” Your cyber policy covers the data loss, but your property policy denies the hardware claim because the damage was software-induced. This is the exact scenario where a Physical Damage Extension is required.

    This extension is critical for companies utilizing industrial control systems (ICS) or supervisory control and data acquisition (SCADA) systems. If a breach leads to an industrial turbine running at unsafe speeds until it breaks, you need insurance that acknowledges the direct link between the software breach and the physical repair cost. Without this, the cost of replacing specialized, high-value machinery could threaten the long-term solvency of the business.

    Securing this type of coverage often requires an audit of your physical infrastructure to demonstrate that you understand how your software interacts with your hardware. Insurers will want to see that you have implemented segmentation—a practice in cyber risk management that keeps your IT systems (servers/laptops) logically separated from your OT (Operational Technology) systems. By showing this level of diligence, you make a much stronger case for the inclusion of a physical damage endorsement.

    How to Evaluate Your Current Policy for Potential Coverage Gaps

    Evaluating your cyber policy should not be a “set it and forget it” task. As your business evolves, your risk profile changes, and your coverage should evolve in tandem. To conduct an effective gap analysis, you should start by pulling your Declarations Page and your full policy wording document. Do not rely solely on the summary provided by a broker; the specific exclusions are found in the fine print.

    First, identify your “critical assets.” Where does your revenue come from? If you have moved your primary sales platform to a cloud provider, ensure your policy has the aforementioned Dependent Business Interruption coverage. If you have recently launched a brand-focused content strategy, double-check your media liability limits.

    Next, look for sub-limits. Many policies look robust at a glance, offering, for example, $5 million in total coverage. However, they may cap “Social Engineering Fraud” or “Ransomware Payments” at $100,000. These sub-limits can be deceptive, as a ransomware event often costs far more than a simple data recovery exercise. Compare these sub-limits against your internal data valuation estimates.

    Finally, engage in a “threat scenario” exercise. Work with your IT security team to identify the top three risks your company faces—such as a ransomware lockout, a third-party vendor failure, or a regulatory fine for a data breach. Once you have these scenarios, ask your broker specifically: “If this exact event happened tomorrow, which policy covers the cost of the ransom, the forensic investigation, the legal notifications, and the resulting downtime?” If the answer is “maybe” or “it depends,” you have identified a gap that needs to be addressed through a formal policy endorsement.

    Frequently Asked Questions

    Is business data breach protection the same as general cyber insurance?

    While often used interchangeably, business data breach protection is usually a narrower subset of comprehensive cyber insurance. It specifically covers costs related to a breach of sensitive information, such as credit card numbers or personal records. A full cyber liability policy is broader, covering not just breaches, but also ransomware events, business interruptions, and system damage.

    Do I really need cyber insurance if I use a reputable cloud provider?

    Yes. Reputable providers offer security, but they are not liable for your specific business loss in the event of an outage or a breach. Your contract with the cloud provider likely includes significant disclaimers of liability. Furthermore, a cloud breach can lead to regulatory investigations and customer lawsuits that are your responsibility to defend, regardless of the provider’s role.

    What are cyber liability endorsements?

    Cyber liability endorsements are specific modifications to your standard policy language. They essentially act as “add-ons” that extend coverage to include scenarios that were previously excluded or under-insured. These allow companies to tailor their policy to match their unique operational risks, such as adding coverage for physical hardware damage or social engineering losses.

    How does a network security insurance policy handle ransomware payments?

    Most modern cyber policies include coverage for “Extortion Expenses,” which can help facilitate the payment of a ransom if a forensic analysis determines it is the only viable path to restoration. However, these policies typically require the business to involve law enforcement and follow specific protocols, such as using specialized ransom negotiation firms approved by the insurer, to qualify for reimbursement.

    What is the biggest coverage gap businesses overlook?

    The most common overlooked gap is the “contingent” or “dependent” business interruption. Many businesses are fully protected if their own server goes down, but they fail to realize that if their third-party software provider, payroll processor, or logistics platform goes offline, they have no insurance for the resulting lost revenue. This is a critical vulnerability for digital-first businesses.

    How often should I review my cyber policy add-ons?

    Experts generally agree that you should review your cyber policy at least annually, or immediately following any significant shift in your business operations. This includes changing your cloud service providers, moving into a new industry, significantly increasing your digital marketing efforts, or integrating new IoT hardware into your office environment.

    Conclusion

    Navigating the complex landscape of cybersecurity insurance requires more than just buying the first policy offered to you. It demands a proactive approach to risk management, a clear understanding of your operational dependencies, and a willingness to tailor your policy using essential cyber insurance extensions. As we have explored, the digital environment is fraught with risks—from media liability and third-party downtime to the emerging dangers of software-induced physical failures.

    The cost of a cyber incident is rarely limited to the immediate data loss; it ripples through your business in the form of operational downtime, legal fees, and reputational damage. By closing the coverage gaps in your current policy, you are not just purchasing an insurance product; you are investing in the resilience and longevity of your organization. Do not wait for an incident to occur to discover what your policy covers—conduct your audit today, speak with your risk advisor, and ensure your business is truly prepared for the challenges of the modern digital era.

    Ready to strengthen your digital defense? Reach out to our expert team for a comprehensive policy audit and tailored risk management strategy. Secure your future before the next threat arrives.

    By insureiqguru Editorial Team

  • Captive Insurance: Is It Worth It for Your Business in 2026?

    Captive Insurance: Is It Worth It for Your Business in 2026?

    Key Takeaways

    • Captive insurance acts as a formal, regulated self-insurance strategy designed to provide businesses with more control over their risk management.
    • In 2026, firms are increasingly turning to captives to stabilize volatile commercial premiums and insure “uninsurable” business risks.
    • There are various structures, including single-parent and group captives, each requiring specific capitalization and regulatory compliance.
    • The core benefit of a captive model is the alignment of risk management incentives, which can lead to significant long-term cost savings.
    • Transitioning to a captive requires a comprehensive feasibility study to ensure the business meets financial and structural requirements.

    As the landscape of global risk continues to shift rapidly, business leaders are finding that traditional insurance products are no longer a catch-all solution for operational volatility. In 2026, the conversation around corporate risk management has pivoted from merely buying protection to owning it. For many mid-to-large-scale enterprises, the question is no longer whether they can afford to take on more risk, but whether they can afford to continue paying commercial carriers for coverage that fails to address their specific exposures. Enter the captive insurance model—a strategic approach that has evolved from a niche financial tool for the ultra-wealthy into a cornerstone of proactive business resilience. Whether you are facing rising premium cycles, unique liability risks, or a desire for greater financial control, understanding the complexities of a captive insurance program is essential for any modern executive planning for the next decade of growth.

    What Is Captive Insurance and How Does It Work?

    At its core, what is captive insurance if not a formalized mechanism for self-insurance? A captive insurance company is essentially a licensed insurance entity established by a parent organization—or a group of organizations—with the primary purpose of insuring the risks of its owners. Unlike a traditional insurance company that sells policies to the general public, a captive is a “closed shop.” It exists solely to fund the risks of the business (or businesses) that created it.

    The operational mechanics are straightforward yet highly regulated. The parent company provides capital to the captive to meet minimum regulatory standards set by the domicile—the jurisdiction in which the captive is formed. Once operational, the captive issues policies to the parent company, charging premiums just as a commercial carrier would. The difference lies in where those premiums go. Instead of leaving the organization to pad the profits of a third-party insurer, the premiums remain within the parent company’s financial ecosystem. If the captive experiences a “good year” with few claims, the profit stays within the structure rather than being lost to external market cycles.

    There are several critical components that make this structure functional. First, there must be a genuine transfer of risk. Regulatory bodies are vigilant about ensuring the captive is not merely a tax-avoidance vehicle; it must function as a legitimate insurer. This means the captive must have the financial strength to pay claims and must be operated by professional underwriters and service providers. The captive typically works with a fronting carrier in certain jurisdictions, which issues the “paper” (the actual insurance policies) to satisfy local requirements or contractual obligations, while the captive takes on the underlying risk through a reinsurance agreement.

    This self-insurance strategy allows a business to customize its coverage. Commercial policies are often “off-the-shelf,” meaning they include exclusions that may leave critical gaps for your specific industry. A captive allows you to draft manuscript policies tailored to your operational realities. If your company has a unique supply chain risk or a specific liability that standard insurers refuse to cover at a reasonable cost, the captive can bridge that gap. By taking ownership of the risk, the organization also gains access to the investment income generated by the reserves held within the captive. This circular flow of capital—collecting premiums, managing investment funds, and paying out claims—transforms risk management from a pure cost center into a potential profit center. Ultimately, the captive acts as a financial buffer, smoothing out the peaks and valleys of premium costs and providing a sophisticated tool for long-term capital retention.

    The Growing Popularity of Captive Insurance in 2026

    The year 2026 marks a turning point for captive insurance, driven by an era of unprecedented market volatility. Over the past several years, organizations across almost every sector have faced the “hard market” phenomenon, where commercial insurance premiums spiked, coverage limits were slashed, and certain risks became altogether uninsurable. As commercial carriers tightened their underwriting criteria to protect their own balance sheets, many businesses found themselves exposed, paying significantly more for less coverage. This frustration with traditional models has propelled the benefits of captive insurance to the forefront of corporate boardroom agendas.

    Technology and data analytics have further accelerated this trend. In the past, the logistical burden of running a captive—managing claims, actuarial modeling, and regulatory filings—was often too heavy for mid-sized firms. Today, the integration of real-time risk data and streamlined domicile administration has lowered the barrier to entry. Businesses can now model their loss history with greater precision, making the decision to move to a captive a data-driven one rather than a leap of faith. Experts generally agree that as companies become more complex and their risk profiles more idiosyncratic, the “one-size-fits-all” approach of legacy insurers has become obsolete.

    Furthermore, the focus on ESG (Environmental, Social, and Governance) and cyber resilience has pushed captives into the limelight. Standard commercial policies often lack the nuance to account for specific ESG-related liabilities or the rapid, evolving nature of cyber-attacks. Captives provide the flexibility to cover these emerging risks, allowing firms to build a “war chest” specifically for the threats they fear most. This self-reliance fosters a culture of risk management; when a company owns the risk, every department within the organization becomes more incentivized to implement safety protocols and loss-prevention measures. This “skin in the game” effect results in fewer losses over time, which reinforces the financial viability of the captive.

    We are also seeing a resurgence in group captives, where non-competing businesses come together to form a mutual captive. This model allows smaller enterprises to enjoy the benefits of a captive—such as loss-sensitive pricing and investment income—without bearing the full financial burden of a single-parent structure. The collaborative nature of these groups, often facilitated by seasoned captive managers, provides a community of shared risk expertise. As we navigate the complex economic environment of 2026, the movement toward self-insurance is no longer a fringe strategy; it is a sophisticated method for businesses to reclaim their autonomy, reduce volatility, and secure their financial future against the unpredictability of the commercial marketplace.

    Types of Captive Insurance Structures Explained

    Selecting the right structure is a pivotal step when considering a self-insurance strategy. There is no singular model that fits every organization; rather, the structure should be dictated by the company’s capital, risk profile, and long-term business goals. The primary distinction lies in ownership and the number of entities involved in the captive.

    A Single-Parent Captive (or Pure Captive) is established by one parent company to cover its own risks. This is the gold standard for large corporations with significant risk volume. Because the captive is exclusively focused on the parent company, it offers the greatest level of control and customization. The parent can dictate every aspect of the policy language and underwriting, allowing for the precise coverage of highly specific, niche risks that no commercial carrier would ever touch. However, the capital requirements are typically higher, as the captive must maintain sufficient solvency ratios to satisfy the regulators of its chosen domicile.

    On the other side of the spectrum are Group Captives, also known as Association Captives. These are formed by a group of companies—often within the same industry or trade association—to pool their risks. This structure is ideal for mid-sized firms that may not have the capacity to launch a single-parent captive on their own. By pooling premiums and losses, these businesses can achieve economies of scale and access sophisticated reinsurance markets. The risks are shared, which provides a degree of stability, though it requires a high level of trust and cooperation among the participating members.

    Another popular option for businesses seeking a lower barrier to entry is the Cell Captive (or Protected Cell Company). This structure involves a core entity that provides the license, capital, and infrastructure for multiple independent “cells.” Each cell is legally segregated, meaning the assets and liabilities of one cell are protected from the risks of another. This allows a business to enjoy the benefits of a captive model with significantly lower setup costs and administrative burdens. It is essentially a “captive-as-a-service” approach, perfect for companies dipping their toes into the water of self-insurance.

    Finally, we see Agency or Producer-Owned Captives, which allow insurance agencies to participate in the underwriting profit of the policies they write. This alignment of incentives can encourage better risk selection and more focused loss prevention. Regardless of the structure, the choice depends on the organization’s appetite for risk, its current premium spend, and its long-term commitment to managing its own risk. Understanding these structures is the foundation of any captive insurance requirements assessment, as the chosen domicile and the regulatory landscape will vary based on the model selected.

    Structure Type Key Advantage Best For
    Single-Parent Maximum autonomy and customization Large firms with high premium volume
    Group Captive Shared costs and pooled risk Mid-sized industry peers
    Cell Captive Low startup cost and flexibility Smaller entities/newcomers

    Key Benefits: Why Businesses Move to Captive Models

    The decision to shift toward a captive model is rarely driven by a single factor; it is almost always a strategic response to the shortcomings of the commercial insurance market. One of the most frequently cited benefits of captive insurance is the ability to bypass the “market cycle.” Commercial insurance is notorious for its pendulum swings—periods of soft markets with low premiums followed by hard markets characterized by massive rate hikes and restrictive coverage. By creating a captive, a business effectively builds a buffer against these fluctuations. The captive acts as a stabilization fund, ensuring that your insurance costs are based on your actual, historical performance rather than the broader, often irrational, trends of the global insurance industry.

    Another powerful incentive is the potential for improved risk management incentives. In a traditional commercial model, the insurance carrier is the one that benefits when your claims are low. Conversely, the company has little to show for its stellar safety record other than perhaps a minor discount on next year’s premium. In a captive, the financial incentives are perfectly aligned. Because the captive belongs to the business, any underwriting profit—the difference between the premiums collected and the claims paid—remains on the balance sheet. This creates a direct, tangible financial incentive for management to prioritize loss control, safety training, and risk mitigation. When the organization knows that a lower loss ratio directly translates into higher retained earnings, a culture of safety often develops organically from the C-suite down to the frontline workers.

    Captives also provide access to wholesale reinsurance markets. Commercial carriers often place a significant markup on premiums to cover their administrative costs, overhead, and profit margins. A captive can negotiate directly with reinsurers, often securing coverage at a much lower cost than retail insurance. By bypassing the layers of commission and brokerage fees inherent in commercial markets, the organization can achieve significant cost savings over the long term. This is especially true for companies with a proven track record of managing risks effectively, as they are essentially “self-insuring” their predictable losses and using the captive to transfer only the catastrophic, high-impact risks that would threaten their solvency.

    Finally, the administrative flexibility of a captive cannot be overstated. Standard policies are filled with boilerplate language and exclusions that may not protect against the nuances of your business. A captive allows for the creation of manuscript policies that provide bespoke coverage. This is particularly valuable for businesses facing emerging threats, such as supply chain disruptions, intellectual property litigation, or specialized environmental liabilities. Instead of paying for a bundled package of coverage that includes risks you don’t face, you can tailor your captive to cover only what you need. This precision eliminates the “coverage gaps” that often leave businesses exposed even when they think they are fully protected. By gaining this level of control, a business effectively transforms its insurance program from a passive expense into an active, strategic asset that supports long-term operational goals.

    Captive Insurance vs Commercial Insurance: Key Differences

    When comparing captive insurance vs commercial insurance, the fundamental difference is the locus of control. Commercial insurance is a retail transaction; you are a consumer purchasing a product. You accept the terms, conditions, and pricing set by the carrier, and you are subject to the carrier’s claims-handling process. In contrast, captive insurance is an act of ownership. You are not buying a policy from a third party; you are establishing the policy, setting the terms, and overseeing the claims adjudication process through your own entity.

    The pricing model is perhaps the most visible distinction. Commercial premiums are priced based on the carrier’s broader book of business, meaning your premium may rise because of losses experienced by other companies in your industry or geographical region. You are paying for the carrier’s overhead, shareholder returns, and the losses of the “average” insured firm. With a captive, your premiums are primarily driven by your own company’s loss experience. If your organization implements robust risk management, your captive premiums will eventually reflect those improvements. This creates a level of cost predictability that is simply unattainable in the commercial world.

    Coverage scope is another area where the two models diverge sharply. Commercial insurance is designed for the mass market, and as such, it must be standardized to be profitable and manageable at scale. This standardization inherently results in limitations—coverage is often capped, and exclusions are widespread to keep the carrier’s exposure predictable. A captive, conversely, is built for the specific needs of the parent company. It can cover risks that are difficult to insure or completely “uninsurable” in the commercial market. Whether it is a unique operational risk, a specific type of cyber liability, or a specialized warranty, the captive allows the organization to define the policy boundaries, ensuring that protection is exactly where it is needed.

    Claims handling is also drastically different. In a commercial model, the claims process is designed to protect the insurance company’s bottom line, which can sometimes lead to adversarial relationships and long, drawn-out disputes. In a captive model, the parent organization typically employs its own third-party administrator (TPA) to manage claims according to the firm’s specific customer service standards. Because the captive is interested in both the fair treatment of claimants and the long-term health of the business, the process is often more efficient and aligned with the company’s broader reputation and retention goals. When you own the captive, you control the claims outcome, ensuring that disputes are settled in a way that aligns with your company’s values and business relationships, rather than just the carrier’s legal strategy.

    Lastly, the long-term financial impact is the ultimate differentiator. Commercial premiums are a sunk cost; once the premium is paid, it is gone. In a captive, the premiums remain within the organization, growing through investment income. Over several years, a well-managed captive can build a reserve fund that serves as a critical financial cushion during economic downturns. This shift from an expense-heavy approach to an asset-building strategy is why so many forward-thinking businesses are reconsidering their relationship with traditional insurance. While a captive requires more upfront commitment and administrative rigor, the ability to control one’s own risk destiny is a benefit that commercial models will never be able to replicate.

    The Regulatory and Financial Requirements for Captives

    Establishing a captive insurance company is a significant financial undertaking that moves a business from being a passive purchaser of insurance to an active participant in the risk management ecosystem. Because a captive functions as a licensed insurance entity, it must adhere to the stringent regulatory oversight of the jurisdiction in which it is domiciled. These requirements are designed to ensure the entity remains solvent and capable of fulfilling its obligations to pay claims.

    Financial capitalization is the cornerstone of regulatory compliance. Every jurisdiction mandates a minimum capital and surplus requirement. These funds are held in reserve to ensure the captive can meet potential claim liabilities. While the specific dollar amount varies significantly based on the type of captive—such as a pure captive, a group captive, or a cell captive—the capital must typically be in the form of cash, irrevocable letters of credit, or other highly liquid, investment-grade assets. Regulators are often cautious, and they will scrutinize the “source of funds” to ensure the capital is genuine and not borrowed against the business’s primary operational cash flow in a way that undermines the captive’s stability.

    Beyond capital, the business must satisfy rigorous licensing procedures. This involves filing a detailed feasibility study that outlines the business plan, the specific risks to be insured, the proposed reinsurance arrangements, and the financial projections for the next three to five years. Regulators will also conduct a “fit and proper” test on the proposed management team, board of directors, and service providers. This ensures that the individuals steering the captive have the insurance expertise required to navigate underwriting, actuarial analysis, and claims management.

    Reporting requirements are ongoing. A captive must produce audited financial statements annually, prepared by an independent accounting firm that specializes in insurance. Many domiciles also require an annual actuarial opinion to confirm that the reserves held for unpaid losses are adequate. Compliance is not a one-time hurdle; it is a permanent operational commitment. Failure to meet these financial and reporting standards can lead to the revocation of the captive’s license, essentially forcing the business to unwind the structure and revert to the commercial market, often at a significant loss of time and capital.

    Common Risks Associated with Captive Insurance

    While the benefits of captive insurance are substantial, it is imperative for business leaders to recognize that this is a risk transfer strategy, not a risk elimination strategy. By forming a captive, a business is essentially choosing to own its risk rather than offload it to a commercial carrier. This transition introduces several critical risks that require careful management.

    The primary risk is underwriting risk. In the commercial market, insurers use massive pools of data to price premiums. A captive, especially in its early years, may not have the same breadth of actuarial data. If the business underestimates the frequency or severity of a particular loss, the captive’s surplus can be quickly depleted. This necessitates conservative underwriting practices and a robust reinsurance program, often referred to as “excess of loss” coverage, which acts as a safety net if a catastrophic claim exceeds the captive’s capacity.

    Another significant risk is operational risk. Running a captive requires a sophisticated team, including a captive manager, legal counsel, and tax advisors. If the business lacks the internal expertise to oversee these vendors effectively, the captive can fall victim to administrative mismanagement. This includes errors in tax filing, failures in regulatory reporting, or lapses in the legal documentation of policies, all of which could trigger audits or penalties from tax authorities like the IRS, particularly concerning the “risk distribution” and “risk shifting” requirements necessary for the IRS to recognize the captive as an insurance company for tax purposes.

    Finally, there is the concentration risk. Commercial insurers thrive by diversifying across many different clients and geographies. A single-parent captive is inherently concentrated in the risks of one business. If that business experiences a catastrophic event that wipes out both its physical assets and its liquidity, the captive structure may also fail. This is why many organizations opt for cell captives or group captives, which allow businesses to share risk and diversify their exposure, thereby mitigating the volatility that can destroy a small, stand-alone captive.

    Is Your Business Large Enough for a Captive?

    The “size” of a business is often a misunderstood metric in the captive conversation. It is less about revenue and more about the quality and quantity of predictable, uninsurable, or overpriced commercial risks. That said, there is a “soft floor” where the costs of forming and maintaining a captive outweigh the potential savings.

    Generally, businesses that spend less than a certain threshold on annual commercial insurance premiums—often cited by experts as falling in the range of $250,000 to $500,000—may find that a captive is not economically viable. The fixed costs associated with captive management, accounting, actuarial fees, and regulatory filings can erode the premium savings for companies beneath this size.

    However, size should also be measured by loss history. A company with a very low loss ratio (where they pay far more in premiums than they ever receive in claims) is a prime candidate, as they are essentially “self-insuring” their own profits through the commercial market. Conversely, a high-growth company with specialized risks that are difficult to place in the standard market (e.g., cyber risk, supply chain interruption, or proprietary manufacturing liability) may find a captive valuable even if their total insurance spend is relatively modest.

    Company Profile Suitability for Captive Best For
    Small, Low-Risk Business Low Traditional Commercial Policies
    Mid-Market, Stable Loss Record Moderate Cell Captive / Rent-a-Captive
    Large Enterprise, Complex Risks High Pure Single-Parent Captive
    Association/Industry Group High Group/Association Captive

    If your business exhibits a pattern of paying large, non-negotiable premiums for risks that rarely result in claims, or if you are constantly facing “insurance gaps” where commercial policies have broad exclusions, you have reached the size and maturity level where a captive strategy warrants a formal feasibility study.

    Step-by-Step Process to Forming a Captive Insurer

    The formation of a captive is a structured, project-managed process that typically takes between six to twelve months. It is not an overnight decision but rather a deliberate strategic shift.

    1. Feasibility Study: This is the most critical phase. You engage a professional captive consultant to analyze three years of loss data, current premium spend, and future risk exposure. The study determines if a captive will provide financial benefit and if the business has the appetite for the risks involved.
    2. Domicile Selection: You must choose a jurisdiction. Key factors include the domicile’s regulatory reputation, tax environment, availability of local service providers, and proximity to your corporate headquarters. Popular onshore domiciles in the U.S. include Vermont, Delaware, and South Carolina, while offshore options like Bermuda or the Cayman Islands remain prominent for global companies.
    3. Regulatory Application: Once a domicile is chosen, a formal business plan and license application are filed with the local Insurance Commissioner. This includes proof of capitalization and the appointment of a resident captive manager.
    4. Legal and Corporate Governance: You establish the corporate entity, draft the Articles of Incorporation and Bylaws, and appoint the Board of Directors. It is essential to ensure that the board has the independence and authority to act in the best interest of the captive.
    5. Operational Setup: You finalize contracts with third-party administrators (TPAs) for claims handling, auditors for financial review, and an investment manager for the captive’s capital reserves.
    6. Policy Issuance: Once licensed, the captive begins issuing policies to the parent company or group members. It will also begin paying reinsurance premiums to transfer excess risk, ensuring the captive maintains its own stability.

    Evaluating the Long-Term ROI of a Captive Strategy

    The ROI of a captive should not be viewed through the lens of a single year. It is a long-term capital management tool. In the first year, you will likely see a negative return due to the “startup costs,” which include legal fees, consulting fees, and initial licensing costs.

    The real ROI manifests in the reduction of the “leakage” inherent in commercial insurance. Every dollar you spend on a commercial premium contains an expense load—the insurer’s administrative costs, marketing budget, profit margin, and commissions. When you capture your own risk, those costs stay within your organization. If your loss history remains favorable, the capital that would have been kept by the insurance company remains in your captive, earning investment income and building a reserve that can eventually fund the company’s growth or cover previously uninsurable risks.

    Another layer of ROI is the cost of capital. By controlling your own insurance reserves, you effectively create a captive internal bank. While these funds must be invested conservatively, they provide the business with a buffer against economic downturns. When the commercial insurance market hardens—meaning premiums skyrocket and capacity dries up—the captive owner remains insulated. They are not beholden to the whims of the global reinsurance cycle, which can cause commercial insurance costs to fluctuate by double-digit percentages annually.

    Frequently Asked Questions

    What is the minimum amount of capital required to start a captive?

    Capital requirements vary wildly by jurisdiction and the complexity of the risks insured. While some small captive structures may be capitalized with as little as $250,000, larger or more complex operations will require millions. Regulators determine this amount based on a “solvency margin” calculation, ensuring the captive can handle unexpected loss volatility.

    Can a small business benefit from a captive, or is it only for corporations?

    While traditional single-parent captives require significant volume, small businesses can participate in group captives or cell captives. These allow multiple businesses to pool their risks, sharing the formation and administrative costs. This makes the benefits of captive ownership accessible to companies that wouldn’t meet the financial thresholds of an individual, stand-alone entity.

    What is the main difference between a captive and self-insurance?

    Self-insurance is an informal way to retain risk, usually through high deductibles. A captive is a formal, licensed insurance company. The key difference is that a captive is a regulated legal entity that allows you to formalize the funding of risks, potentially gain tax advantages on premiums paid, and access reinsurance markets that are otherwise unavailable to an individual business.

    Are premiums paid to a captive tax-deductible?

    The IRS maintains strict standards for tax deductibility. To be deductible, the captive must be recognized as an insurance company for tax purposes. This requires the presence of “risk distribution” and “risk shifting.” If a captive is used merely as a tax shelter without legitimate insurance risk, the IRS may disallow the deductions. Always consult with a tax attorney specializing in captive insurance before proceeding.

    What happens to the money in the captive if we have a great year with no claims?

    The money remains in the captive’s surplus. It grows through investment income and can be used to pay future claims, reduce future premium requirements, or, in some cases, be distributed to the shareholders (the parent business) as dividends, provided that the distribution does not compromise the captive’s financial solvency or violate local regulations.

    How does a “cell captive” differ from a standard captive?

    A cell captive, also known as a Protected Cell Company (PCC), allows a business to have its own “cell” within a larger, pre-existing insurance company. This provides many of the benefits of a captive—such as risk retention and control—without the high costs and lengthy setup time of forming a standalone entity. Each cell’s assets are legally protected from the liabilities of other cells within the same company.

    Conclusion

    Captive insurance represents a transition from a reactive insurance consumer to an empowered, proactive risk manager. While it is a sophisticated strategy that demands rigorous financial oversight, regulatory compliance, and a long-term commitment, the benefits—greater control over risk, insulation from commercial market volatility, and potential long-term cost savings—are substantial. For businesses that have outgrown the limitations of standard commercial insurance, a captive can serve as a powerful engine for financial stability.

    However, moving forward requires careful deliberation. The journey begins with an honest assessment of your current insurance landscape and a professional feasibility study. Whether you are a mid-market organization exploring cell captives or a large enterprise ready to establish a pure captive, the foundation of success lies in partnering with experienced advisors who can help you navigate the complexities of 2026’s evolving regulatory environment.

    Is your business ready to take ownership of its risks? Contact a qualified captive manager today to initiate a preliminary audit and discover if your current insurance profile qualifies for this transformative strategy.

    By insureiqguru Editorial Team